ABAC: When Data Context Becomes the Access Rule
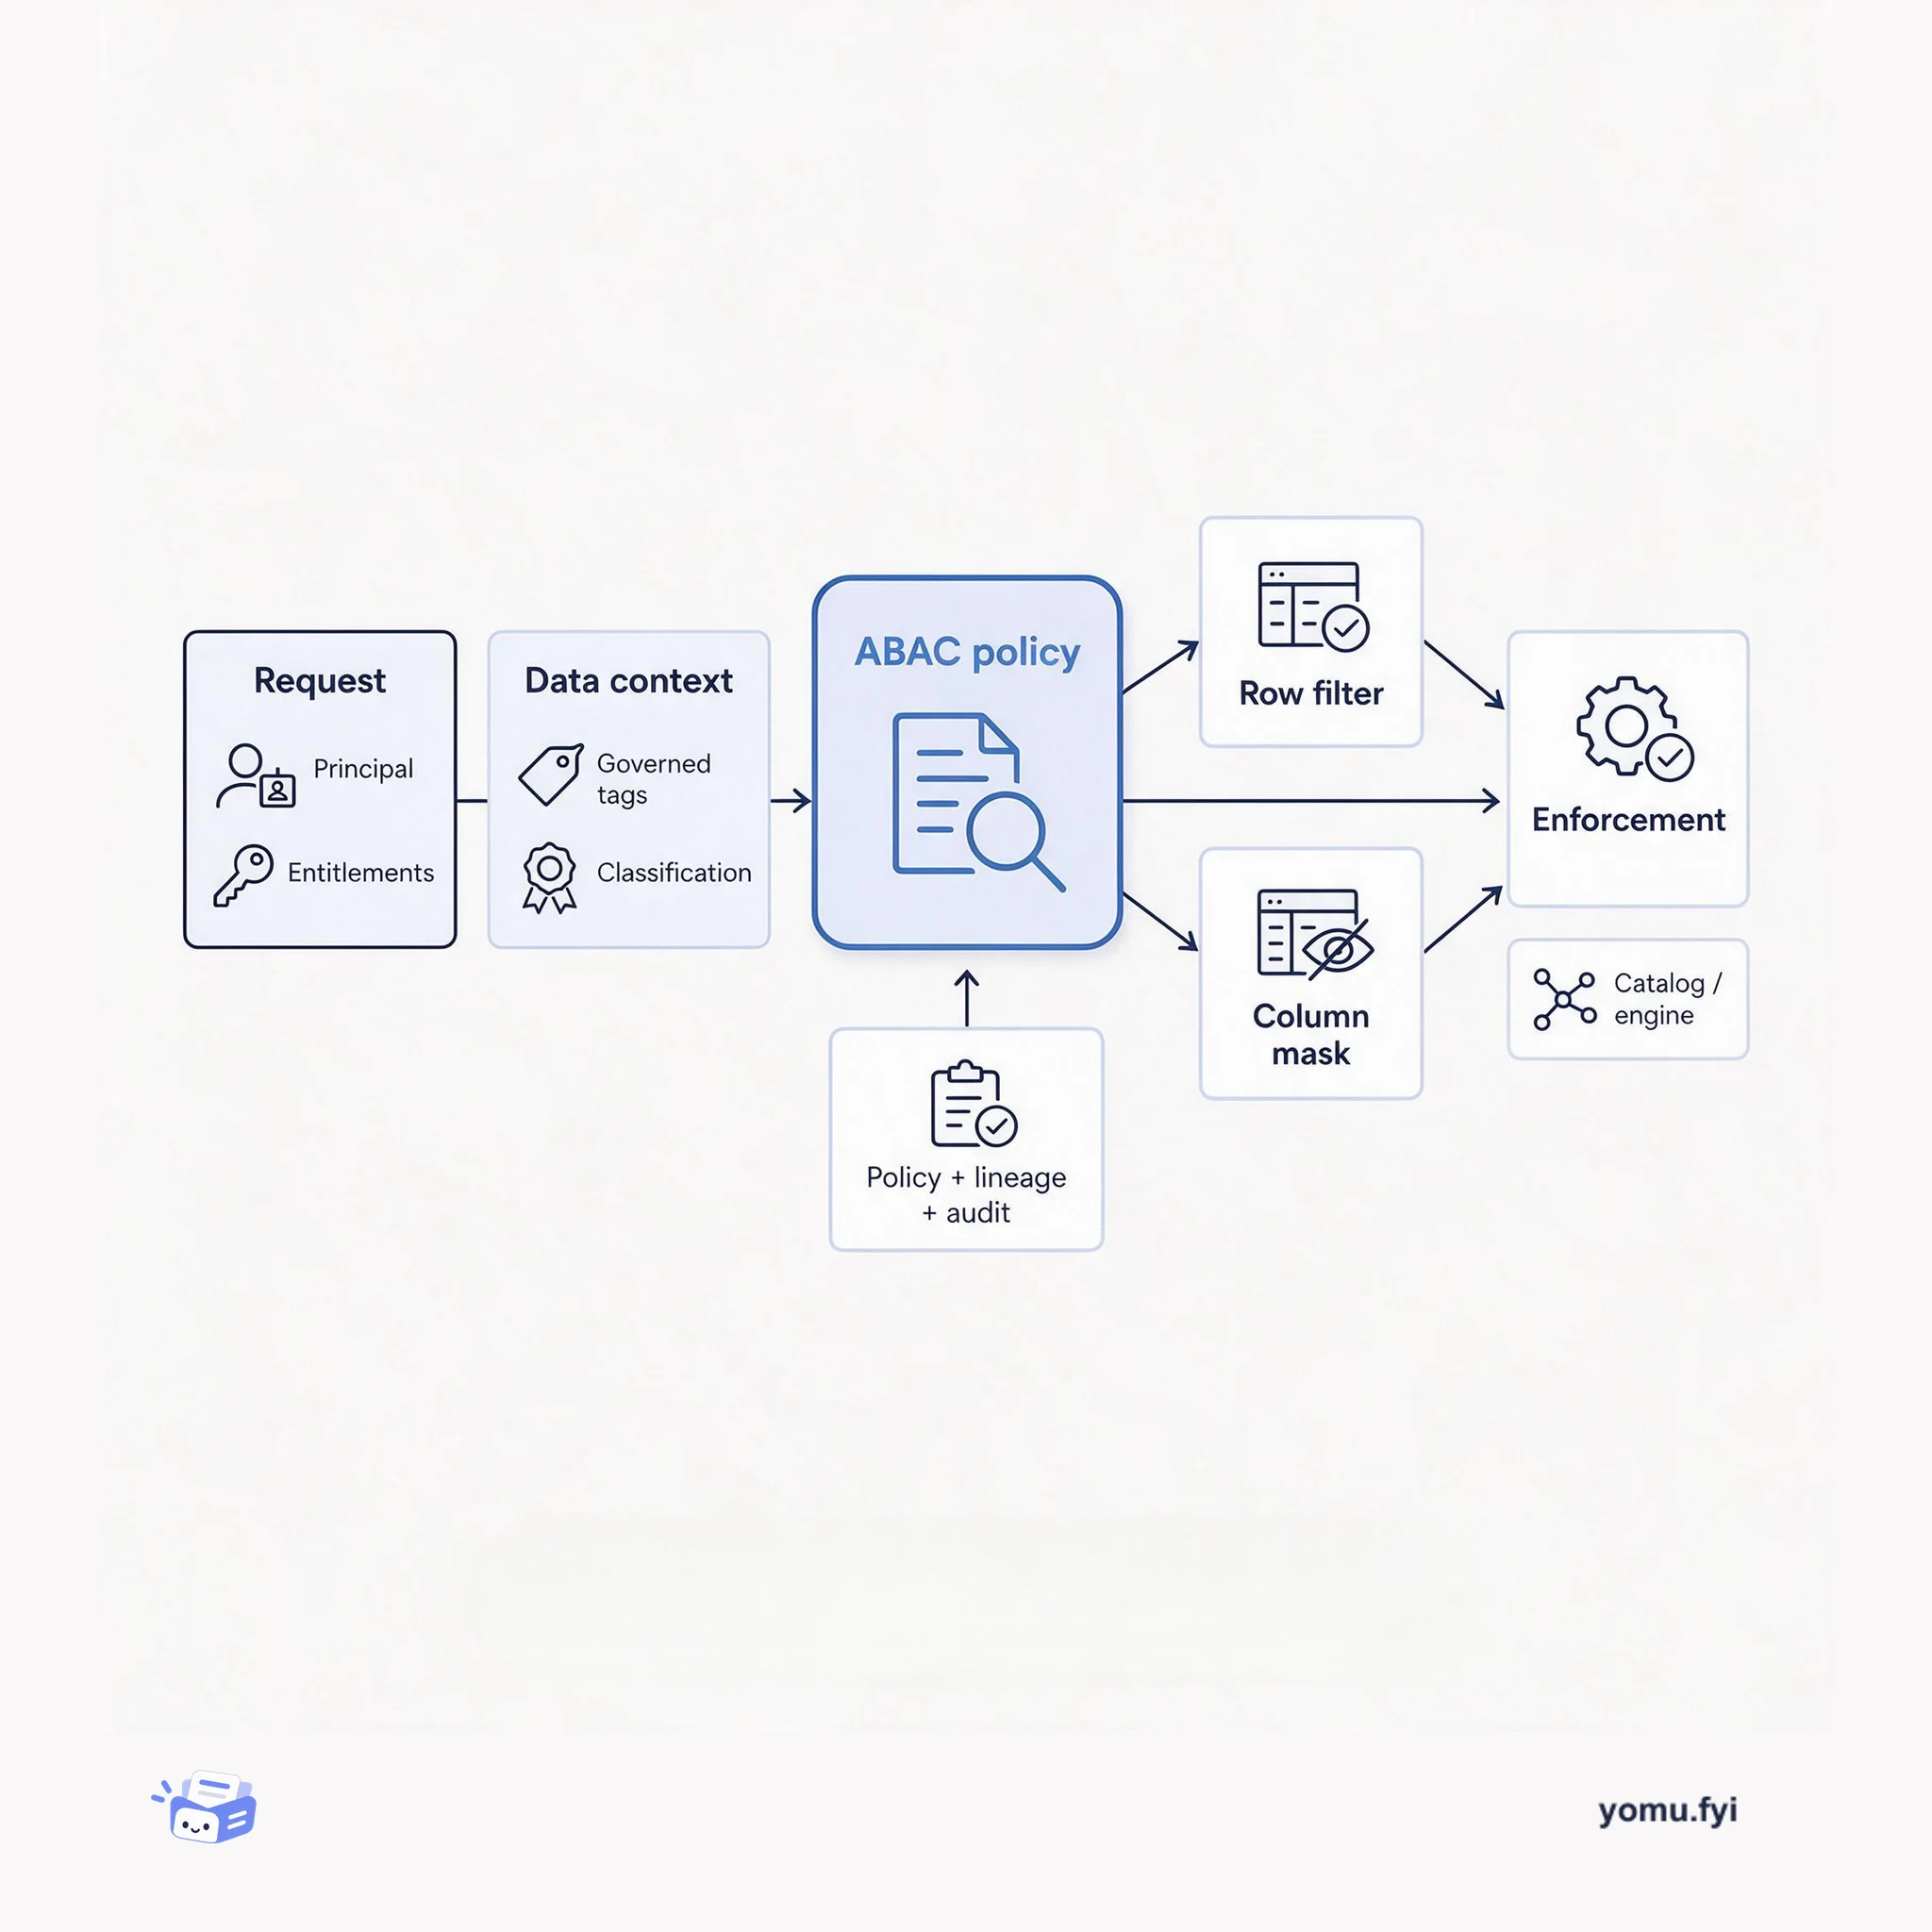
Attribute-Based Access Control uses identity and data attributes to decide access. This explainer shows how governed tags become row filters or column masks across data engines.
 DatabricksAlex Jiang, Alex Reid, Michelle LeonAnnouncement
Cross-engine ABAC is announced in Beta, extending Unity Catalog's fine-grained governance to external engines through Iceberg REST Catalog APIs. It supports tag-based row filters and column masks, including conditional logic and SQL UDFs, while allowing policies to be defined once and enforced across engines. For an external query, the engine sends a scan request, Unity Catalog evaluates entitlements and applicable policies, and returns a filtered scan plan before the engine processes authorized files. Enforcement remains at the catalog layer, so engines need not implement governance logic and can use the open scan APIs. Apache Spark is supported today through Iceberg-Spark and Delta-Spark connectors, with Starburst and DuckDB integrations coming soon; the Beta also points toward Apache Iceberg label exchange for future governance metadata sharing.
Open table formats enabled multiple engines to read the same data, but row-level and column-level policies remained siloed within individual engine runtimes. Security teams therefore had to duplicate policies, maintain separate table copies, or grant broader access than intended.
Unity Catalog uses the Iceberg REST Catalog scan APIs to evaluate user entitlements and applicable ABAC policies, then returns a filtered scan plan to an external engine. The engine queries only the authorized files and does not need to implement policy logic.
Cross-engine ABAC supports tag-based row filters and column masks with conditional logic and SQL UDFs.
The catalog enforces policies before data reaches the external engine, which processes only files included in the filtered scan plan.
Apache Spark works today through the Iceberg-Spark and Delta-Spark connectors; Starburst and DuckDB integrations are planned.
Summaries are generated from the original by a language model. Check the original before relying on it.
See the idea
Attribute-Based Access Control uses identity and data attributes to decide access. This explainer shows how governed tags become row filters or column masks across data engines.
Keep reading
The Good Stuff
Paid picks we use ourselves. Links carry a referral code — a subscription through one earns us a commission at no extra cost to you.
One useful email. Unsubscribe anytime.
