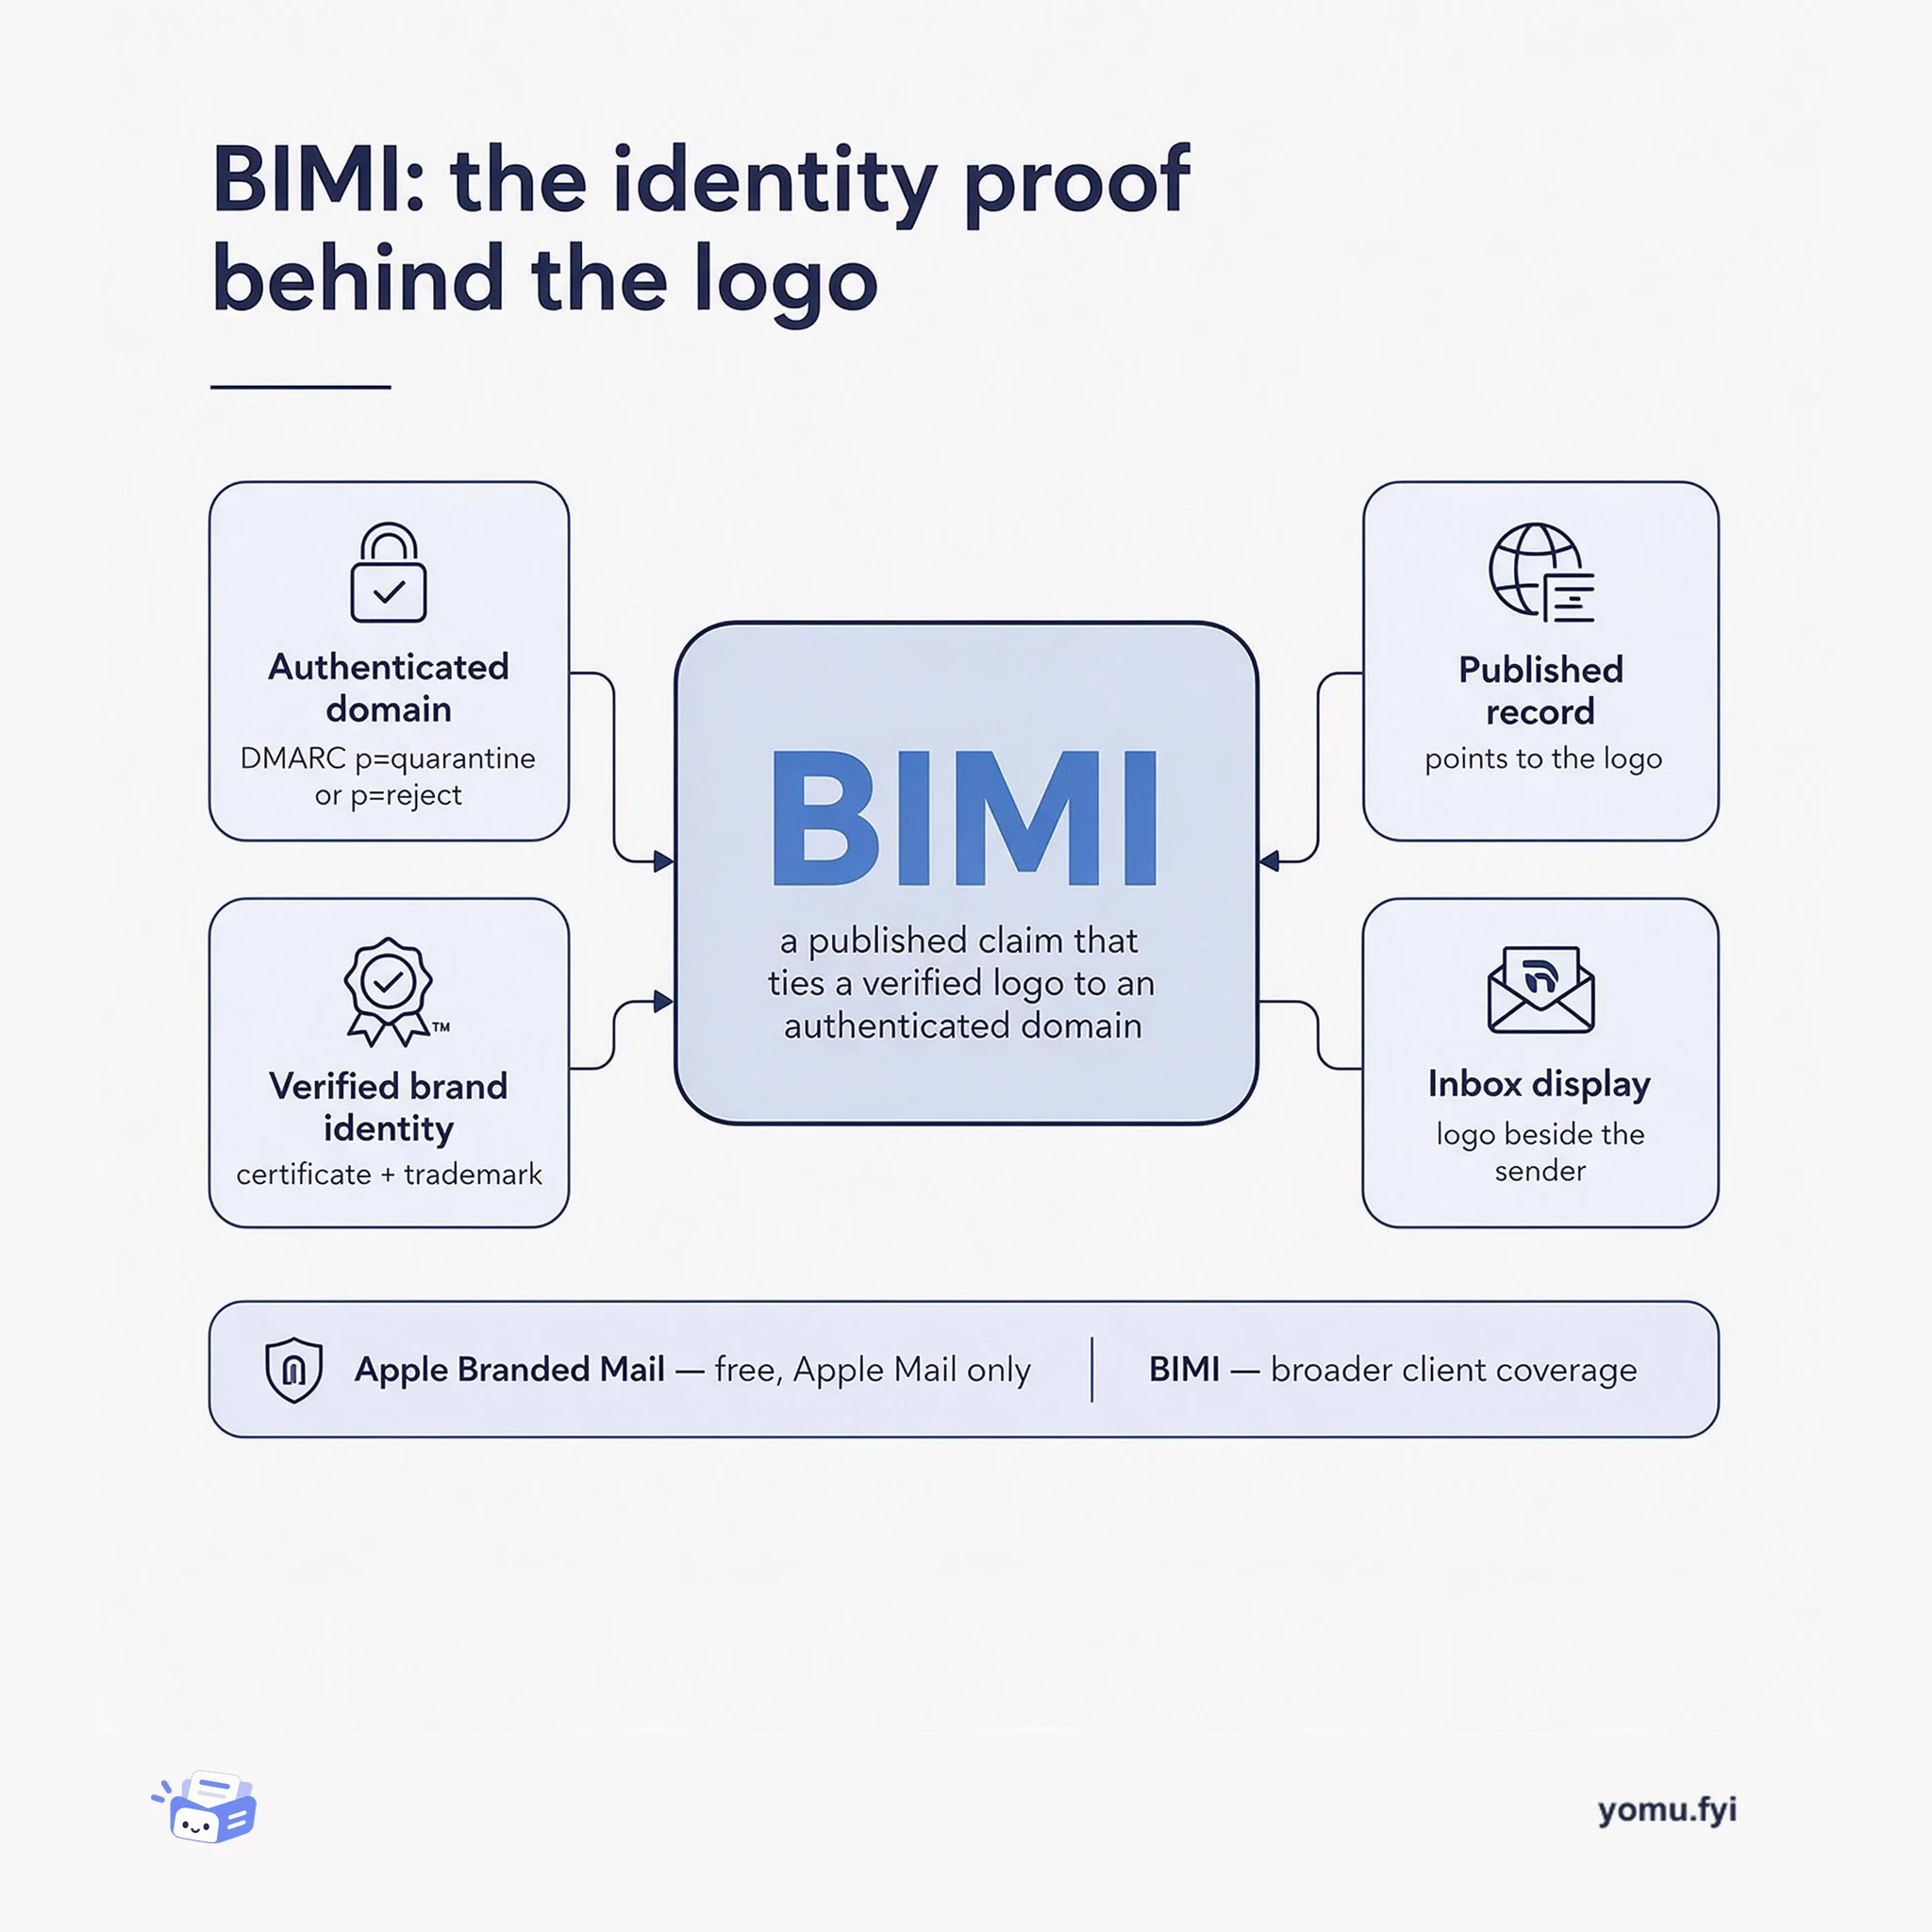
BIMI: The Identity Proof Behind the Logo
BIMI is a DNS-published claim that ties a verified brand logo to an authenticated domain, so mailbox providers can display it. Here is what each part of that claim requires.
 OktaVanshika PandeyAnnouncement
Okta will end support for Self-Service Registration, Desktop Single Sign-On using Integrated Windows Authentication (IWA), and Device Trust on Classic Engine on March 5, 2027. After that deadline, the capabilities will be turned off unless organizations upgrade to Okta Identity Engine, and Okta will no longer address related bugs, security vulnerabilities, or broken flows. The migration paths are Profile Enrollment Policy for self-service registration, Agentless Desktop Single Sign-On or Okta FastPass for desktop authentication, and management attestation with Okta Verify for mobile device trust. Identity Engine adds passwordless authentication, device assurance, phishing-resistant multifactor authentication, identity verification, zero-trust capabilities, and a newer policy framework, with the upgrade included at no additional licensing cost. Organizations are advised to assess feature usage, test in non-production, and schedule production migration before the hard deadline.
Classic Engine support for Self-Service Registration, Desktop SSO through IWA, and Device Trust ends on March 5, 2027. Okta issued the initial notice on August 5, 2026, followed by reminders through March 1, 2027. The deadline is described as hard, and affected capabilities will be unavailable without an earlier upgrade to Identity Engine.
Migrate affected authentication flows to their Identity Engine replacements: use Profile Enrollment Policy for Self-Service Registration, Agentless Desktop Single Sign-On or Okta FastPass for IWA-based desktop authentication, and management attestation with Okta Verify for Device Trust. Okta recommends assessing current feature usage, testing in a non-production environment, and scheduling the production upgrade during an appropriate maintenance window.
Classic Engine support for Self-Service Registration, Desktop SSO using IWA, and Device Trust ends March 5, 2027; the capabilities are turned off after that date unless the organization upgrades.
Identity Engine replacements include Profile Enrollment Policy, Agentless Desktop SSO or Okta FastPass, and management attestation with Okta Verify.
The Identity Engine upgrade is free under the existing Okta subscription, but organizations should test migration flows in non-production before upgrading production.
Organizations can migrate to Agentless Desktop Single Sign-On (ADSSO) for agentless desktop authentication or to Okta FastPass for passwordless platform authentication. Okta recommends consulting the account team to determine which option fits the authentication and device management strategy.
Identity Engine uses management attestation with Okta Verify. It verifies that Okta Verify manages and trusts the mobile device before allowing access, providing enhanced device assurance beyond the previous Device Trust feature.
No. The upgrade itself is free, and the Identity Engine capabilities described are included at no additional licensing cost as part of the existing Okta subscription.
Summaries are generated from the original by a language model. Check the original before relying on it.
See the idea
BIMI is a DNS-published claim that ties a verified brand logo to an authenticated domain, so mailbox providers can display it. Here is what each part of that claim requires.
Keep reading
The Good Stuff
Paid picks we use ourselves. Links carry a referral code — a subscription through one earns us a commission at no extra cost to you.
One useful email. Unsubscribe anytime.
