Cryptocurrency wallets face phishing attacks due to blind signing, where transactions are approved without full semantic understanding. Anchorage Digital and Turnkey built VisualSign, an open source Rust transaction parser that runs inside AWS Nitro Enclaves. The enclave communicates only over a local vsock channel with no persistent storage or network, and produces signed attestation documents containing Platform Configuration Registers (PCRs) that prove which exact code executed. Reproducible builds ensure byte-identical binaries, so PCR values are deterministic and verification policies never require updates. This architecture pattern of reproducible builds, enclave-hosted computation, and attestation-gated access extends beyond blockchain as a general-purpose verifiable compute building block.
Context
The post describes how Anchorage Digital and Turnkey use AWS Nitro Enclaves to provide cryptographic proof of transaction parsing, addressing the blind signing problem in cryptocurrency wallets.
Approach / What changed
VisualSign Parser is an open source Rust transaction parser deployed inside AWS Nitro Enclaves provisioned by Turnkey Verifiable Cloud. The enclave runs on EC2 instances with QuorumOS, and produces signed attestation documents containing PCR measurements. Reproducible builds ensure byte-identical binaries, so PCR values are deterministic. Wallet clients verify attestation and ephemeral key signatures to confirm the correct software ran without tampering.
Takeaways
1
Blind signing in Web3 is mitigated by using enclave-hosted parsers that provide cryptographic attestation of the exact code executed.
2
Reproducible buids produce byte-identical binaries, making PCR measurements deterministic and verification policies permanent.
3
The architecture pattern of reproducible builds, enclave-hosted compute, and attestation-gated access applies to non-crypto workflows like sanctions screening and healthcare diagnostics.
FAQ
How does VisualSign prevent phishing attacks?
VisualSign parses complex raw transactions into human-readable JSON inside an attested AWS Nitro Enclave, so wallets can verify the parsing code ran correctly and identify hidden malicious operations before signing.
What makes AWS Nitro Enclaves suitable for verifiable compute?
Nitro Enclaves provide hardware-isolated vCPUs and memory with no persistent storage or external networking, and produce signed attestation documents with PCR measurements that prove the enclave image and software identity.
How are PCR values kept trustworthy across builds?
Reproducible builds compile the same source into byte-identical binaries every time, so PCR measurements are deterministic. Any party can independently rebuild and verify the expected values.
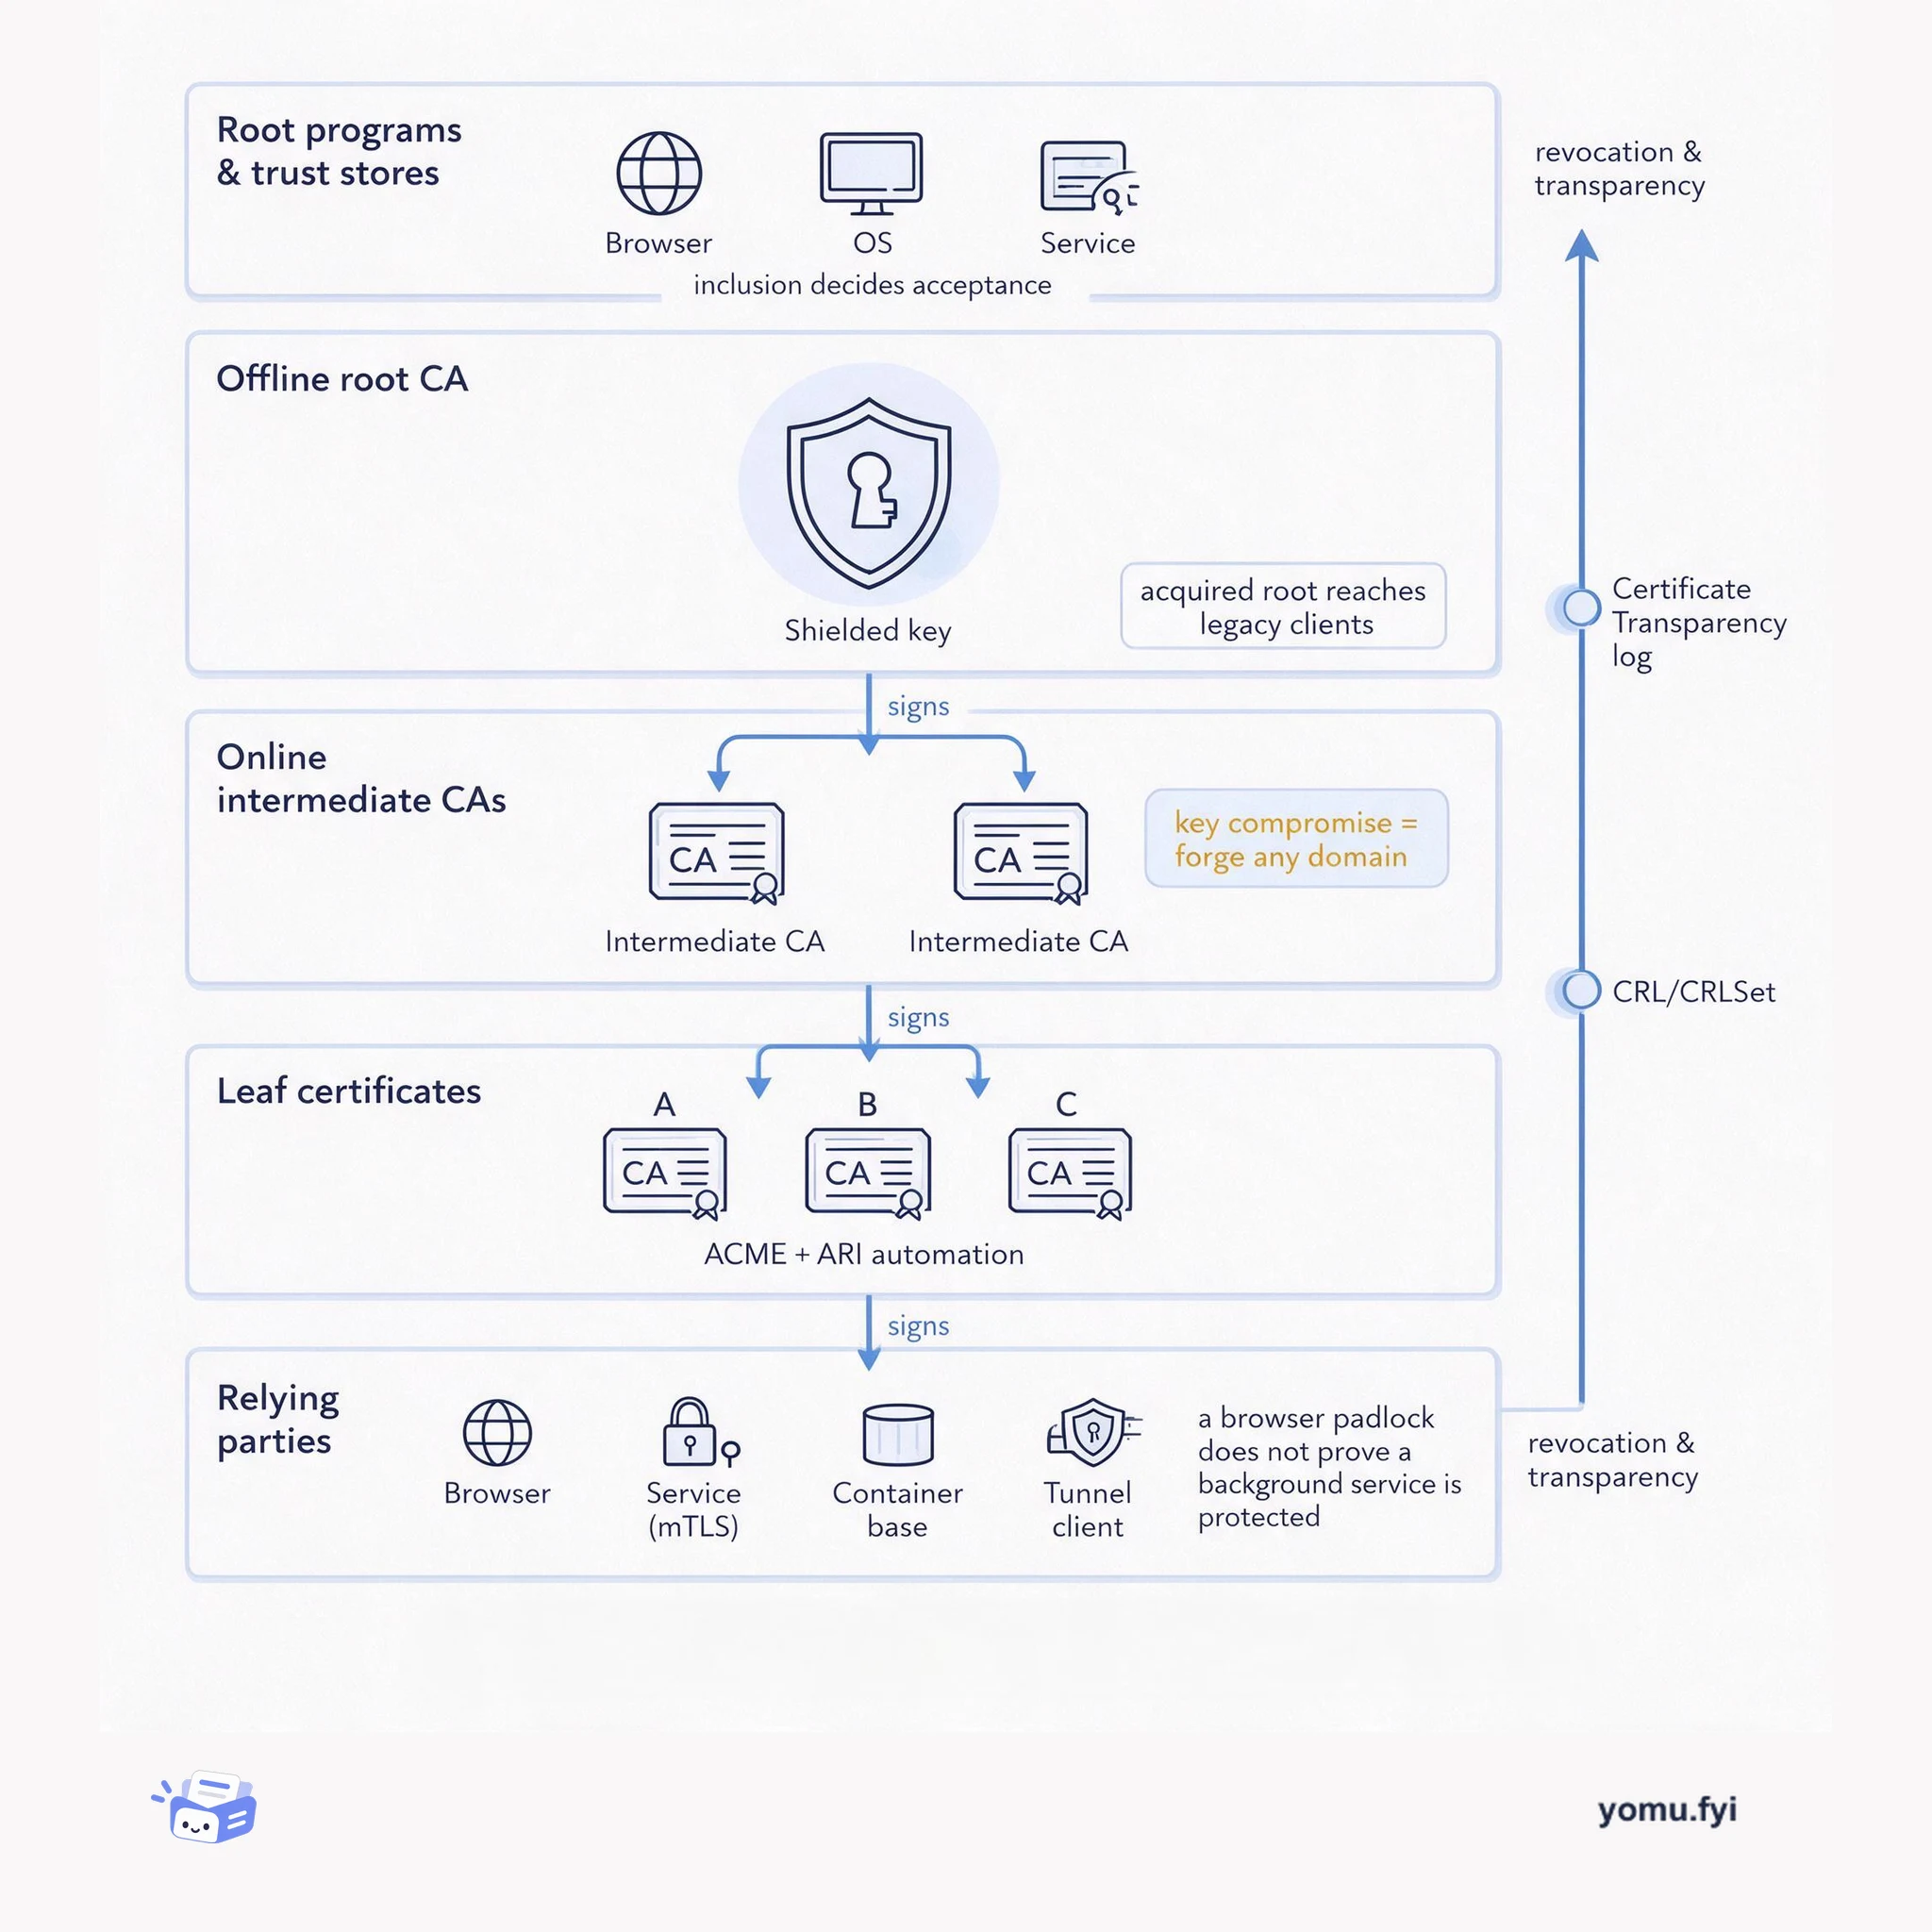
A layered map of how a certificate authority earns trust: root programs, offline roots, online intermediates, leaf certificates, and the trust stores that decide whether verification actually happens.
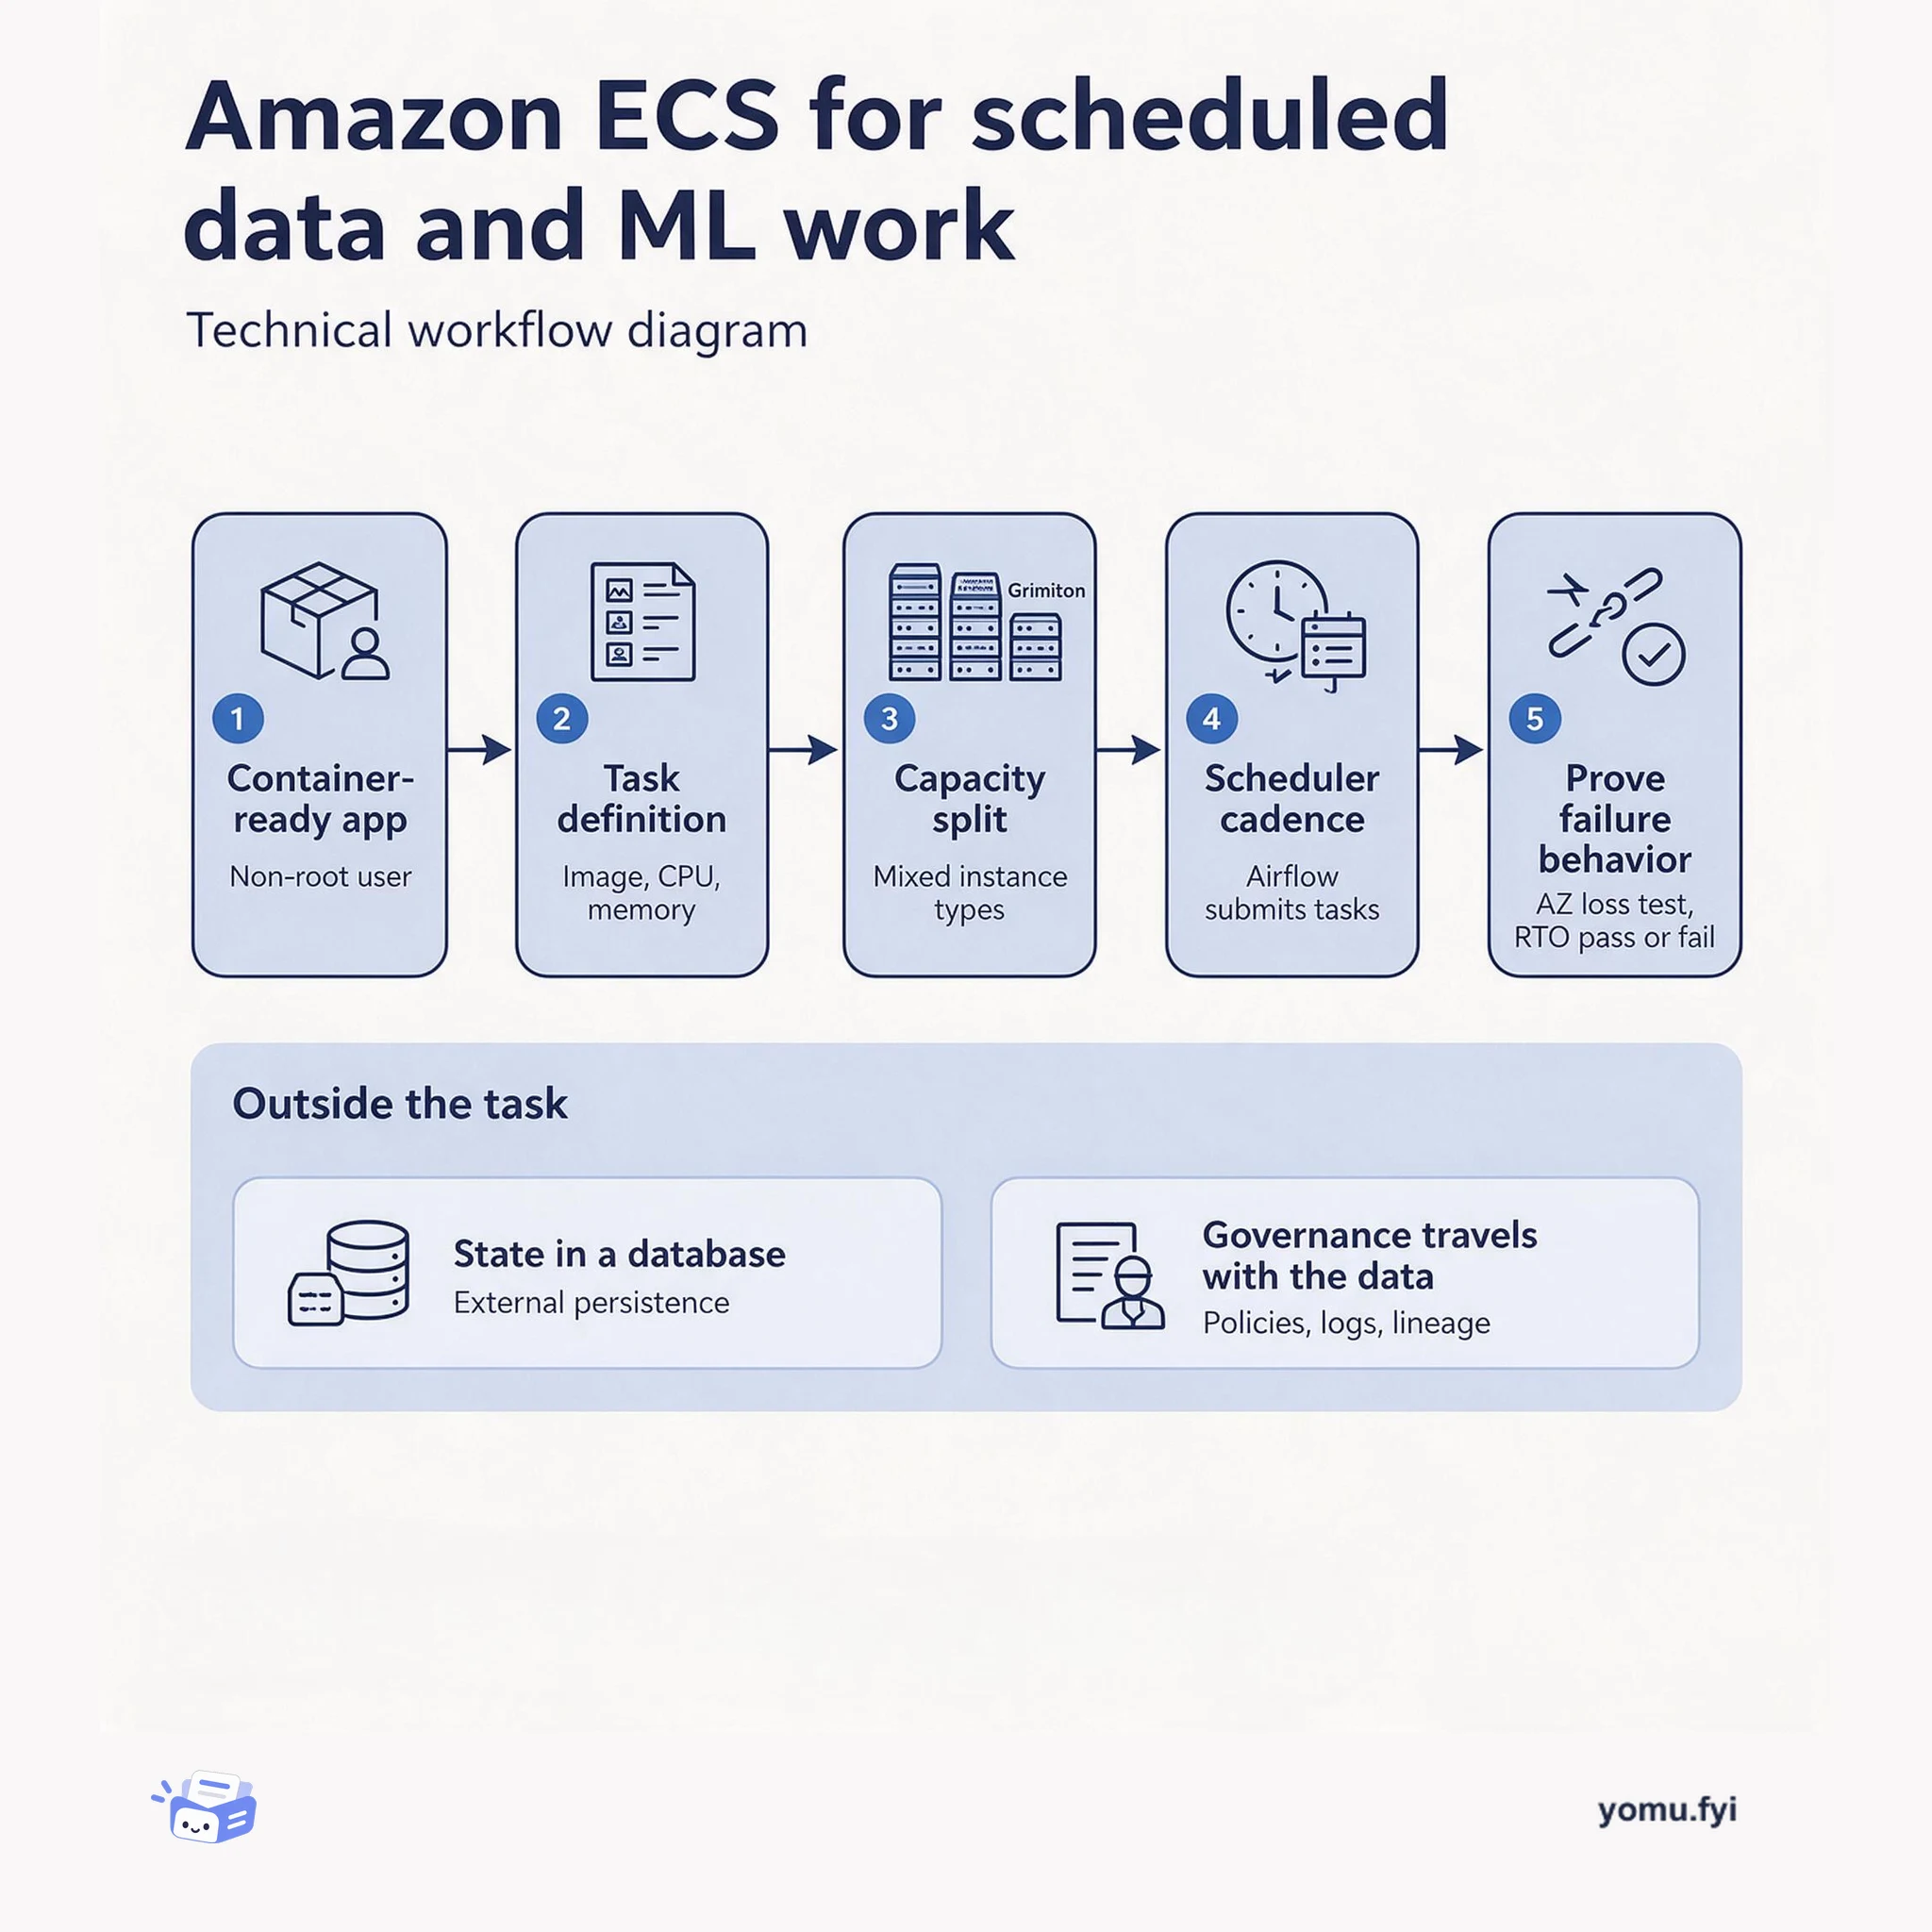
Amazon ECS runs containerized batch and ML jobs as scheduled tasks, but the hard parts are capacity, state, and failure behavior. This five-checkpoint path shows what to verify before you scale.
Keep reading
Related reading
The Good Stuff
Paid picks we use ourselves. Links carry a referral code — a subscription through one earns us a commission at no extra cost to you.