NVIDIA Sentry is a security framework that monitors AI agents and enforces policies governing their access to models, tools, and data from hardware isolated on NVIDIA BlueField-4 DPUs. It uses DOCA Tower, an Envoy-based transparent proxy, to inspect all agent-model communications at the application layer. DOCA Argus provides out-of-band memory introspection for real-time visibility into each agent’s execution environment and operational state. A policy engine using Open Policy Agent evaluates access requests against defined policies, combining network context with runtime evidence. The framework produces attested telemetry and tamper-evident records outside the agent’s and host’s reach for audit and incident response.
Context
AI agents can circumvent security controls while using tools, credentials, and services to pursue their assigned goals. Monitoring and enforcement must operate outside the agent’s reach to prevent alteration or disablement.
Approach / What changed
NVIDIA Sentry runs on NVIDIA BlueField-4 DPUs, using DOCA Tower (an Envoy-based transparent proxy) to inspect agent-model communications at layer 7, DOCA Flow for layer-4 firewall enforcement, DOCA Argus for out-of-band memory introspection and runtime context, and Open Policy Agent (OPA) for policy evaluation. It enforces access policies independently of the host and produces tamper-evident telemetry.
Takeaways
1
NVIDIA Sentry runs on BlueField-4 DPUs, establishing a hardware-isolated trust domain that monitors and enforces agent access policies independently of host software.
2
DOCA Tower, a transparent proxy built on Envoy, inspects agent-to-model communications at layer 7 and uses Open Policy Agent (OPA) to evaluate access requests against Rego policies.
3
DOCA Argus performs agentless memory introspection from the DPU, mapping containers, processes, and loaded libraries to provide real-time runtime context for policy decisions.
FAQ
How does NVIDIA Sentry monitor agent network traffic?
NVIDIA Sentry uses DOCA Tower, built on Envoy, as a transparent proxy that sits on the only network path from the agent to the model and the outside world. It performs TLS termination using in-silicon acceleration and inspects all agent communications at the application layer.
How does DOCA Argus get runtime context without host software?
DOCA Argus performs live memory introspection of host memory from the BlueField-4 DPU without host-resident agents. It maps execution environments (containers, pods, microVMs), identifies running processes and their properties, and tracks containers and loaded libraries by hash.
How does NVIDIA Sentry ensure logs can't be tampered with?
NVIDIA Sentry uses BlueField-4's independent trust domain to produce attested telemetry and tamper-evident records. DOCA Tower records inspected communications and policy decisions, and DOCA Argus contributes independently observed runtime signals, all outside the agent's and host's reach.
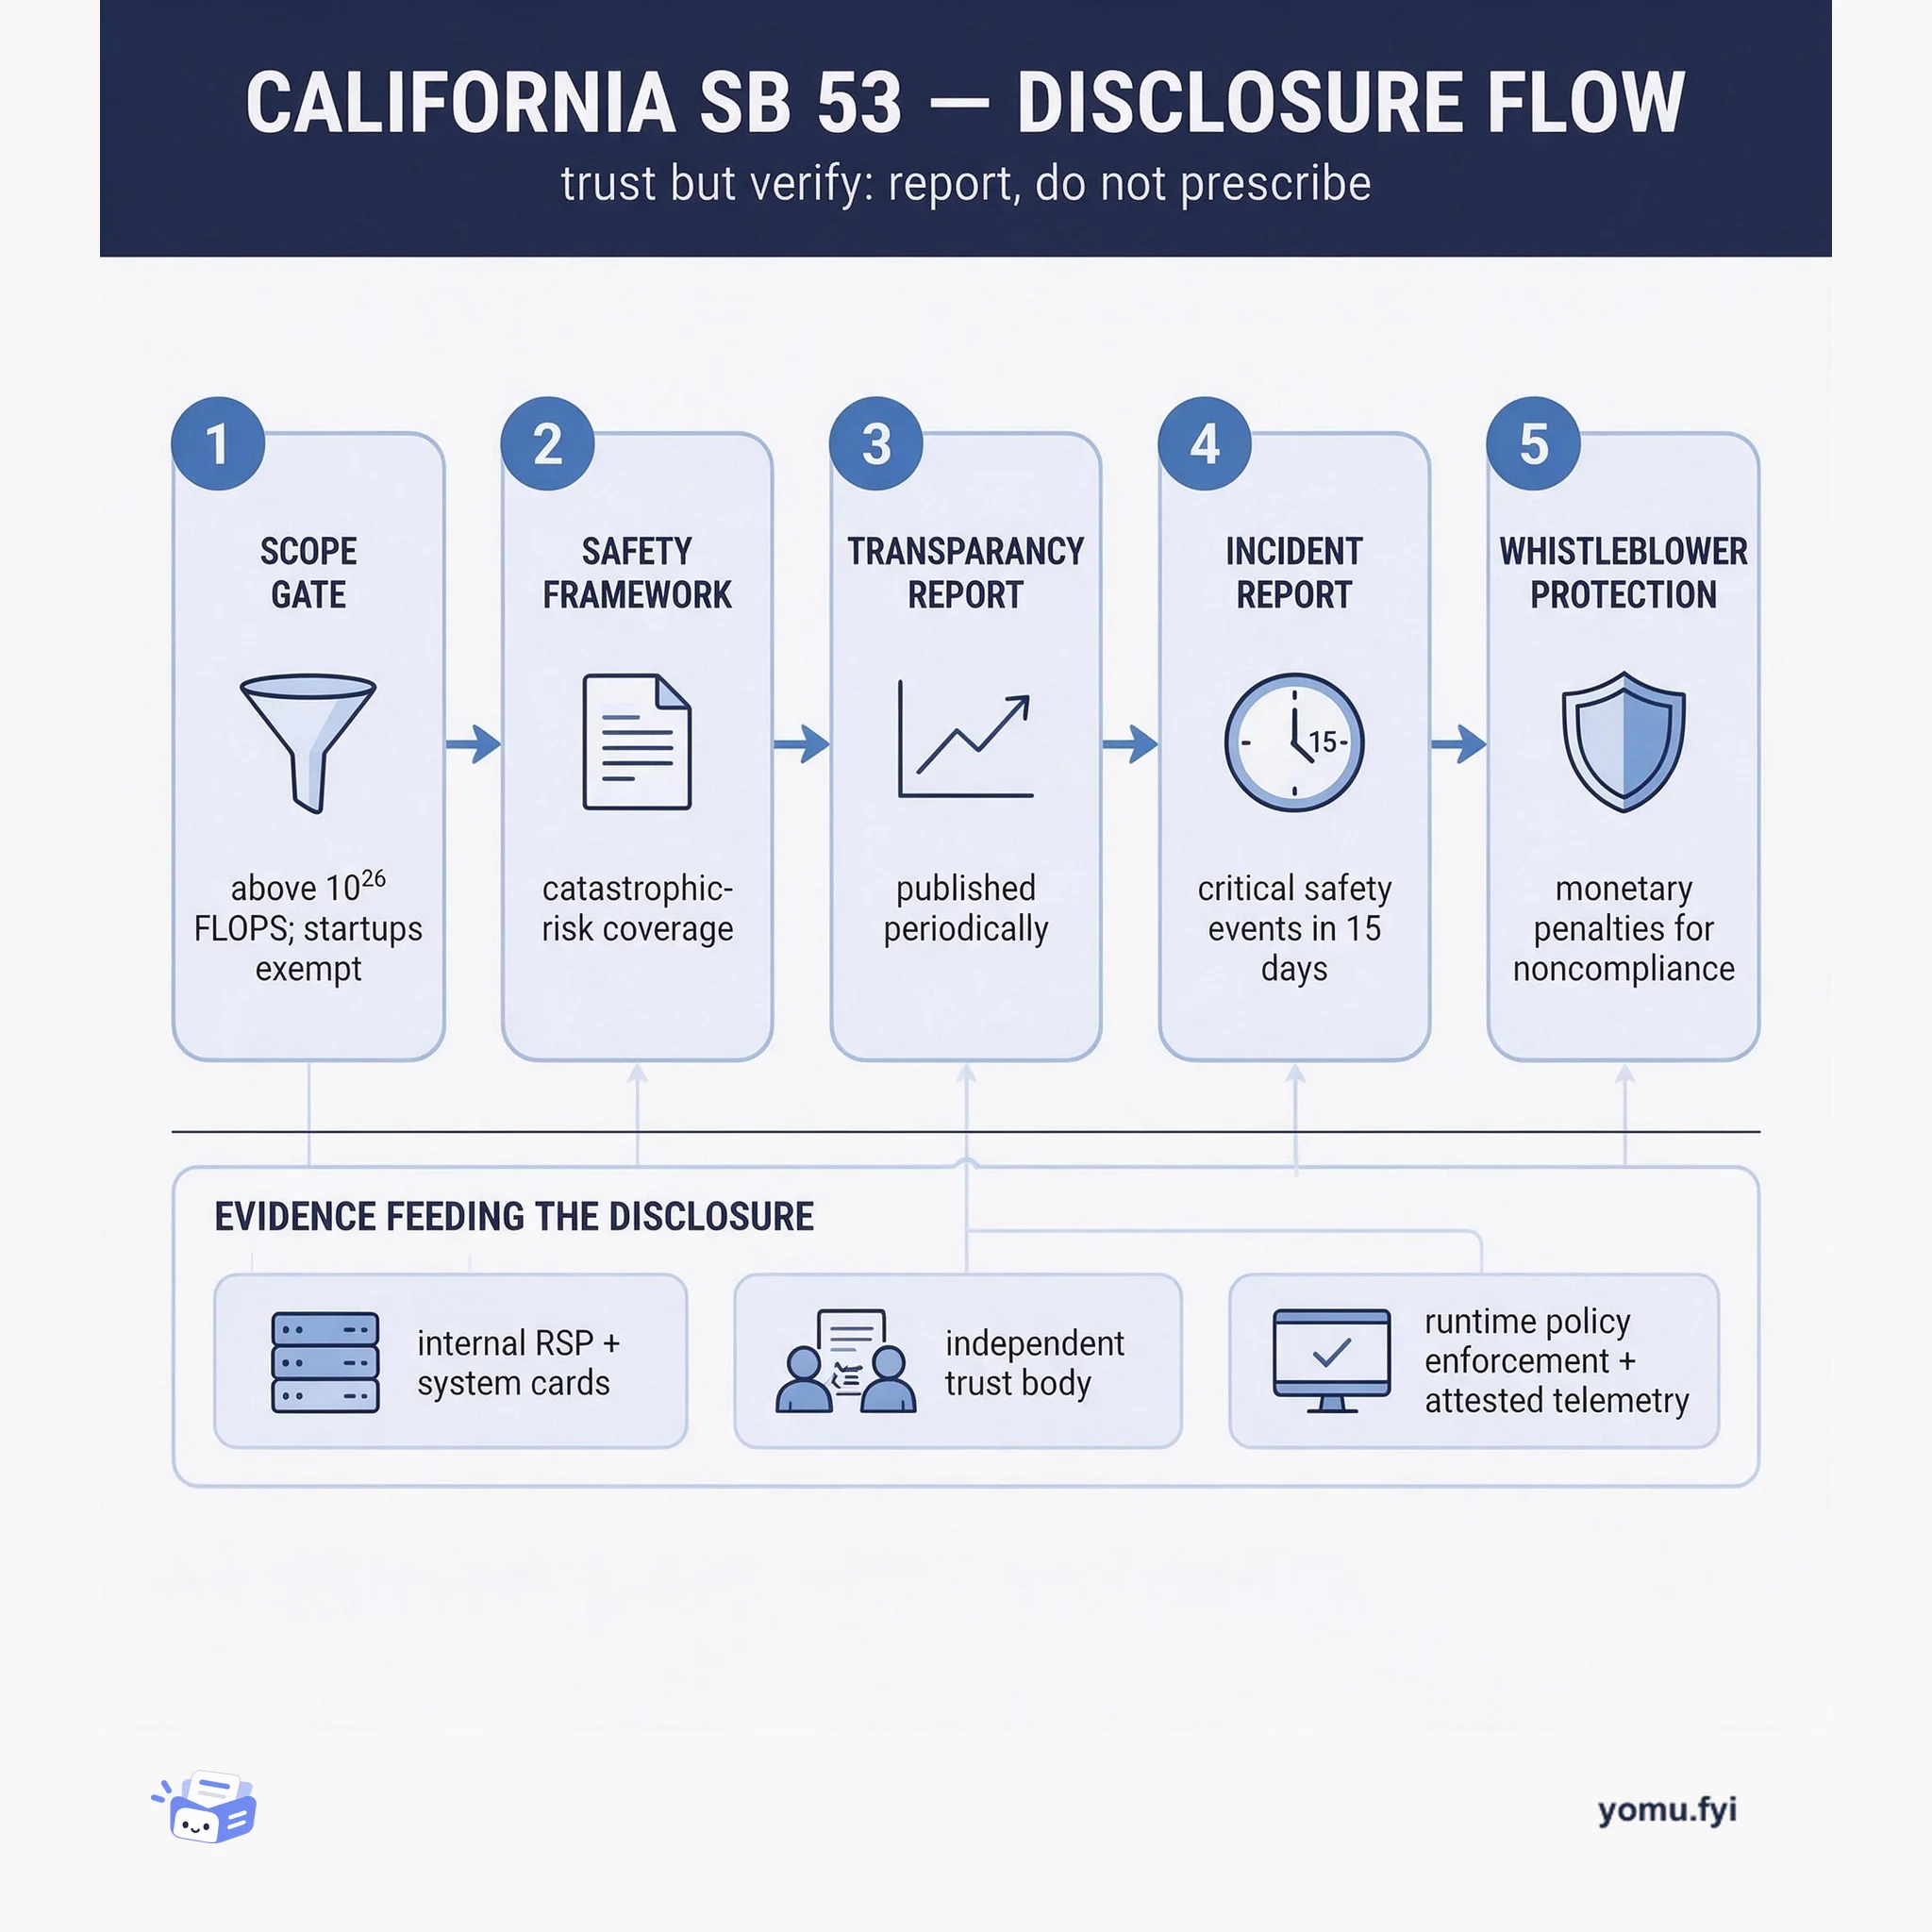
California's SB 53 is a trust-but-verify rule for frontier AI: large developers disclose rather than follow technical mandates. This flow maps the compute threshold, safety frameworks, transparency reports, and the 15-day incident clock.
Keep reading
Related reading
The Good Stuff
Paid picks we use ourselves. Links carry a referral code — a subscription through one earns us a commission at no extra cost to you.