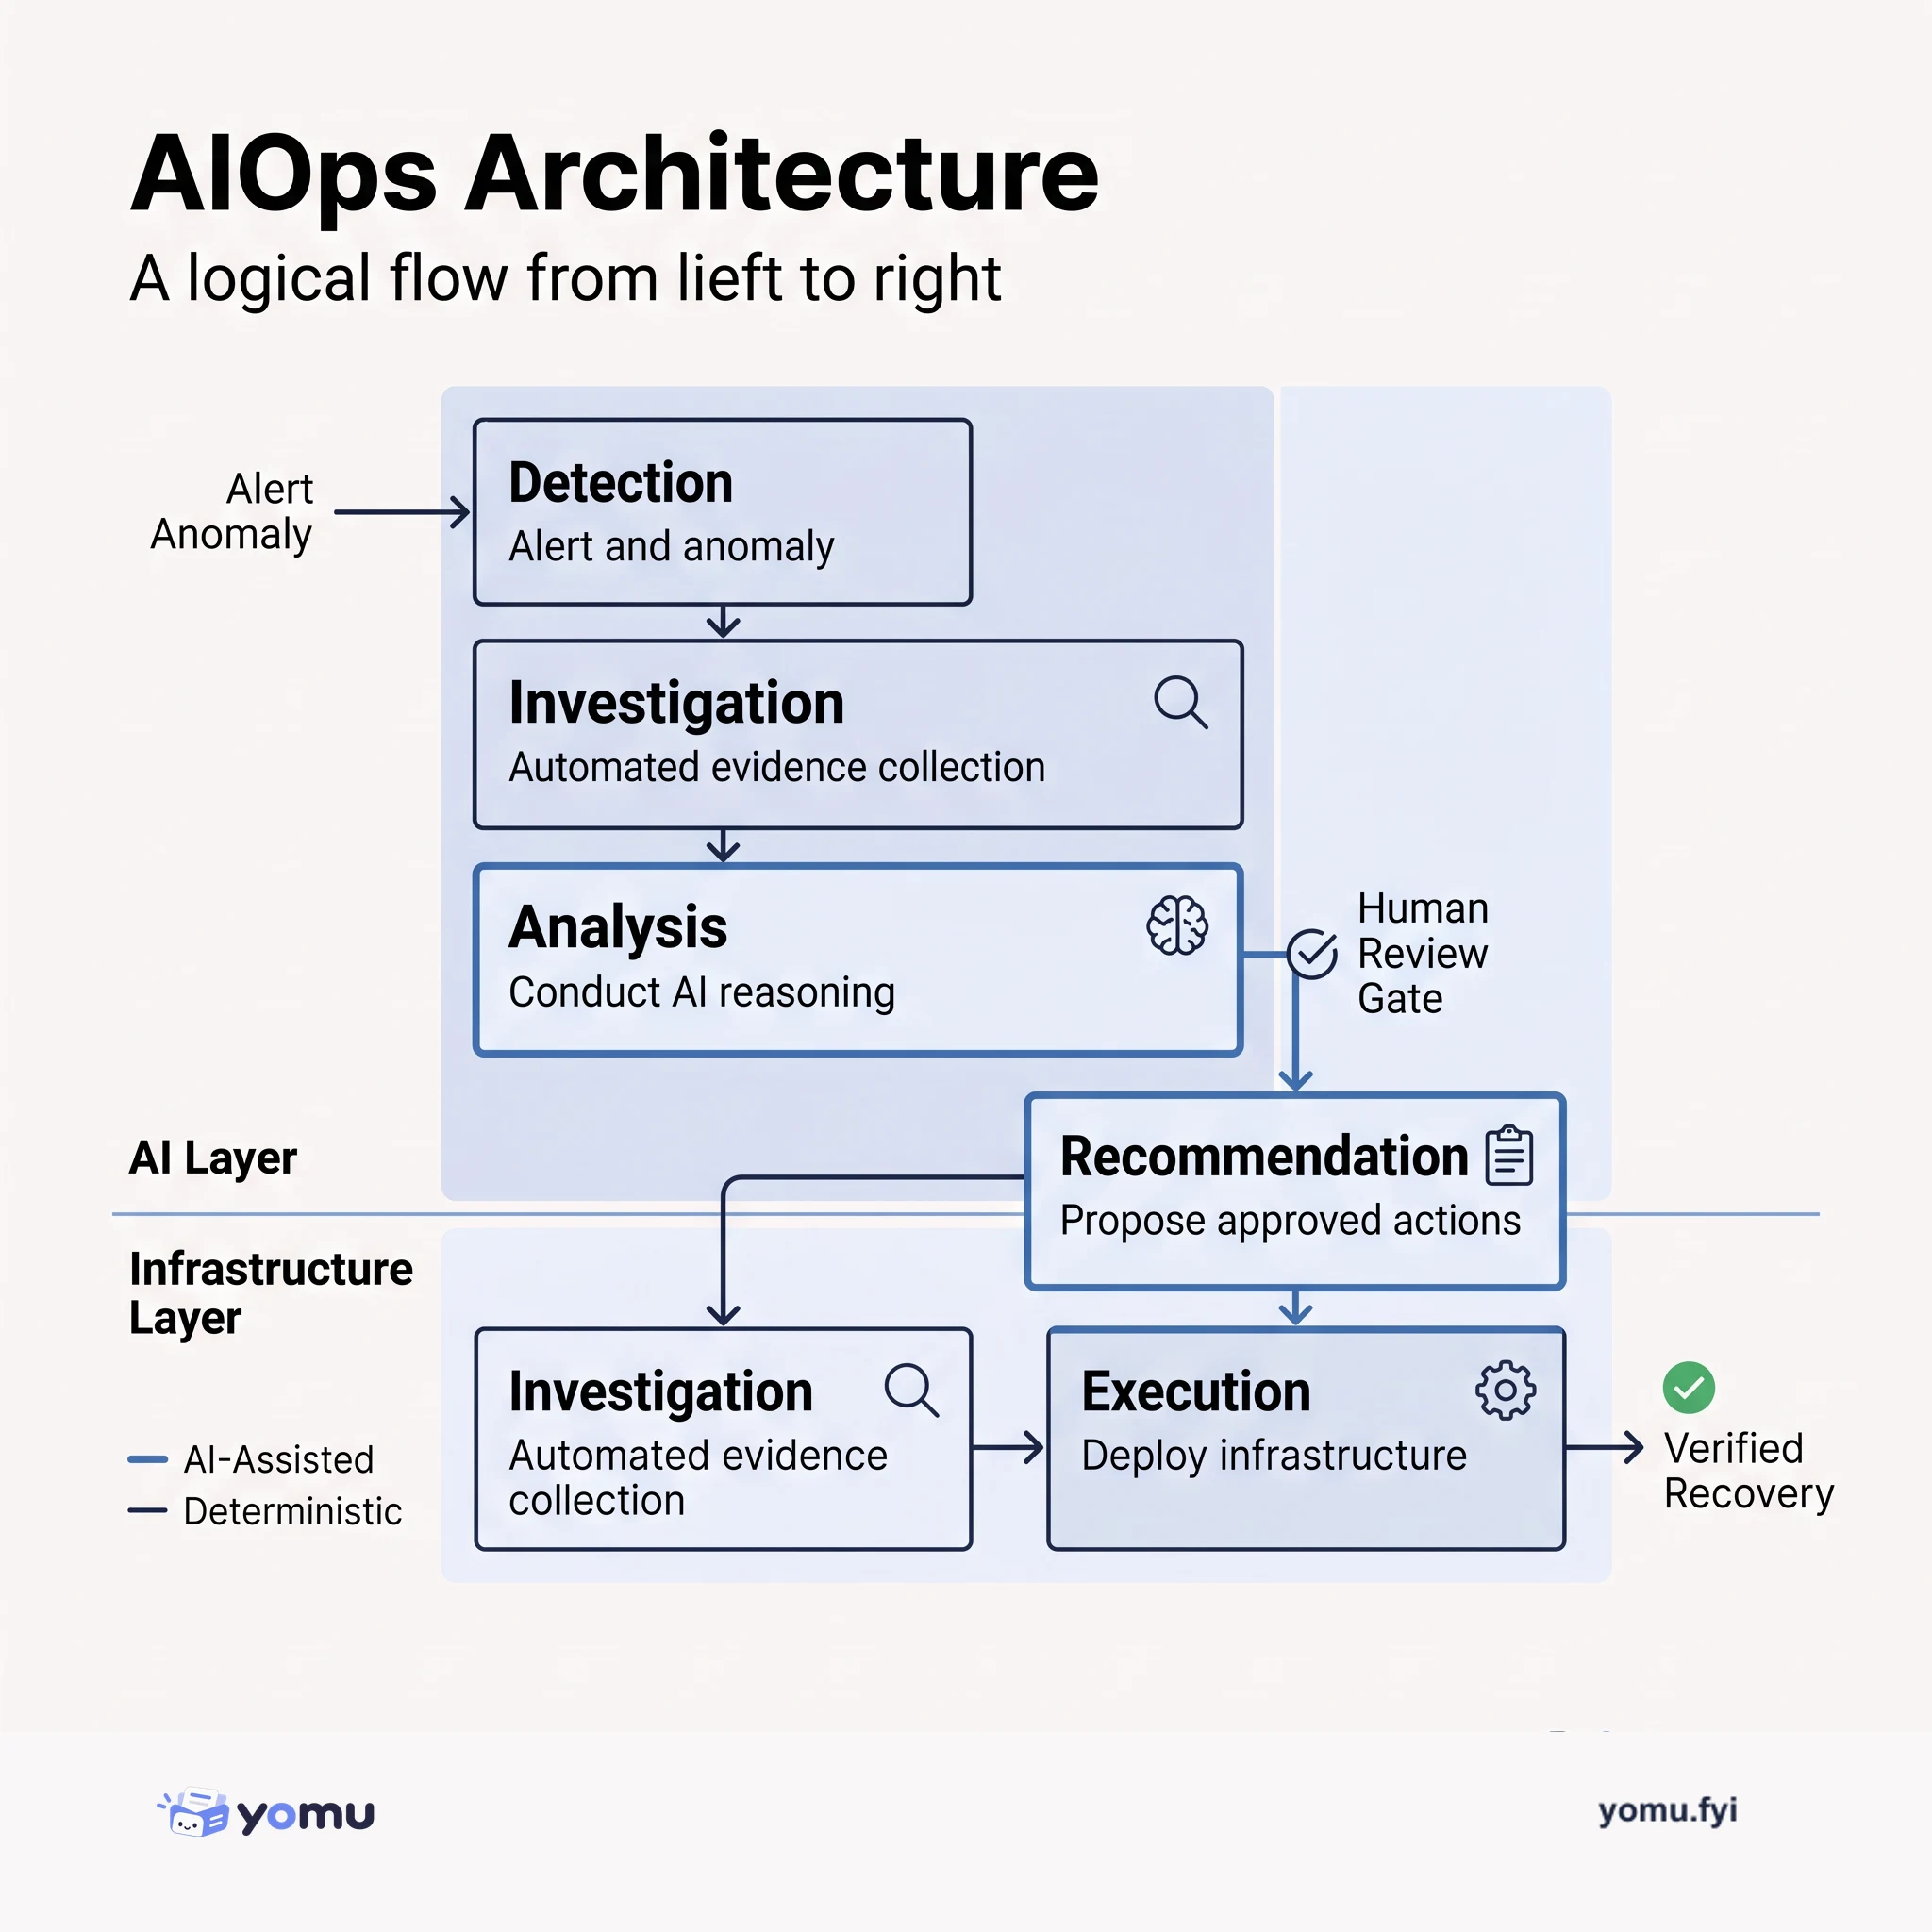
AIOps Architecture: From Detection to Remediation
AIOps automates the detect-investigate-analyze-recommend-execute-verify cycle by combining AI reasoning with infrastructure automation, keeping humans in control of credentials and final decisions.
 CloudflareKen SandersonAnnouncement
Cloudflare announces invitation-only early access to Vulnerability Discovery and Remediation, a Managed Defense service that investigates authorized codebases and helps prioritize and mitigate vulnerabilities. It combines source-code analysis with production route activity, traffic volume, security events, and active Web Application Firewall (WAF) protections to assess exposure. Reconnaissance maps request paths to code, hunter agents search relevant sections, and validation checks proposed patches and custom WAF rules before customer review. OpenAI Daybreak models, including GPT-5.6 Cyber, run reconnaissance, hunting, and validation through AI Gateway, while source code, logs, and request metadata are bounded by authorization, redaction, access policies, and external checks. Findings receive source-based risk ratings that network evidence can raise, with code patches and conservative WAF mitigations prepared for review; customers decide whether to test or deploy them.
Security teams increasingly face large volumes of vulnerability findings and limited time to determine which weaknesses matter most. Source-code analysis alone does not show whether affected code is deployed, which routes reach it, how much traffic it receives, whether it is being probed, or what protections already apply.
Vulnerability Discovery and Remediation combines Web Assets and WAF snapshots, Workers route and observability metadata, bounded source-code investigation, OpenAI Daybreak models, and customer-authorized access. Reconnaissance maps request paths to code, hunter agents investigate relevant sections, and validation checks patches and proposed WAF rules using controls outside the model before customer review.
Production traffic, route activity, security events, and existing WAF protections can raise a finding’s initial source-based risk rating.
GPT-5.6 Cyber performs reconnaissance, hunting, and validation on OpenAI’s servers through Cloudflare AI Gateway; no model inference runs at Cloudflare’s edge.
Proposed patches and WAF rules are checked before review, but customers retain control over whether any change is tested or deployed.
Summaries are generated from the original by a language model. Check the original before relying on it.
See the idea
AIOps automates the detect-investigate-analyze-recommend-execute-verify cycle by combining AI reasoning with infrastructure automation, keeping humans in control of credentials and final decisions.
Keep reading
The Good Stuff
Paid picks we use ourselves. Links carry a referral code — a subscription through one earns us a commission at no extra cost to you.
One useful email. Unsubscribe anytime.
