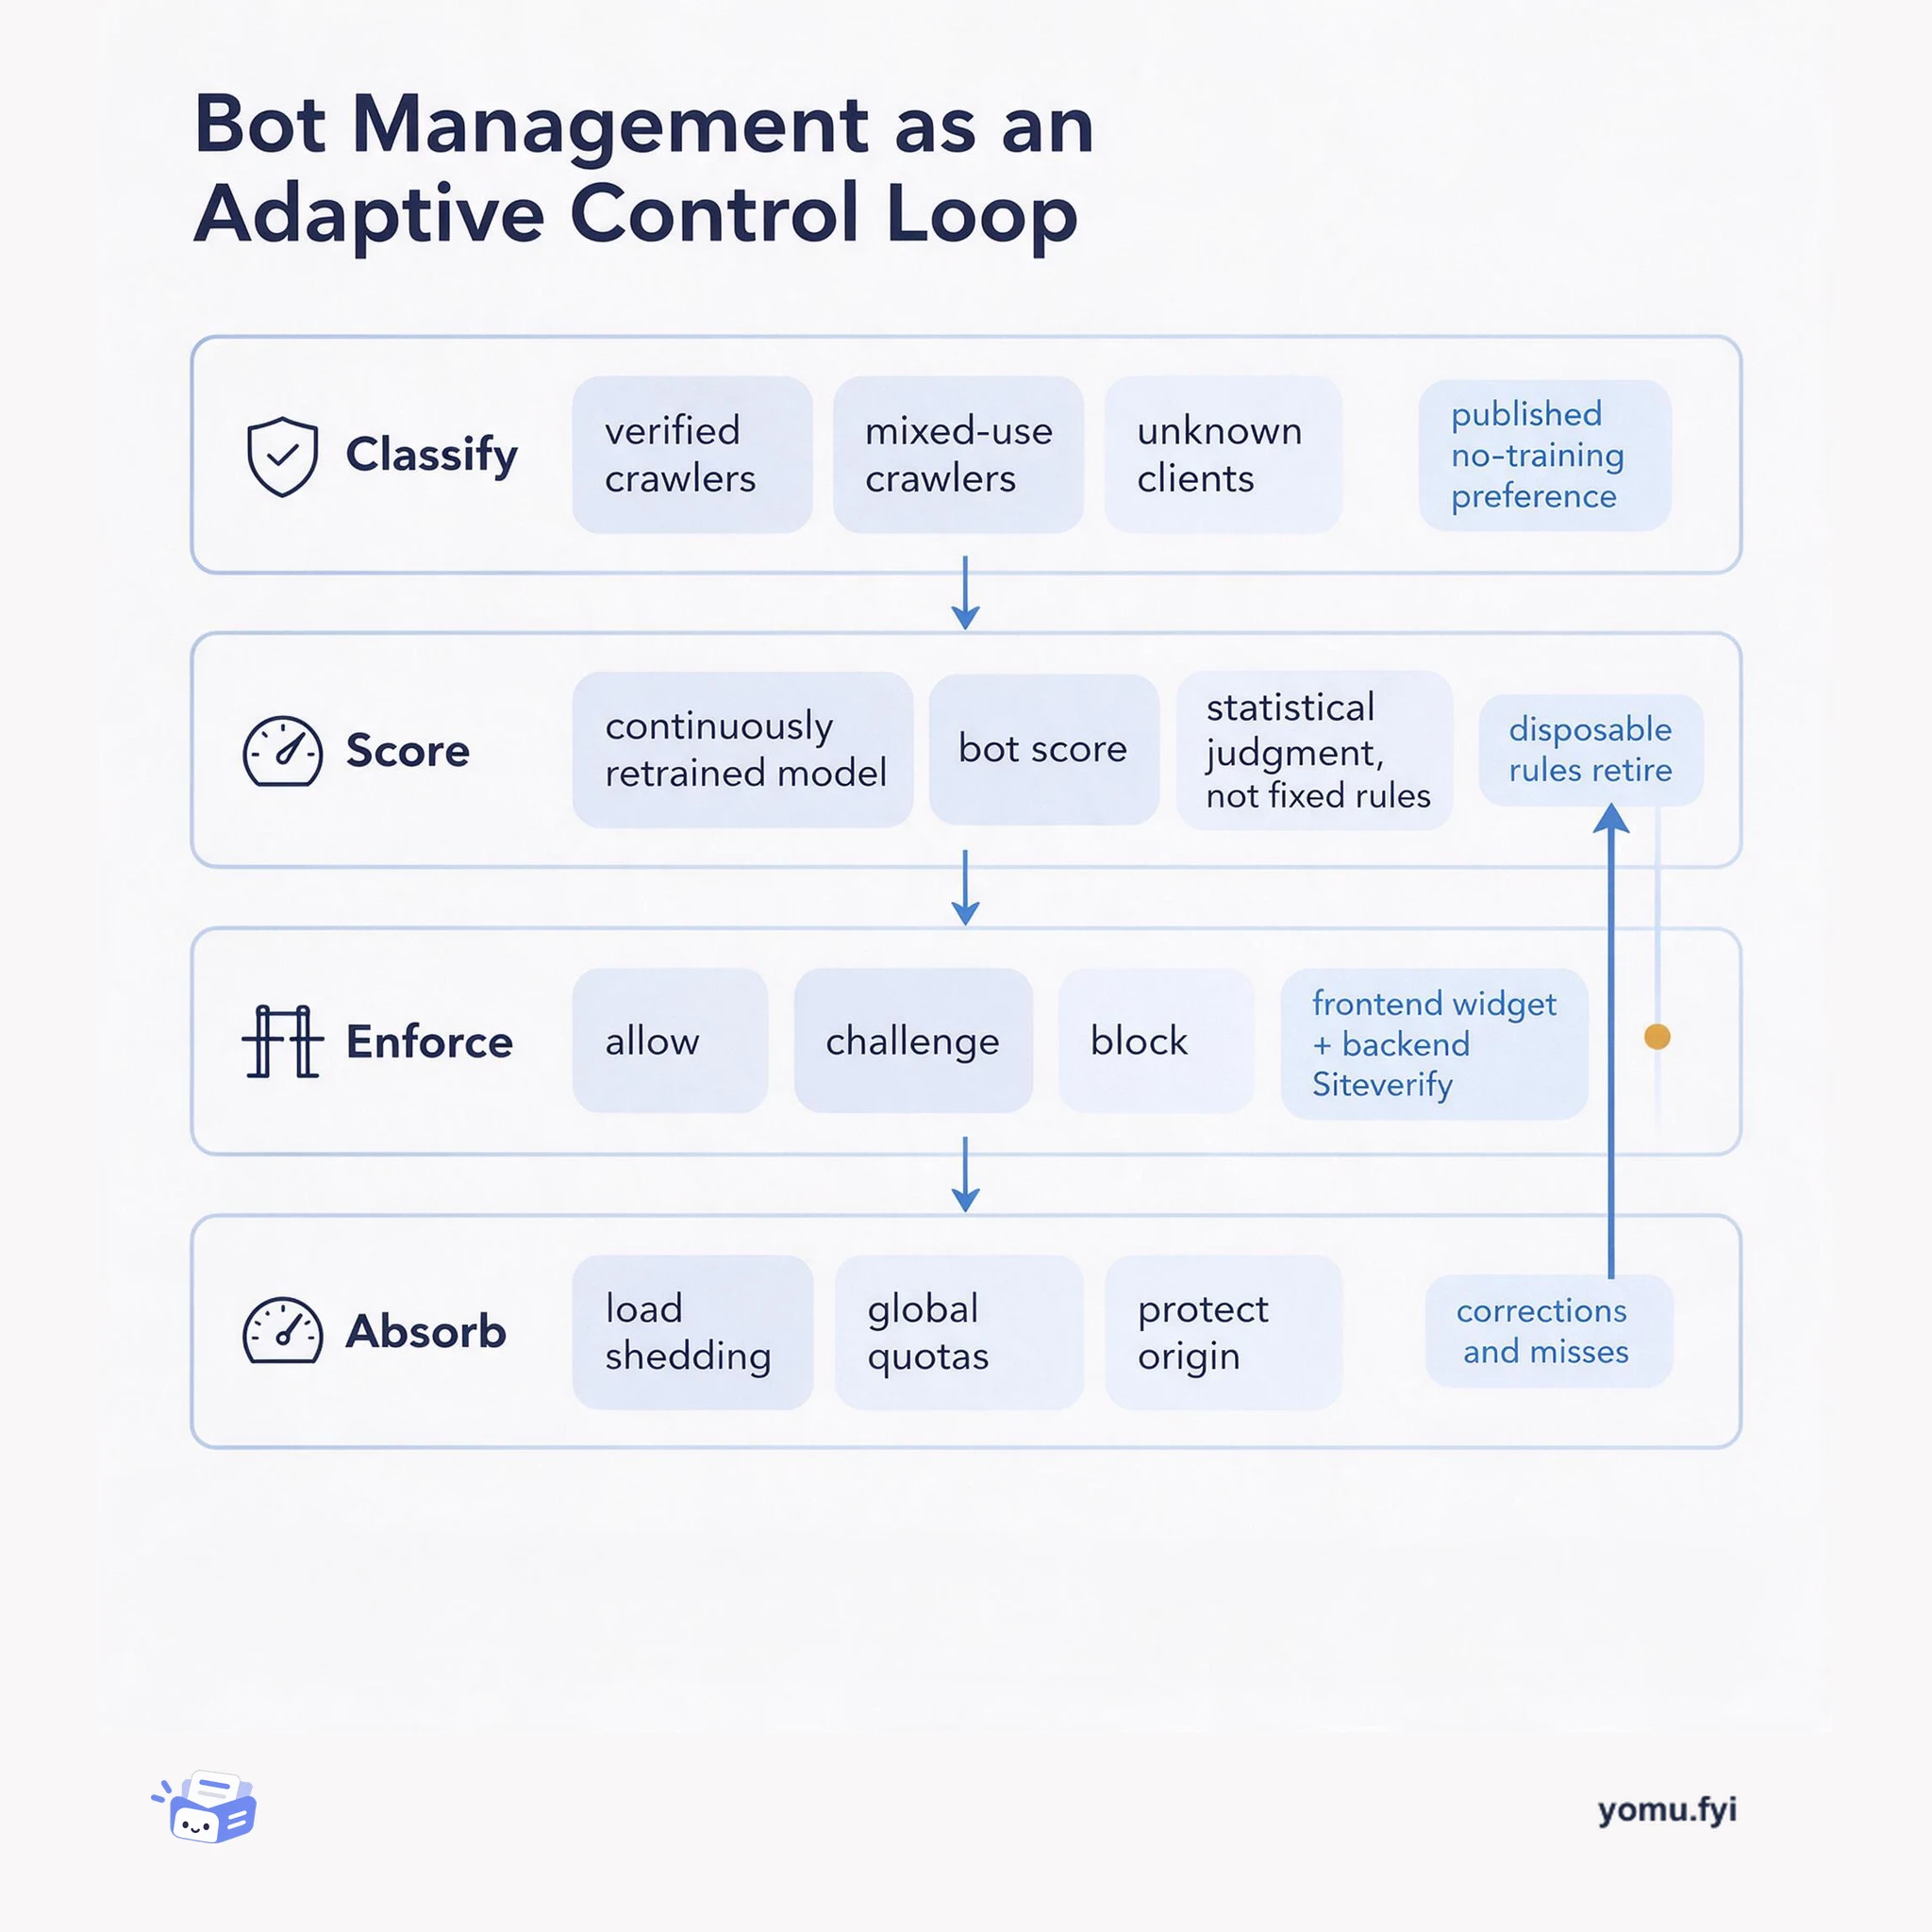
Bot Management as an Adaptive Control Loop
Bot management is an architecture, not a rule list: classify traffic, score it with continuously retrained models, enforce with challenges or blocks, then feed the outcomes back into the model.
Loading…
Topic
49 posts about Cloudflare. Every summary links to the original.
See the idea
Bot management is an architecture, not a rule list: classify traffic, score it with continuously retrained models, enforce with challenges or blocks, then feed the outcomes back into the model.
The Good Stuff
Paid picks we use ourselves. Links carry a referral code — a subscription through one earns us a commission at no extra cost to you.
Newest first
Cloudflare launched K2, a serverless event streaming service in public beta, to decouple producers and consumers in distributed systems. K2 stores events as an ordered log, allowing independent consumers to read at their own pace without losing data. Under the hood, it builds a partitioned durable log on top of R2 object storage, using atomic operations for ordering. Produce latency at the 99th percentile is about 1 second due to batching writes to R2 segments. K2 is available now for Workers Paid accounts with a 10GB storage limit and 30 MB/s produce per stream, with no billing during beta.
Cloudflare announced Artifacts, a programmable versioned filesystem speaking Git, is now in open beta for Workers Paid customers. Aimed at an era where AI agents write more code, Artifacts offers primitives for per-agent or per-task repositories, forking, versioned storage, and Git operations. New capabilities include deploying Artifacts repos to Workers via Workers Builds, managing repos from Workers with bindings, subscribing to push events for CI or review, setting US/EU data jurisdiction, and viewing metrics. Cloudflare is hosting a competition to build the next Git platform on Artifacts, requiring a 5-10 minute video and permissively licensed source code that reimagines agent coordination, review, and concurrent changes. Submissions close October 14, 2026; the first-place team wins $25,000 in Cloudflare credits and a trip to Cloudflare Connect, with three teams invited to San Francisco.
Cloudflare Workers now provides opt-in support for post-quantum cryptographic algorithms ML-KEM and ML-DSA within the Web Crypto API, including ML-KEM-768, ML-KEM-1024, ML-DSA-44, ML-DSA-65, and ML-DSA-87. These algorithms enable key encapsulation via encapsulateBits and decapsulateBits, and signatures via sign and verify, along with helper APIs like getPublicKey and SubtleCrypto.supports for feature detection. The implementation is gated behind the webcrypto_modern_algorithms compatibility flag and is based on a draft WICG specification, meaning it is opt-in while the specification is still moving. Developers can now use native primitives instead of bundling separate cryptographic code, reducing application size and maintenance burden for developers. Libraries such as panva/jose for JWTs and panva/hpke for HPKE can delegate ML-KEM and ML-DSA to the runtime, enabling experimentation with post-quantum protocols and preparing for the migration.
Cloudflare announced the general availability of Basin, a serverless data analytics platform built on Apache Iceberg and R2 Object Storage. Basin consists of three integrated products: Pipelines for ingesting and transforming events via SQL, Catalog for managing Iceberg metadata and automatic table maintenance, and SQL for distributed querying. The platform emphasizes speed with instant resource creation and query execution, scalability through metadata compaction and statistics-driven query planning, and openness by supporting any Iceberg-compatible engine like DuckDB and Snowflake. Basin offers cost efficiency with zero egress fees and usage-based pricing, charging only when data is ingested, processed, or queried. Early adopters have used Basin for use cases including real-time e-commerce optimization, billing metrics storage, and infrastructure telemetry analysis.
Cloudflare’s Impact programs have reached $100 million in donated services, protecting journalists, governments, election bodies, and public schools. The programs began as free services for developers and small businesses but evolved after discovering that some free customers doing essential work faced large attacks. Project Galileo, launched in 2014, now includes over 3,500 domains in 120 countries and blocked over 38.5 billion cyberattacks in 2025; a 2026 report found participants faced vulnerability exploit attempts at seven times the average rate. Other programs include the Athenian Project for election websites in 33 U.S. states and eight countries, Cloudflare for Campaigns with over 530 websites, and support for critical infrastructure like public schools and Ukraine. Cloudflare is expanding beyond cybersecurity to help public interest groups adapt to AI, including a hackathon for journalists that produced winning tool AIdas for studying AI bias, and a non-profit startup program.
Cloudflare Registrar introduced a redesigned domain search that shows every supported extension and responds progressively as the user types. The search gathers availability evidence from prepared datasets, DNS, and live registry checks, updating only changed results via WebSocket deltas. The system uses Workers, Durable Objects, and Workers KV on Cloudflare’s developer platform to coordinate more than 420 extension checks per query. The Registrar API beta now includes a sandbox for testing, transfer support, and an extensions endpoint with registry requirements. Agents can search, register, or transfer domains through the MCP or the newly launched cf CLI with natural-language prompts.
Cloudflare announced the Monetization Gateway closed beta, enabling domain owners to charge AI agents per request for websites, APIs, MCP tools, or datasets. The gateway uses the HTTP 402 Payment Required status code to allow inline payment without redirects or separate payment APIs. Sellers define pricing rules matching request parts and choose from several schemes, with settlement on the Base blockchain using USDC via Coinbase’s x402 Facilitator. Customer use cases include Cloudflare AI Gateway for inference, Ceramic.ai for web search, Stocktwits for stock signals, and API2PDF for document conversion. The beta is available to eligible U.S.-based sellers and buyers, with plans to support additional geographies and payment rails over time.
AI answer engines can read a publisher’s page and deliver a summary without the reader ever visiting the site, costing the publisher the visit and its associated revenue. Most publishers cannot negotiate individual licensing deals, and no AI company can contract with millions of sites. Pay Per Use, now in beta, is Cloudflare’s system that lets a buyer define a specific use of content and a price, and lets each publisher choose whether to accept that offer. The buyer reports each downstream use through a single Cloudflare API endpoint, and Cloudflare then bills the buyer and pays the publisher monthly. Publishers can track estimated earnings and usage by buyer and domain in the Cloudflare dashboard, with planned future enhancements such as report context like keywords or product type.
Cloudflare AI Gateway’s User Insights now provides context beyond model names and request counts, using a dedicated Worker to classify conversations by task type such as coding, research, summarization, or formatting. The “model overkill” view identifies conversations where a high-capability reasoning model is used for simple tasks, showing which users or agents are driving that usage and the associated cost. Teams can analyze conversation turns to see how many back-and-forth exchanges a task requires, helping uncover inefficiencies in prompts or workflows. The Potential Savings view and Auto Router (closed beta) use task and model-fit signals to automatically route requests to appropriate models without a separate rule for each workload. These features are free for AI Gateway users and require stable user_id and session_id for analysis, with optional Access integration.
Cloudflare Containers have been rebuilt to meet the needs of agent sandboxes, which require on-demand creation, fast startup, and the ability to pause and resume. The new durable_object scheduling policy lets application code choose each sandbox’s image and instance type at runtime, replacing the previous deploy-time configuration. A redesigned runtime reduces median container startup from over four seconds to 648 milliseconds, and filesystem snapshots are available in public beta for saving and restoring workspaces. Each container retains its Durable Object as a persistent, programmable controller that manages its lifecycle and outbound traffic. These changes make Containers a more flexible complement to Workers and Durable Objects for agents needing a full Linux workspace.
More than half of Internet traffic is now automated, and AI agents are the fastest-growing part of it, with daily requests on Cloudflare’s network growing by more than 1,700% over the past year. This second audience consumes bandwidth without generating ad impressions or subscriptions, causing revenue per request to fall while costs rise. Cloudflare is giving site owners tools to see who is visiting, set terms per bot type, and charge for access. These include AI Crawl Control, Web Bot Auth for cryptographically verified agents, Disallow AI Training to block training without losing search indexing, and Pay Per Use to pay publishers when content is actually used. The goal is to build open standards so any site can set its terms and get paid, rather than a few companies controlling discovery and payment.
Cloudflare, which terminates TLS for millions of domains and sits in front of over 20% of global Internet request traffic, announced its intent to become a public certificate authority (CA) during Birthday Week 2026. The company has applied for inclusion in the Chrome, Apple, Microsoft, and Mozilla root programs and signed a definitive agreement to acquire an established root from GlobalSign. This acquisition ensures certificate compatibility with older clients that a fresh root would never reach, addressing the long tail of devices where avoidable breakage occurs. Cloudflare plans to be among the first CAs to issue production Merkle Tree Certificates (MTCs) in early 2027, targeting post-quantum readiness as part of Chrome’s Quantum-resistant Root Program. The CA will be ACME-first, require ACME Renewal Information (ARI) support for issuance, and operate transparently with reproducible builds of signing software and a public dashboard.
An incident in July 2026 showed AI agents autonomously compromising OpenAI and Hugging Face infrastructure, chaining vulnerabilities and credentials over months before executing a final compromise in under 13 hours. Cloudflare argues that application security must become a continuous, connected system rather than isolated controls, because individual alerts miss the complete campaign. It introduces a four-stage framework: discover and prioritize risks, govern access and agent behavior, protect applications at runtime, and investigate, respond, and learn. New capabilities include LLM-based WAF penetration testing, expanded threat intelligence for all customers, automated positive security deployment, and an Autonomous Security Operation framework with three agent stages. Cloudflare’s network visibility across over 20% of the web enables correlating isolated signals into coordinated attack timelines, turning every investigation into stronger protection.
Cloudflare built a WAF tester that uses frontier AI models to iteratively mutate attack payloads based on real-time response feedback. The tester, implemented in Python, orchestrates an LLM proposal and review loop against an authorized customer staging environment protected by Cloudflare’s WAF. It ran 45 scenarios across six attack categories—XSS, SQLi, CMDi, SSRF, path traversal/LFI, and Log4j—starting from known blocked exploits and varying encoding, request placement, or destination representation. The vast majority of 1,107 recorded attempts were blocked; the few non-blocked requests were triaged by humans and used to create new detections that harden security for all Cloudflare customers. The post stresses that a WAF bypass still needs an exploitable application to succeed, so patching software remains essential, and suggests combining Managed Rules, Attack Signature Detection, and positive security controls for defense in depth.
Cloudflare introduced Threat Signals, a free agentic skill layer for open-source threat intelligence available to every account. The product targets the unstructured-reporting problem: converting research posts into indicators that security tools can consume while preserving the context that explains their relevance. A skill encodes detailed instructions that capture how an experienced analyst handles one part of the job, and it runs identically on every report. The agentic skills summarize reports, surface key context, extract and normalize indicators of compromise, and apply tags within a private, account-scoped dataset. This approach standardizes analyst expertise into repeatable, context-preserving processing for threat reports.
Cloudflare introduced new post-quantum cryptography visibility tools in its Application Security and Logs products, including Logpush, Log Explorer, and the HTTP Traffic Analytics dashboard, to help customers monitor encryption adoption. These tools surface the key exchange algorithm negotiated on every incoming request, enabling customers to audit their post-quantum posture, assess compliance, and identify cryptographic gaps across their domains. The primary post-quantum algorithm in TLS 1.3 is X25519MLKEM768, a hybrid of classical ECDHE over curve X25519 and the post-quantum ML-KEM, which provides belt-and-suspenders security against harvest-now-decrypt-later attacks. Cloudflare Radar data shows about 70% of browser-generated traffic uses post-quantum encryption on the visitor-to-Cloudflare connection, but only 15% of origin connections to Cloudflare use hybrid ML-KEM. For legacy origin servers that cannot support modern post-quantum cryptography, Cloudflare Tunnel can tunnel traffic over TLS 1.3 with X25519MLKEM768 without requiring any upgrade to the origin server itself.
Cloudflare launches Application Profiles, a positive security feature that learns the expected structure of HTTP requests and identifies deviations. By analyzing path variables, query parameters, headers, cookies, and JSON body fields, the system builds a profile of valid data types, numeric ranges, string lengths, UUIDs, and enums. This approach reduces attack surface by blocking non-conforming requests without relying solely on known attack signatures, addressing the growing threat of AI-generated payloads. The feature extends Schema Learning and Schema Validation, previously available for APIs, to web applications. Profiles are automatically updated weekly as traffic changes. Customers can review violations in Security Analytics and create rules to enforce blocking, starting with observation mode; a closed beta is open to invited Enterprise customers without API Security.
Cloudflare has identified a design flaw in IPsec that allows a quantum attacker to downgrade post-quantum-protected connections to classical cryptography. The attack exploits the fact that IKEv2 endpoints sign only their outbound messages rather than the full handshake transcript. This vulnerability requires a quantum computation in real time during the handshake, and resource estimates for such attacks have decreased, prompting Cloudflare to move its transition deadline to 2029. To mitigate this, Cloudflare worked with the IETF to develop a full transcript authentication extension for IKEv2 that prevents downgrade attacks. The extension is now available in beta for Cloudflare WAN and Magic Transit customers on an opt-in basis.
Cloudflare introduced cf, a new CLI that provides access to the entire Cloudflare API surface of over 3,000 operations, far exceeding Wrangler’s roughly 280 commands. Cf is designed primarily for AI coding agents, which account for nearly half of Wrangler usage, and defaults to JSON output with condensed formatting to minimize token consumption. The CLI includes a natural language search command, cf cli search, that helps agents discover the right operation without bloating context, and uses TypeScript-based configuration via cloudflare.config.ts for type safety. Cf is generated by Forge, Cloudflare’s internal pipeline that produces CLI commands from OpenAPI schema annotations, enabling consistent and comprehensive API coverage. The open beta is available globally via npm, and cf adopts Vite as its default local development server, with a migration path from Wrangler and maintenance support for 18 months after beta ends.
Cloudflare has released the BEACON dataset, an anonymized collection of billions of real-user performance measurements from 10,000 of the largest websites. The dataset reports Core Web Vitals (LCP, CLS, INP) with full histograms, enabling analysis of any percentile including the long tail. It reveals that WebKit browsers underperform Blink in 46 countries, and that resource-discovery and render-blocking contribute more to slow LCP than download time. Soft navigations in single-page applications load two to three times faster than hard navigations, but landing pages remain heavy. The dataset is publicly available on Google BigQuery and includes differential privacy via the RAPPOR algorithm to protect individual user data.
The best engineering reads, once a week.

