A malicious version of Anthropic.claude-code (2.1.313) was distributed in the Cursor VS Code extension Marketplace for about 11 hours on October 29, 2026, affecting up to 5,000 users. The extension collects host and user information, adds an attacker-controlled SSH key, attempts to enable SSH service, opens a reverse tunnel, installs persistence via a LaunchAgent on macOS or a scheduled task on Windows, and reports host details via HTTP POST to a beacon endpoint. Due to errors in the malicious code, the SSH service enablement fails on most systems without administrator privileges, but the key addition and persistence mechanisms still execute. Cursor removed the malicious version, audited the marketplace, rotated keys, and worked with the hosting provider to take the attacker’s server offline. Affected users should check for the unauthorized SSH key labeled svc-telemetry, run the provided remediation scripts, and rotate credentials from a trusted system.
Approach / What changed
Cursor removed the malicious extension from the marketplace, shut down the marketplace for audit, audited access to confirm no other tampering, rotated keys, rebuilt the marketplace, and worked with the hosting provider to take the attacker’s server offline.
Takeaways
1
The malicious extension was available for about 11 hours and affected up to 5,000 users.
2
The extension attempts to install a persistent SSH backdoor, but the SSH service enablement fails on most systems without admin rights.
3
Uninstalling the extension alone is insufficient; the payload drops standalone persistence scripts that continue running.
FAQ
How can I check if my machine is impacted?
Check for the unauthorized SSH key labeled svc-telemetry in your authorized_keys file. On macOS, run the provided grep command; on Windows, use the PowerShell command. If the key is found, your machine is impacted.
What does the malicious extension do?
It collects host and user information, adds an attacker-controlled SSH key, attempts to enable SSH service and open a reverse tunnel, installs persistence mechanisms, and reports host details to a beacon endpoint. The SSH service enablement fails on most systems without admin rights.
What should I do if I am impacted?
Isolate the host, remove the unauthorized SSH key and persistence mechanisms using the provided remediation scripts, and rotate credentials and sessions accessible from the affected host from a trusted system. Uninstalling the extension is not sufficient.
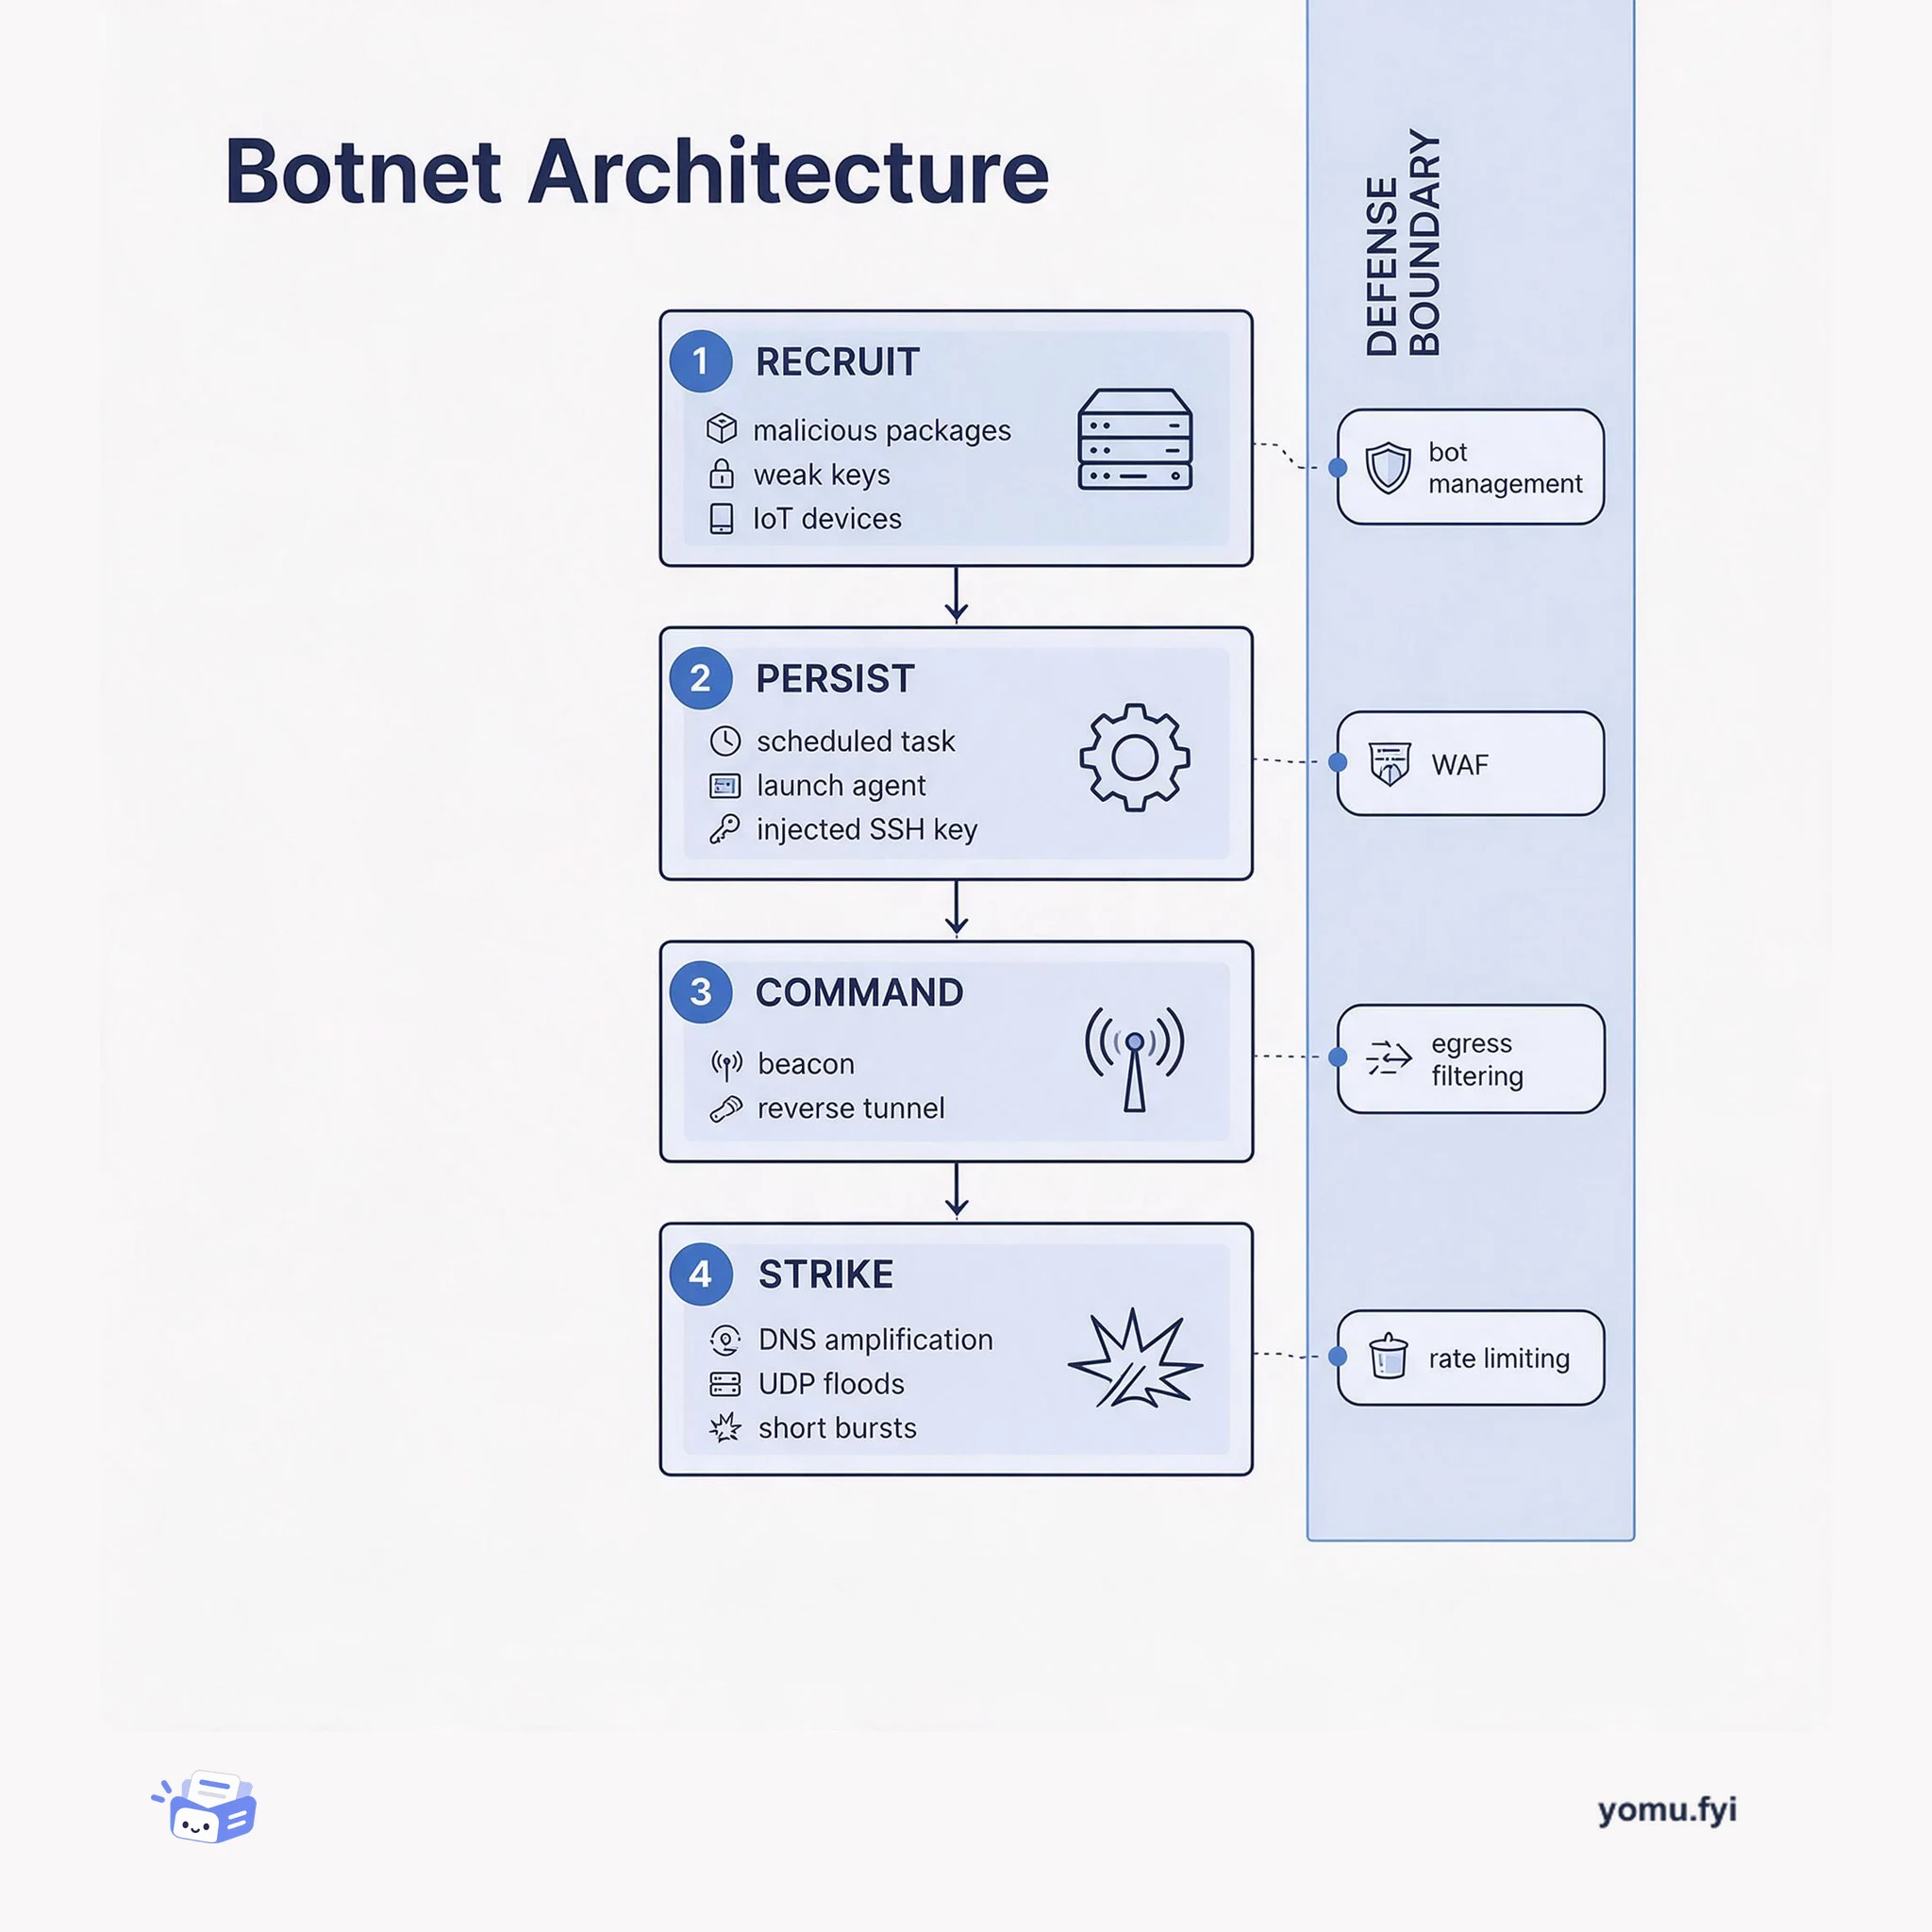
A botnet is a fleet of compromised devices organized in four layers: recruitment, persistence, command and control, and attack execution. This diagram maps how the layers connect and where defenses break the chain.
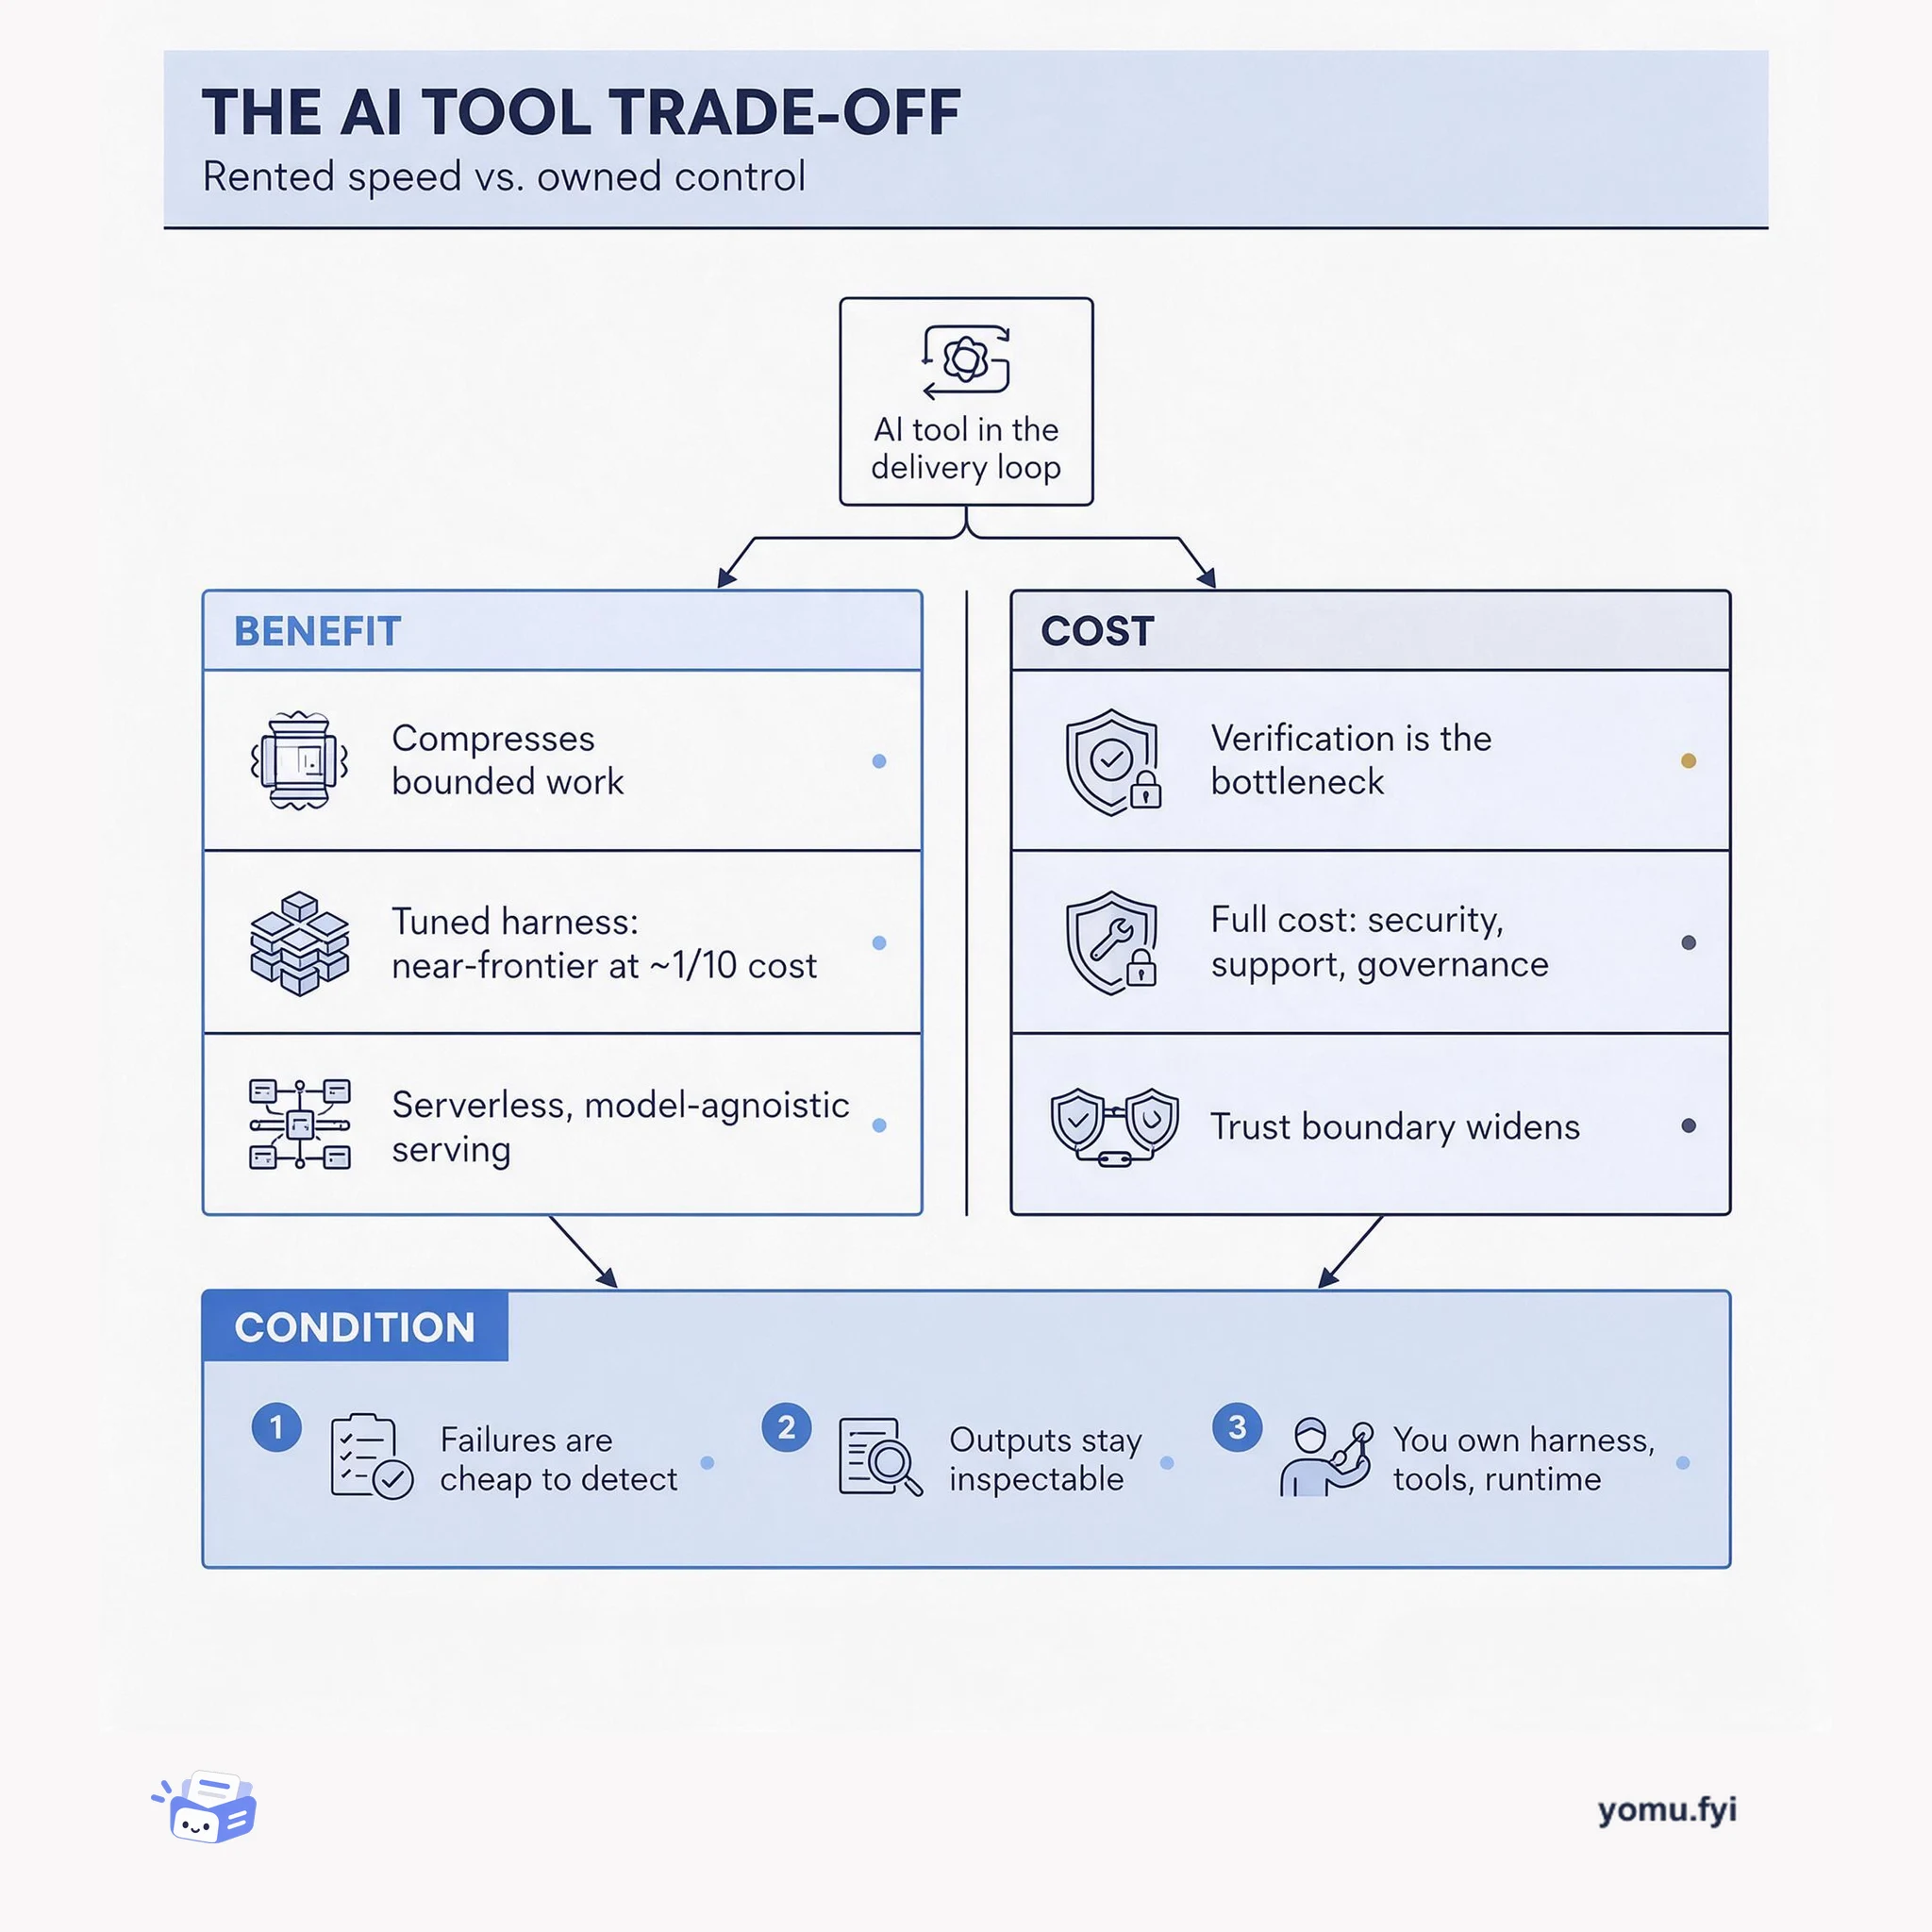
The AI tool trade-off: where AI compresses bounded work, what verification and governance really cost, and the condition that decides whether to rent capability or own the stack.
Keep reading
Related reading
The Good Stuff
Paid picks we use ourselves. Links carry a referral code — a subscription through one earns us a commission at no extra cost to you.