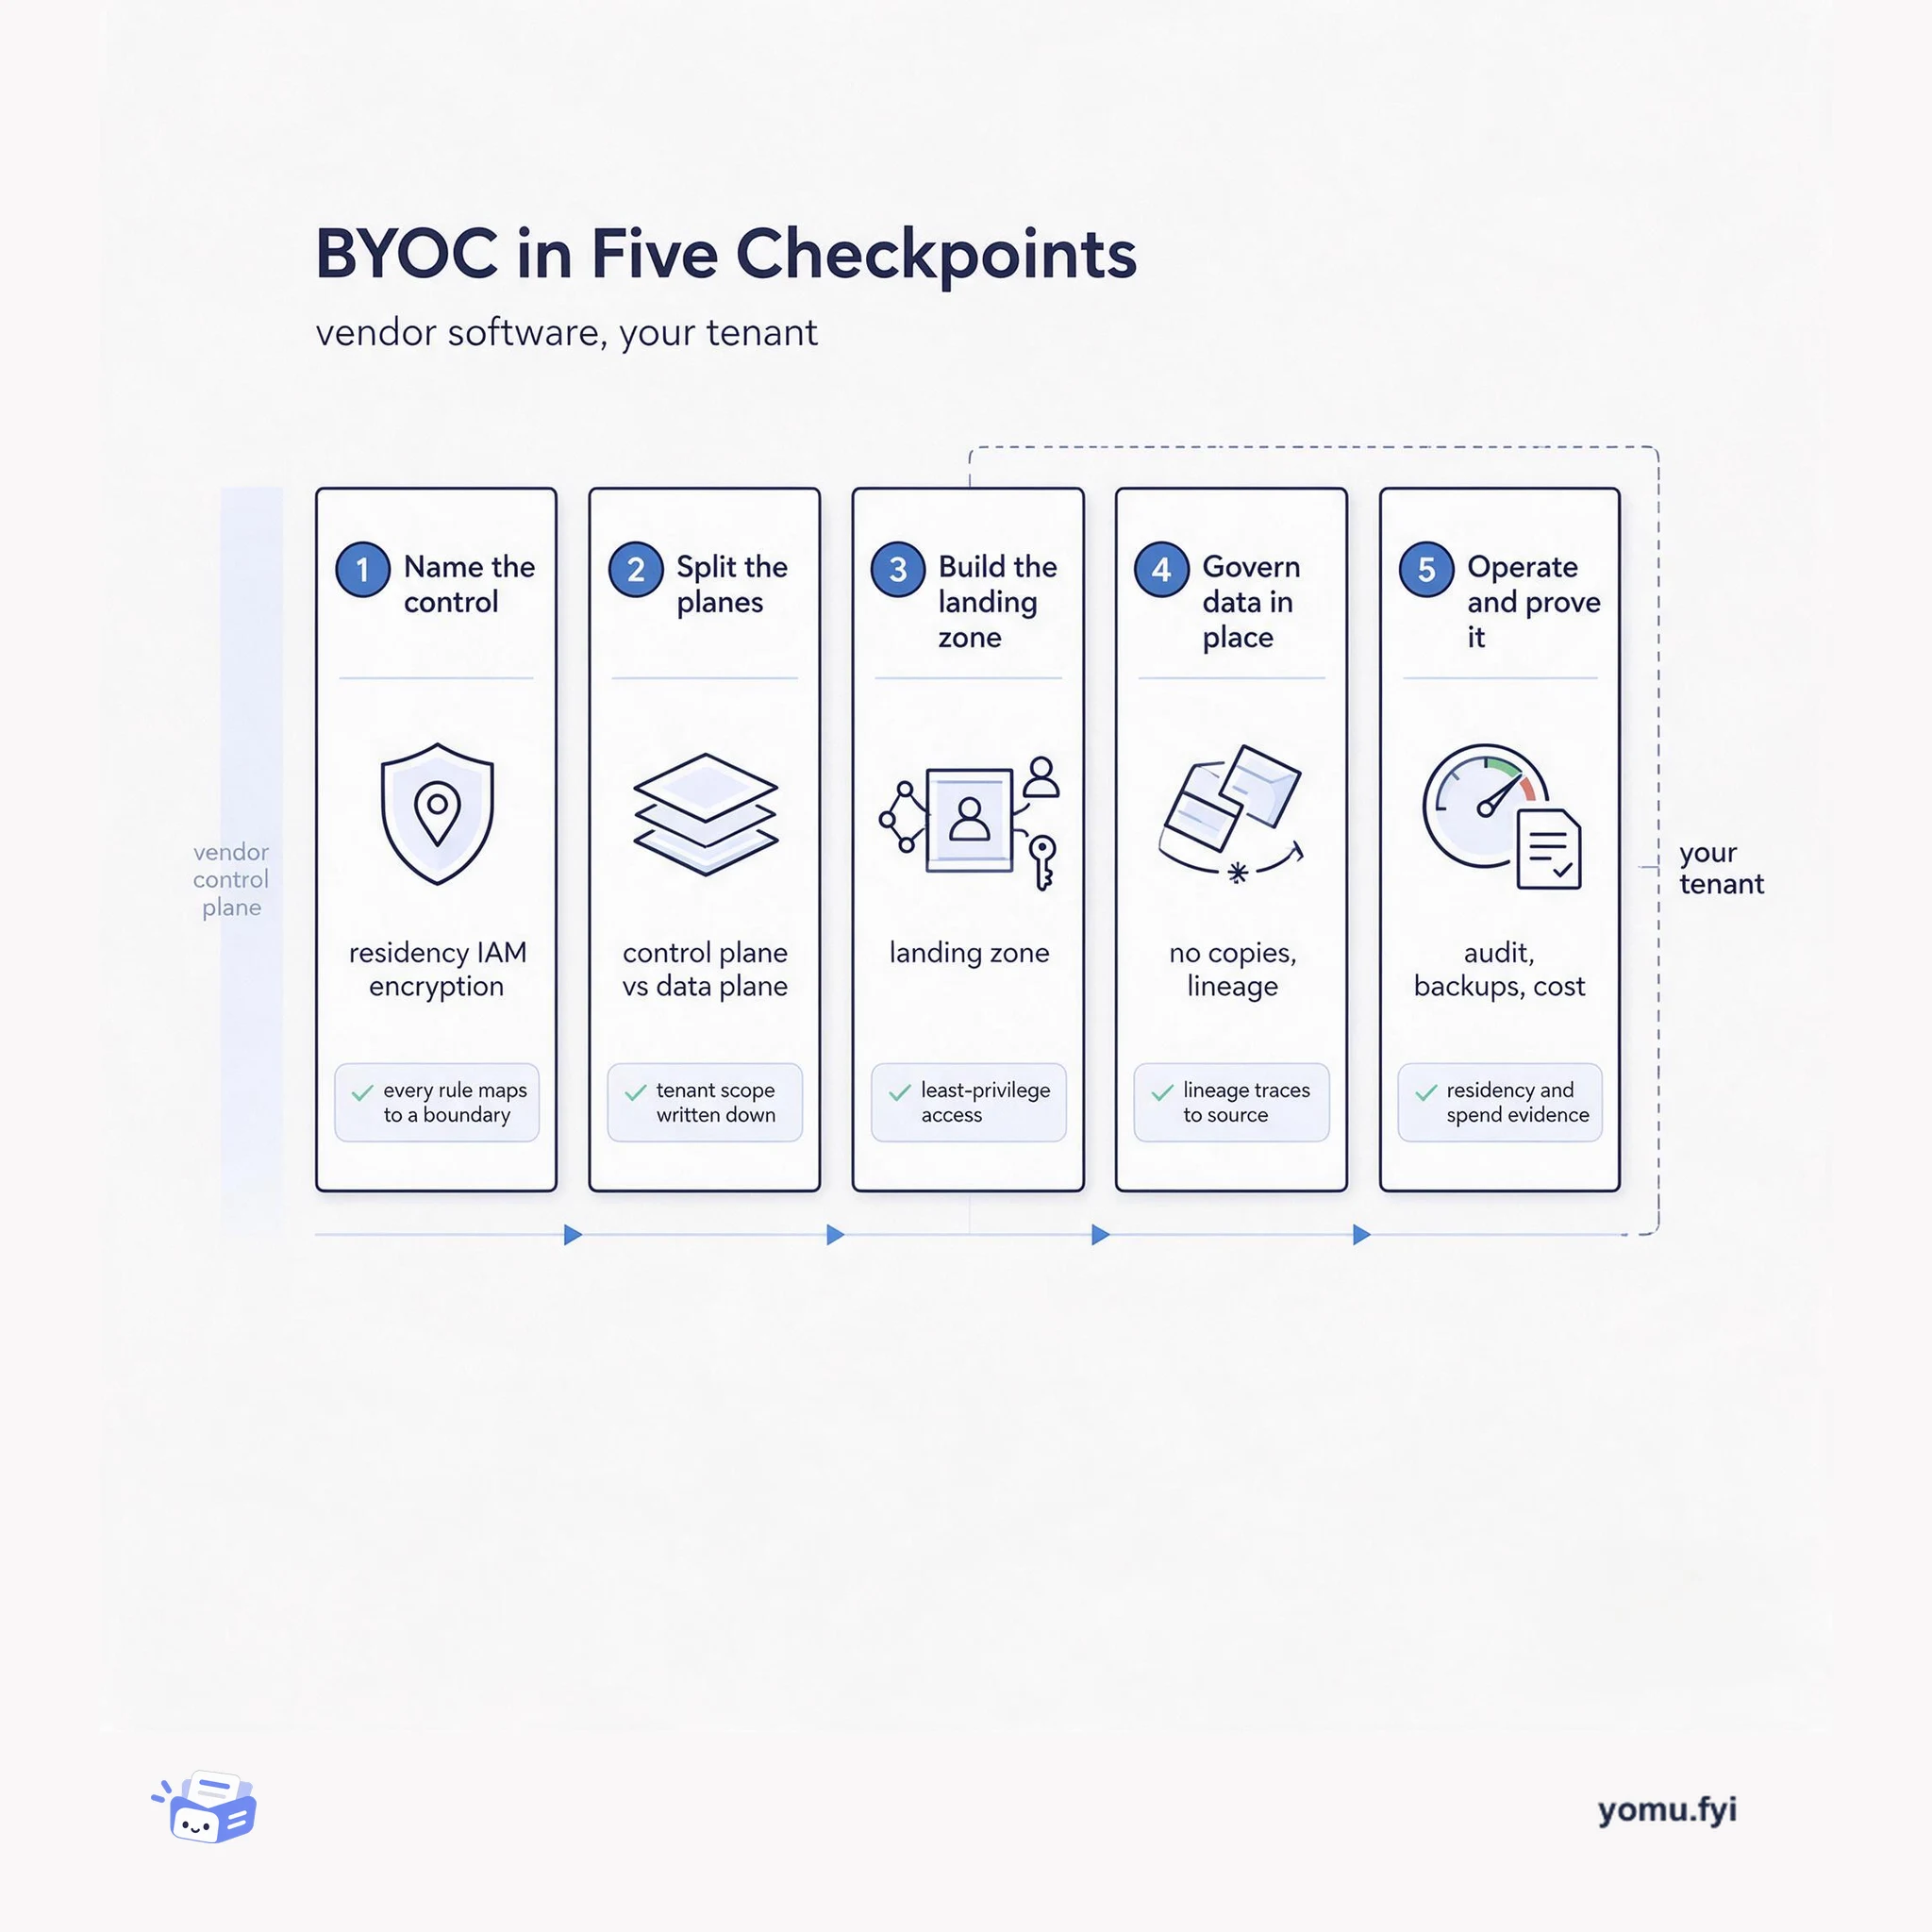
BYOC in Five Checkpoints: Name, Split, Land, Govern, Operate
A five-checkpoint walkthrough of BYOC: name the control you need, split control and data planes, build the landing zone, govern data in place, then operate inside your own tenant.
Loading…
Topic
1 post about IAM. Every summary links to the original.
See the idea
A five-checkpoint walkthrough of BYOC: name the control you need, split control and data planes, build the landing zone, govern data in place, then operate inside your own tenant.
The Good Stuff
Paid picks we use ourselves. Links carry a referral code — a subscription through one earns us a commission at no extra cost to you.
Newest first
ReadyOn describes a four-layer tenant-isolation architecture for Harmony, its multi-tenant workforce-intelligence platform on Amazon EKS, which handles payroll data, organizational hierarchies, and operational analytics. The design combines dedicated Kubernetes namespaces, Karpenter-managed tenant node pools, per-tenant Amazon VPC security groups, and dedicated Amazon Aurora databases, with RBAC, admission control, default-deny network policies, IAM Roles for Service Accounts, and tenant-scoped secrets. GitOps through Argo CD ApplicationSets provisions identical controls and continuously reverts drift, while dual taints and admission validation prevent cross-tenant scheduling. ReadyOn says adversarial exercises have blocked all six tested cross-tenant paths to date, and reports defenses across 10 threat-model stages, though shared control-plane dependencies make the layers defense in depth rather than fully independent probabilities.
The best engineering reads, once a week.

