APAC Is Not One Region: The Regionalize vs. Standardize Tradeoff
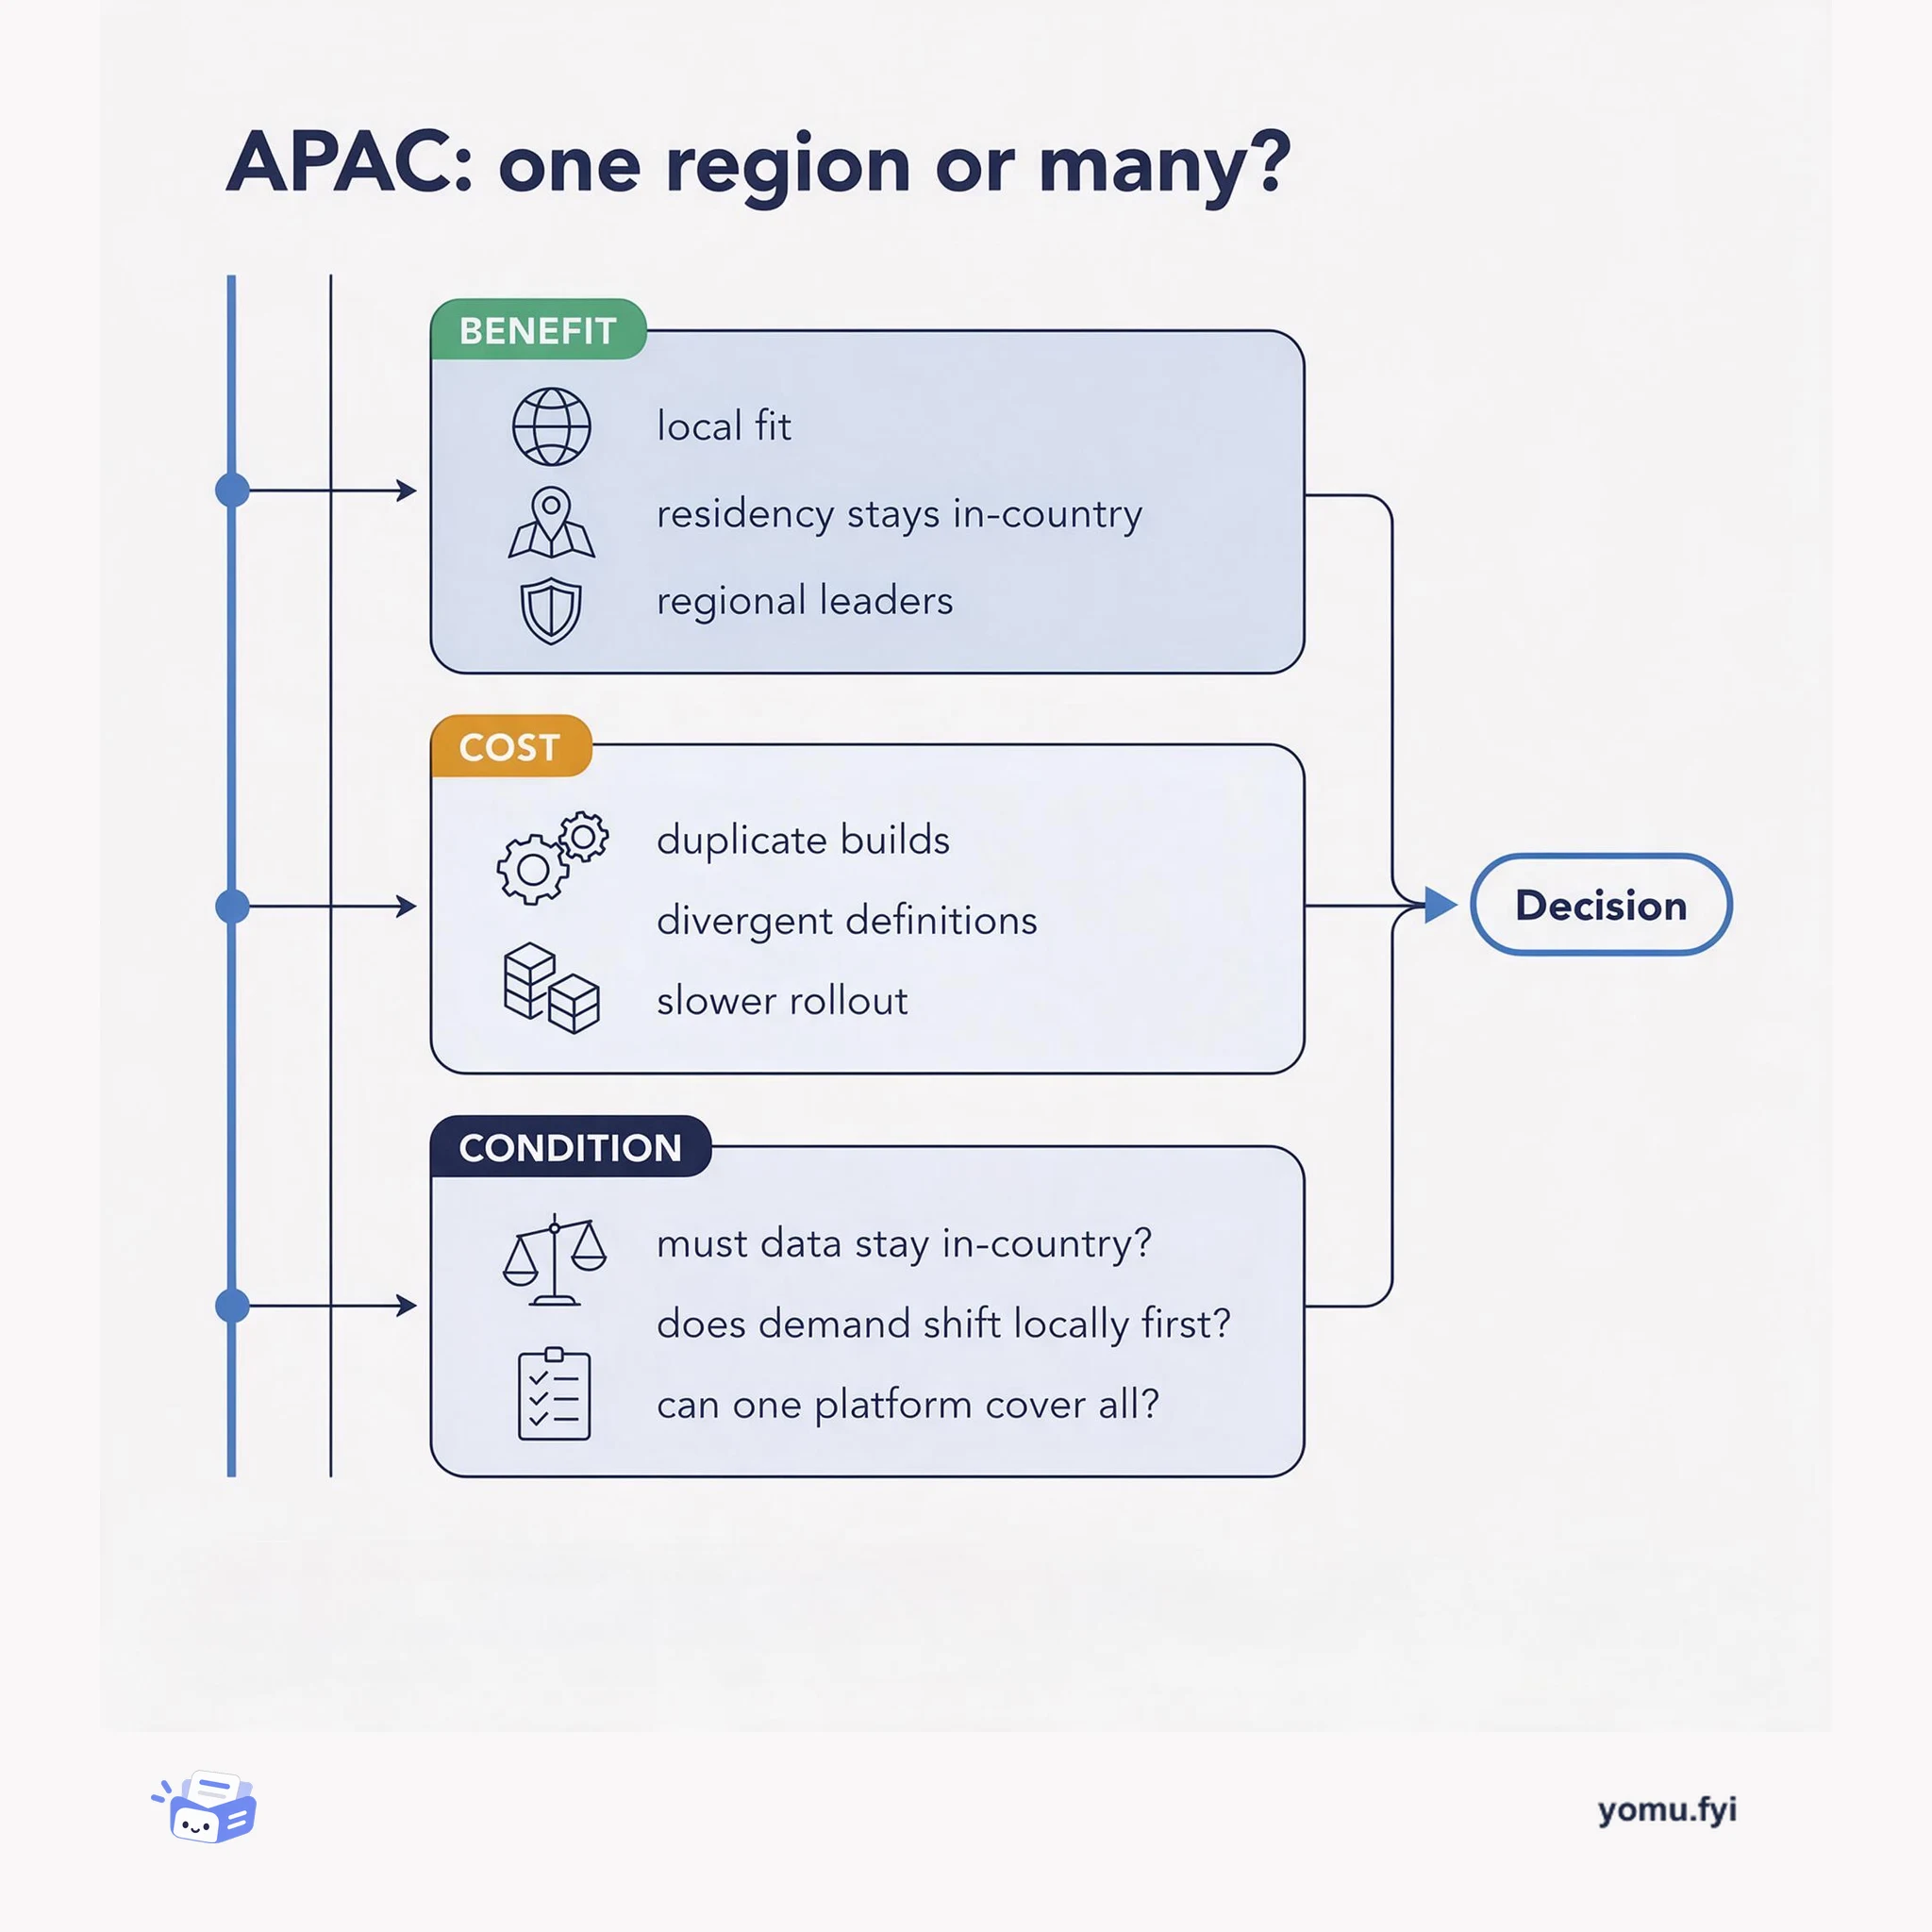
APAC is a federation of markets, not a single deployment region. This diagram maps the tradeoff between local autonomy and one shared platform, and the conditions that decide it.
Loading…
Topic
1 post about Data Sovereignty. Every summary links to the original.
See the idea
APAC is a federation of markets, not a single deployment region. This diagram maps the tradeoff between local autonomy and one shared platform, and the conditions that decide it.
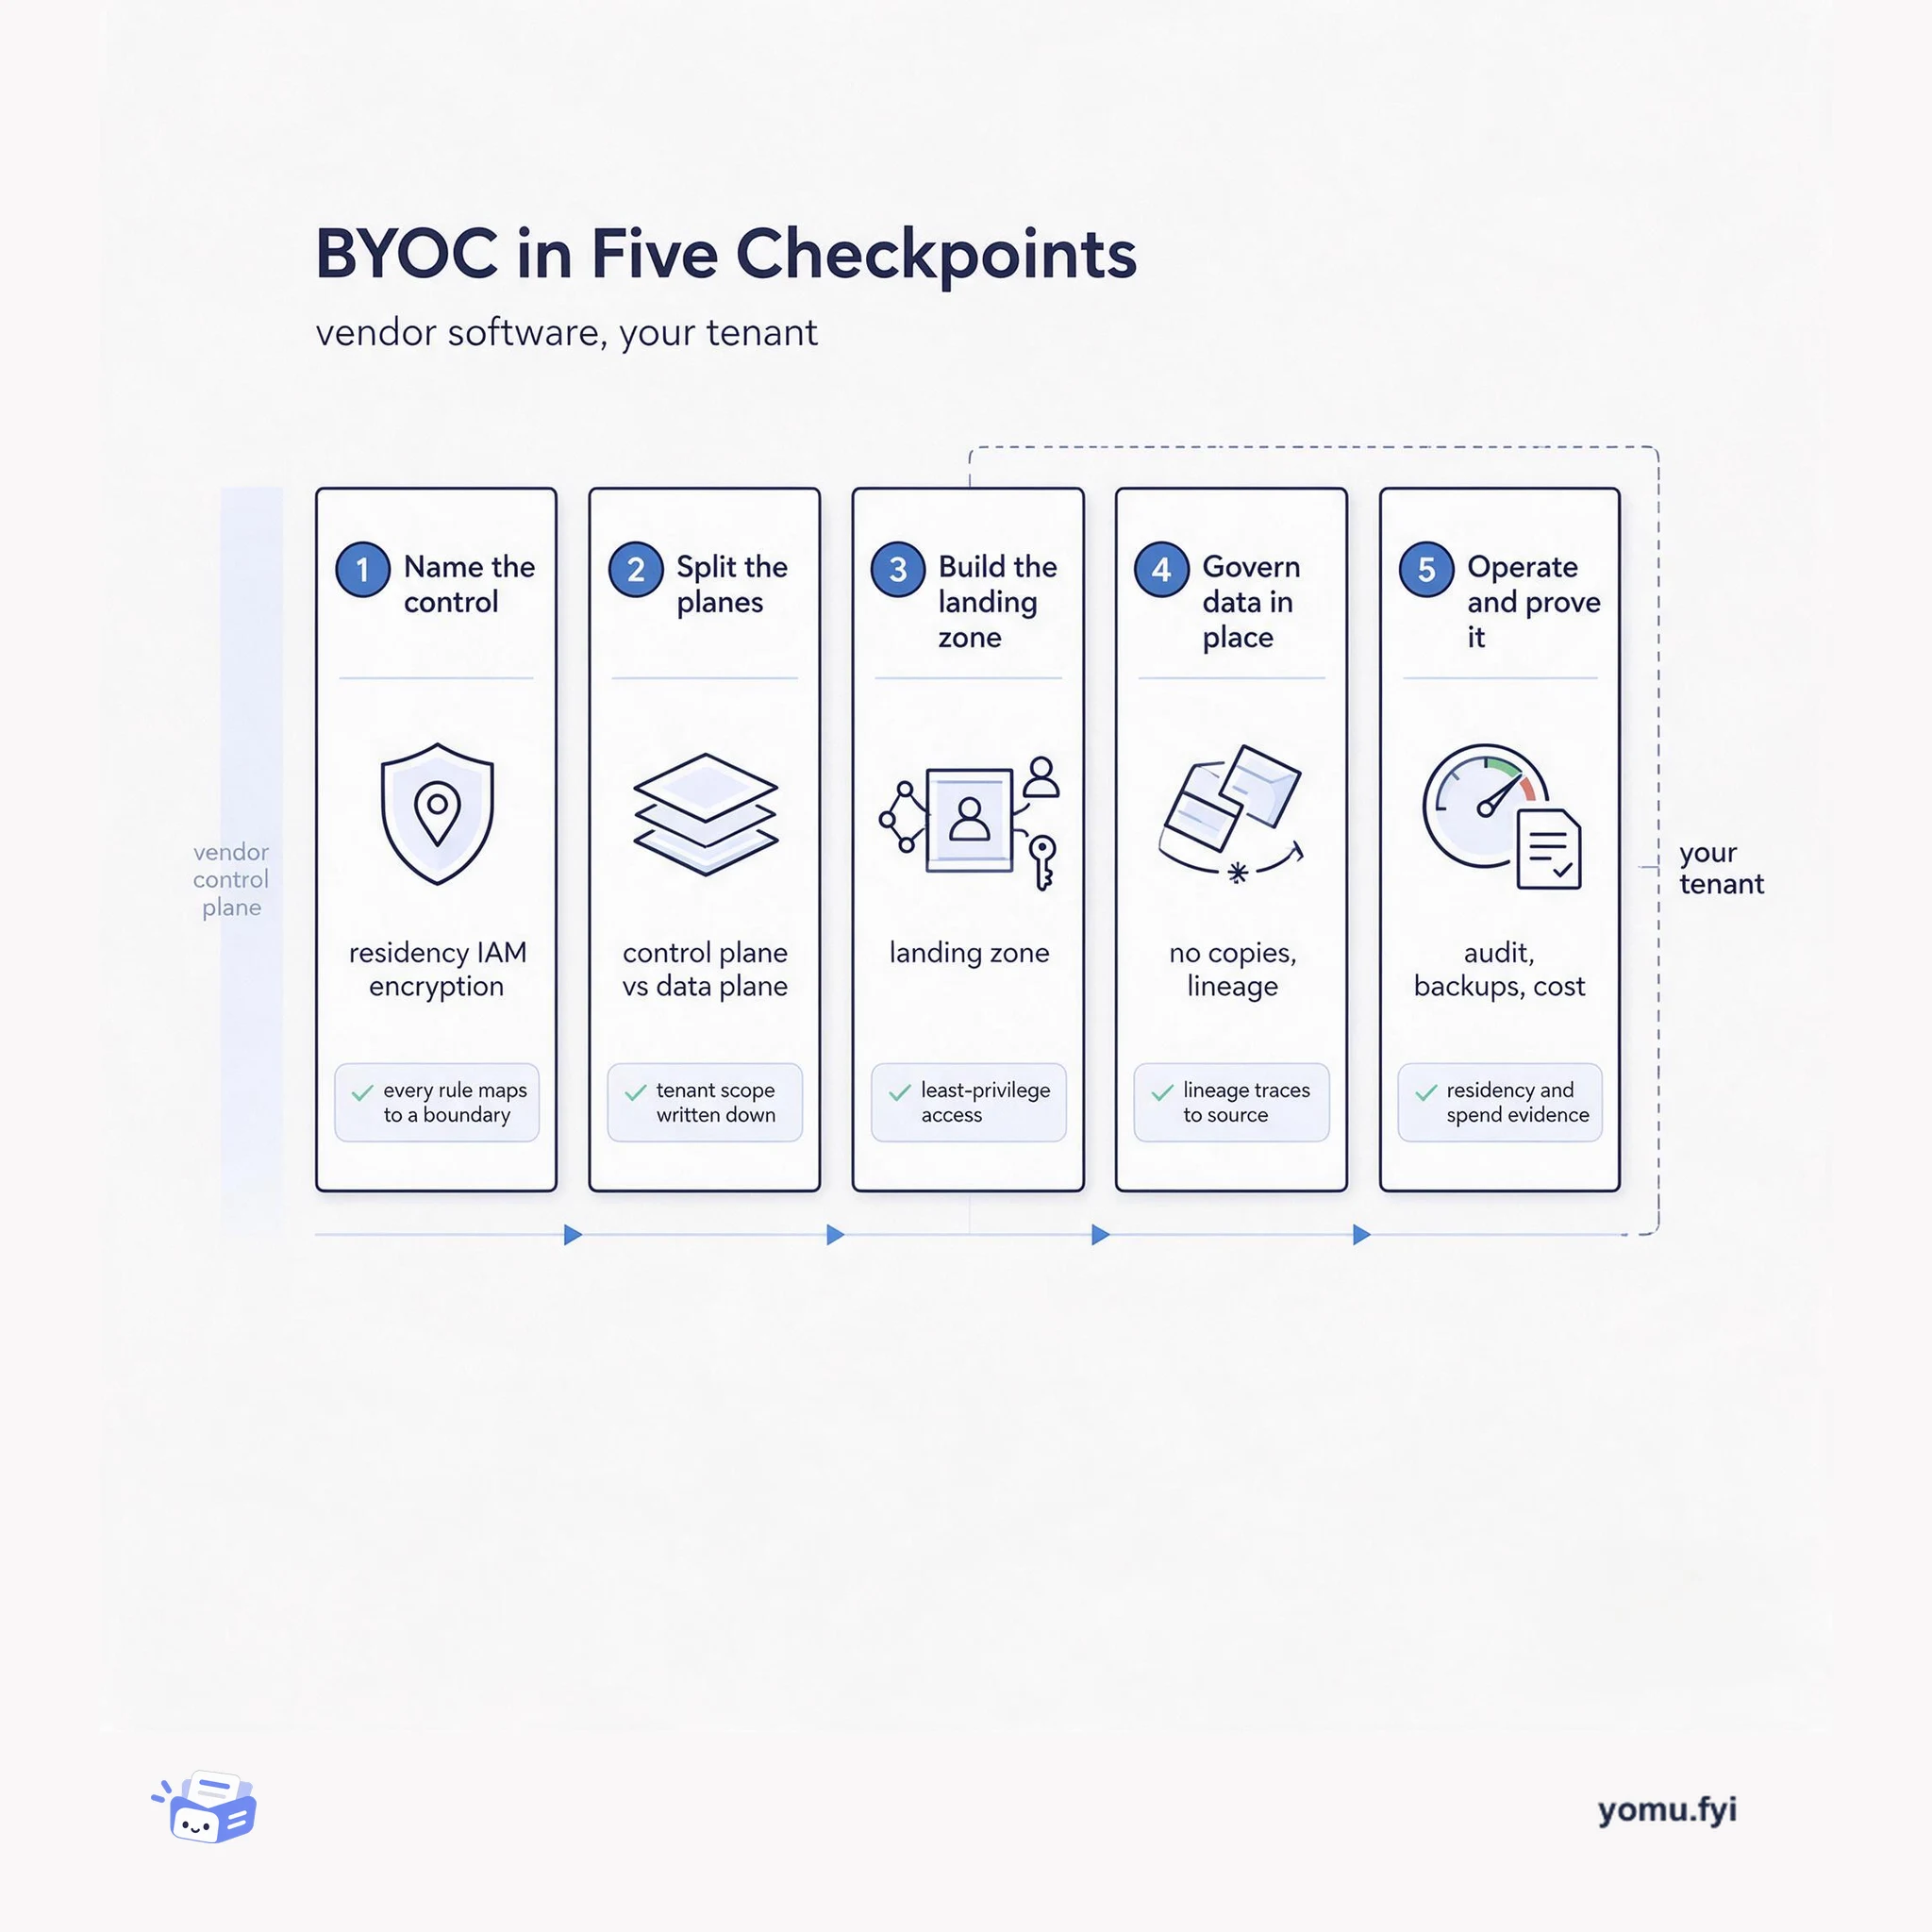
A five-checkpoint walkthrough of BYOC: name the control you need, split control and data planes, build the landing zone, govern data in place, then operate inside your own tenant.
The Good Stuff
Paid picks we use ourselves. Links carry a referral code — a subscription through one earns us a commission at no extra cost to you.
Newest first
Data sovereignty is a market expression, not a universal legal standard, and IT leaders should evaluate it through architecture and governance questions rather than a single label. The assessment covers where data resides, who can access it, how it moves, and whether control is retained, with considerations varying by jurisdiction, industry, and risk posture. Physical location is only one part of a broader control boundary that includes operations, key custody, and access paths. The article proposes five technical lenses for evaluation: jurisdiction-native data placement, in-use encryption, customer-held keys, network isolation and identity-based access, and forensic-grade audit evidence. These lenses are practical reference points for architecture decisions, not a legal test or certification checklist, and organizations should assess their own requirements with qualified counsel.
The best engineering reads, once a week.