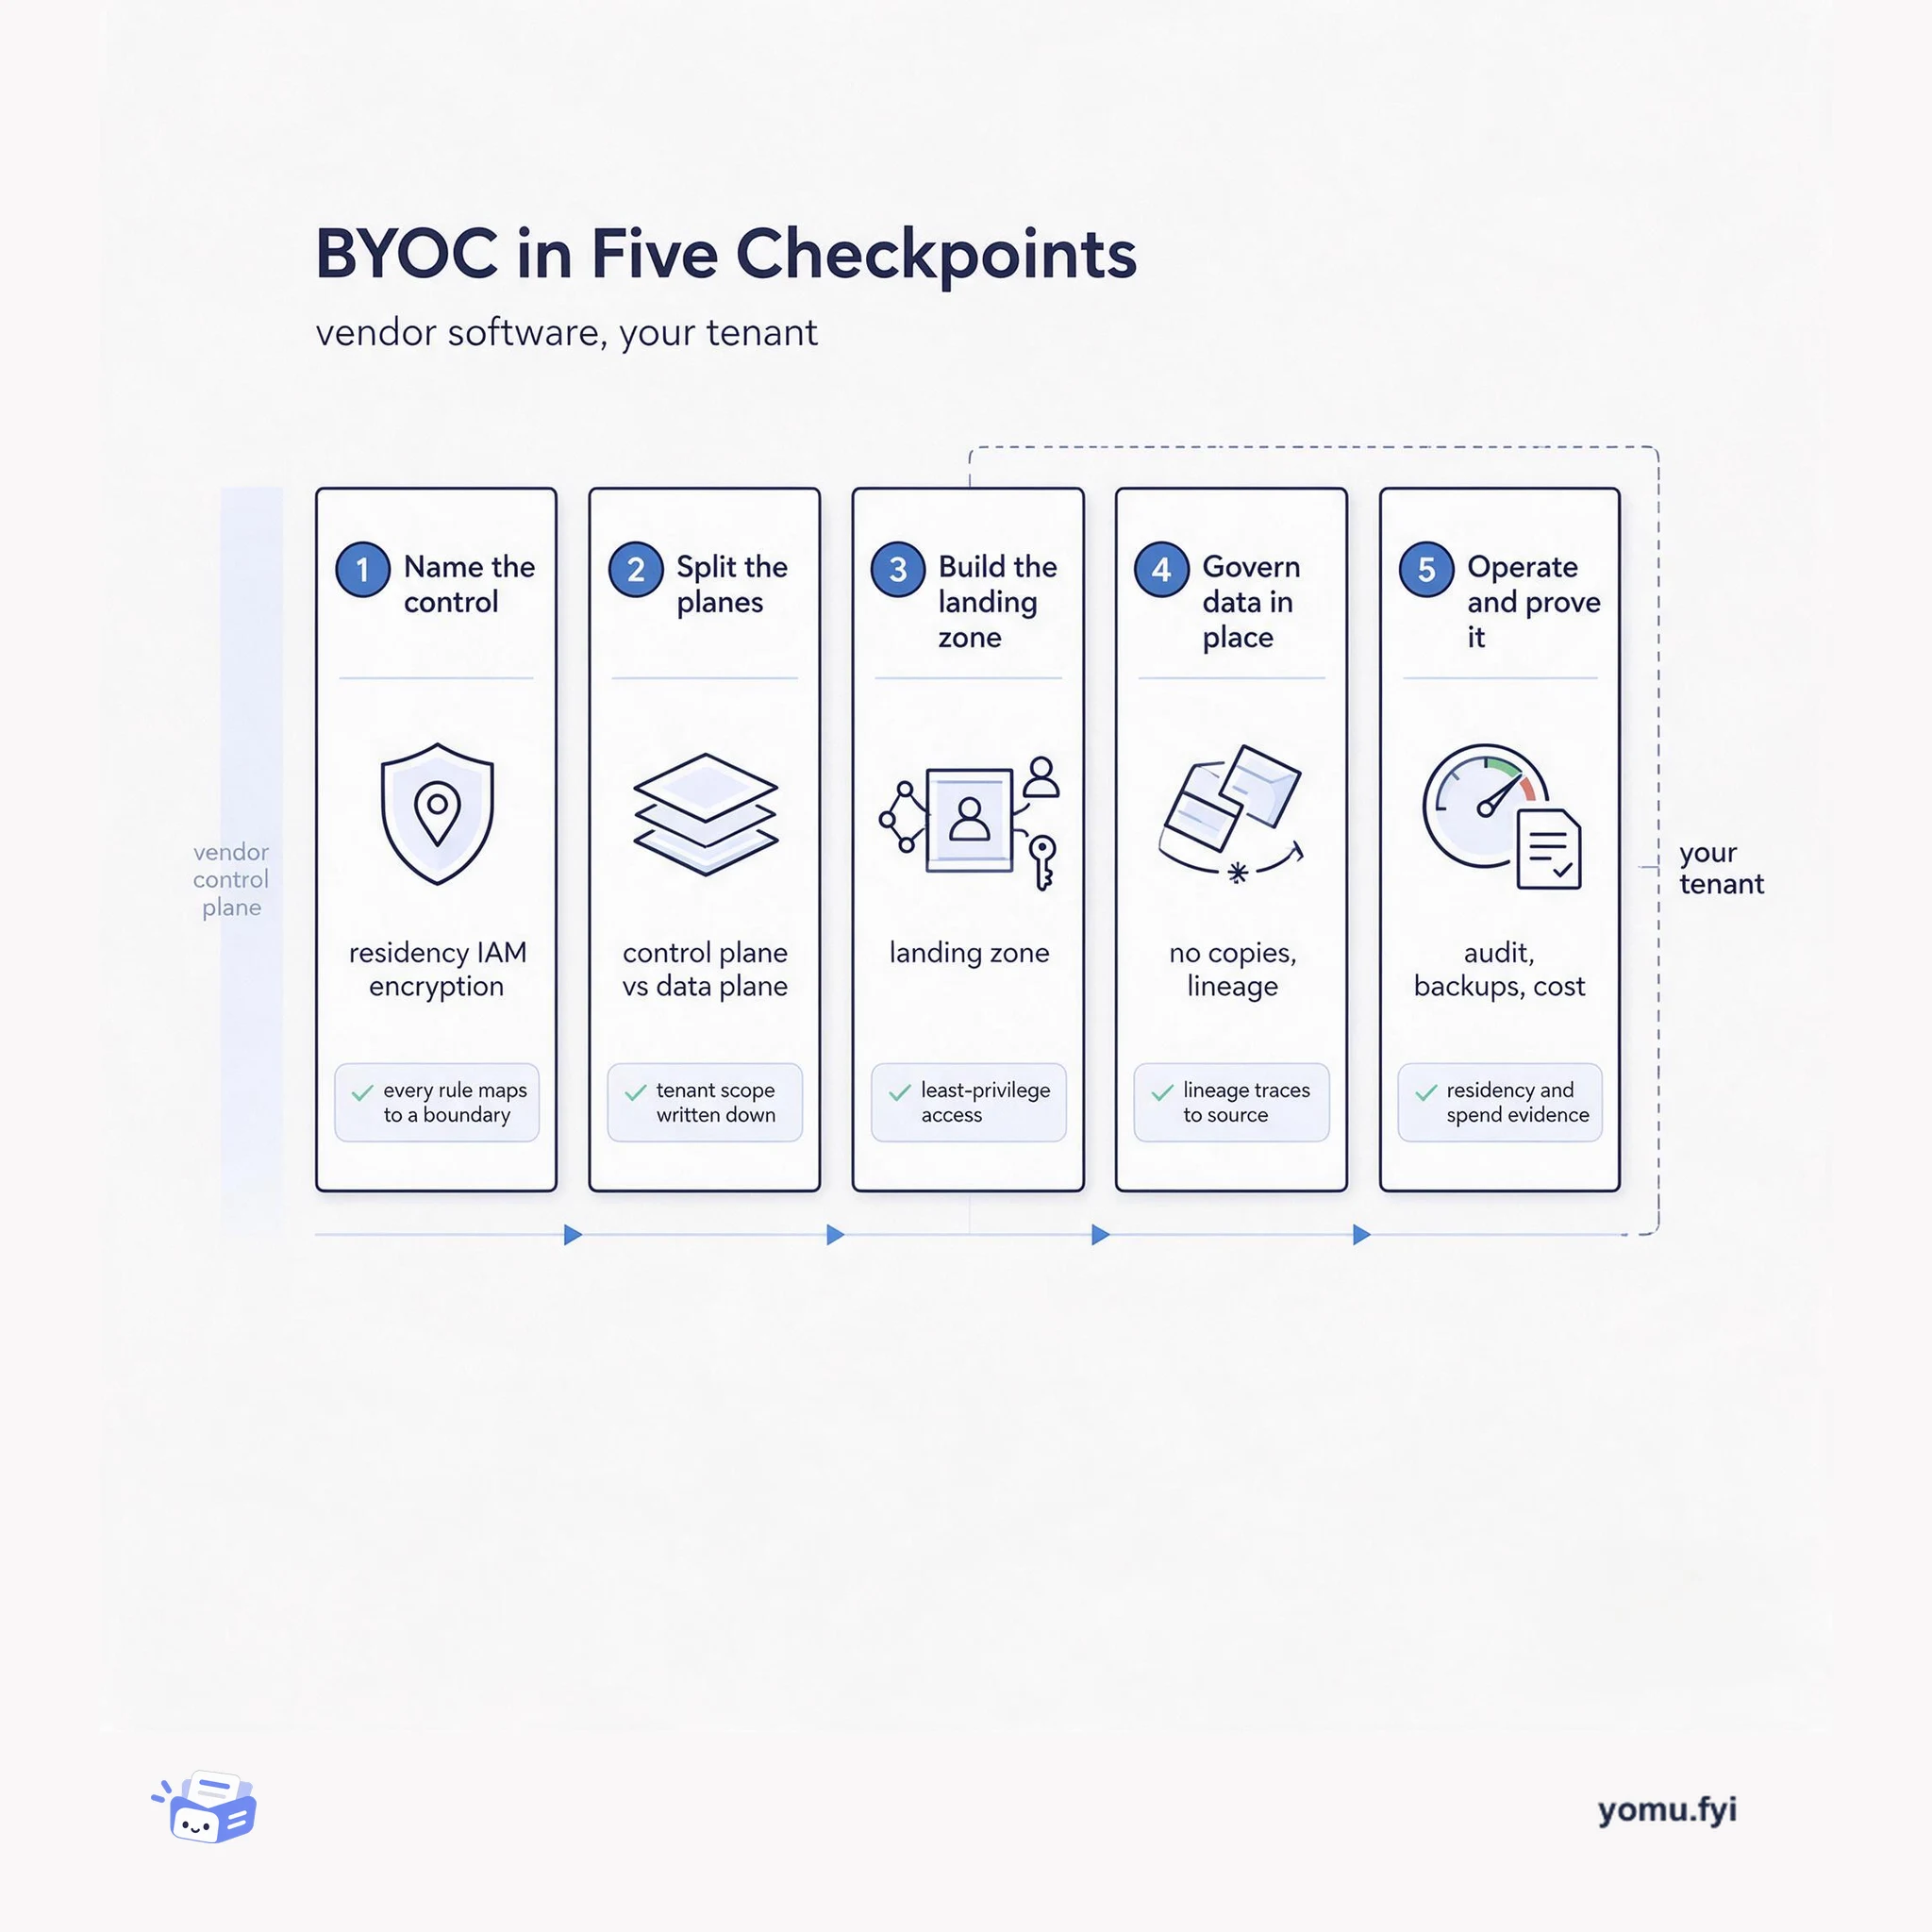
BYOC in Five Checkpoints: Name, Split, Land, Govern, Operate
A five-checkpoint walkthrough of BYOC: name the control you need, split control and data planes, build the landing zone, govern data in place, then operate inside your own tenant.
Loading…
Topic
4 posts about Multi-tenant. Every summary links to the original.
See the idea
A five-checkpoint walkthrough of BYOC: name the control you need, split control and data planes, build the landing zone, govern data in place, then operate inside your own tenant.
The Good Stuff
Paid picks we use ourselves. Links carry a referral code — a subscription through one earns us a commission at no extra cost to you.
Newest first
Local developer workstations introduce three concrete operational risks: production-parity risk from environment drift, slow time-to-first-commit for new engineers, and unmanaged security exposure from misconfigured tools. Red Hat OpenShift Dev Spaces addresses these by moving compute and tooling into containerized workspaces running directly on the cluster, with environments declared as code in a devfile. A production deployment requires four-zone namespace isolation separating control (openshift-devspaces), core server (devspaces-checluster), secure asset (devspaces-openvsx), and sandbox (username-devspaces) zones to prevent operator reconciliation from overriding custom configurations. Resource governance uses a two-tier model with defaultContainerResources fallback limits and containerResourceCaps absolute per-container ceilings, while automated cleanup cron jobs (monthly on the 1st) and inactivity idling (after 4 hours) protect etcd health by removing stopped workspaces after 30 days. The guide concludes with next steps for authentication and private extension registries.
Auth0 Organizations provide an isolated workspace per tenant with dedicated members, identity provider connections, metadata, and role-based access control, addressing enterprise requirements like Acme Corp’s SSO ultimatum. Login flows differentiate between B2C users (no organization parameter) and B2B users (organization parameter scopes connections, branding, and token claims including org_id). Home Realm Discovery automatically matches users to their enterprise IdP by email domain when an organization is set, requiring the Identifier First authentication profile and eliminating password prompts. Authorization is per-organization via org_id claims in access tokens, with organization-level roles and permissions resolved through RBAC. The post also covers invitation tickets, tenant context switching where users obtain new tokens with a different org_id, recommends one Auth0 Organization per app tenant, describes Auth0 Actions for custom metadata, and introduces this as part one of a five-part series on B2B identity.
Salesforce’s Cloud Atlas team operates a globally distributed identity data store that must maintain five nines of availability, roughly five minutes of downtime per year. The team redesigned service protection after per-instance rate limiting proved insufficient under autoscaling and increasingly bursty, unpredictable agent-driven traffic. The new approach combines intelligent load shedding, which monitors queue time as an early indicator of system pressure before error rates spike, with coordinator-free global quota management. Servers independently measure and share customer usage to throttle noisy tenants without a centralized coordinator, preventing one customer’s surge from affecting others. This design prevents cascading failures by shedding lower-priority work before overload spreads across dependent services, ensuring graceful degradation rather than widespread outage.
Security researcher Oren Yomtov reported a vulnerability in Cloudflare Containers and Sandboxes through the bug bounty program, demonstrating that a Workers Paid account could recover residual disk blocks from previous containers on the same host. The issue arose from Linux device mapper thin provisioning with skip_block_zeroing enabled, which left unzeroed 64 KiB blocks when a 4 KiB write triggered allocation, allowing the remaining 60 KiB to retain prior data. Researchers recovered directory structures, database pages, and structurally complete SQLite databases from 18 of 24 placements across four continents, using ext4 checksums to distinguish foreign blocks. Cloudflare removed skip_block_zeroing, retired all running container disks, and cleared cached image snapshots created before the mitigation, completing cleanup by September 19. Retained disk-I/O telemetry showed no evidence of malicious exploitation, and the researchers confirmed secure deletion of recovered data.
The best engineering reads, once a week.




