Axum at the Trust Boundary: From Request to Protected Response
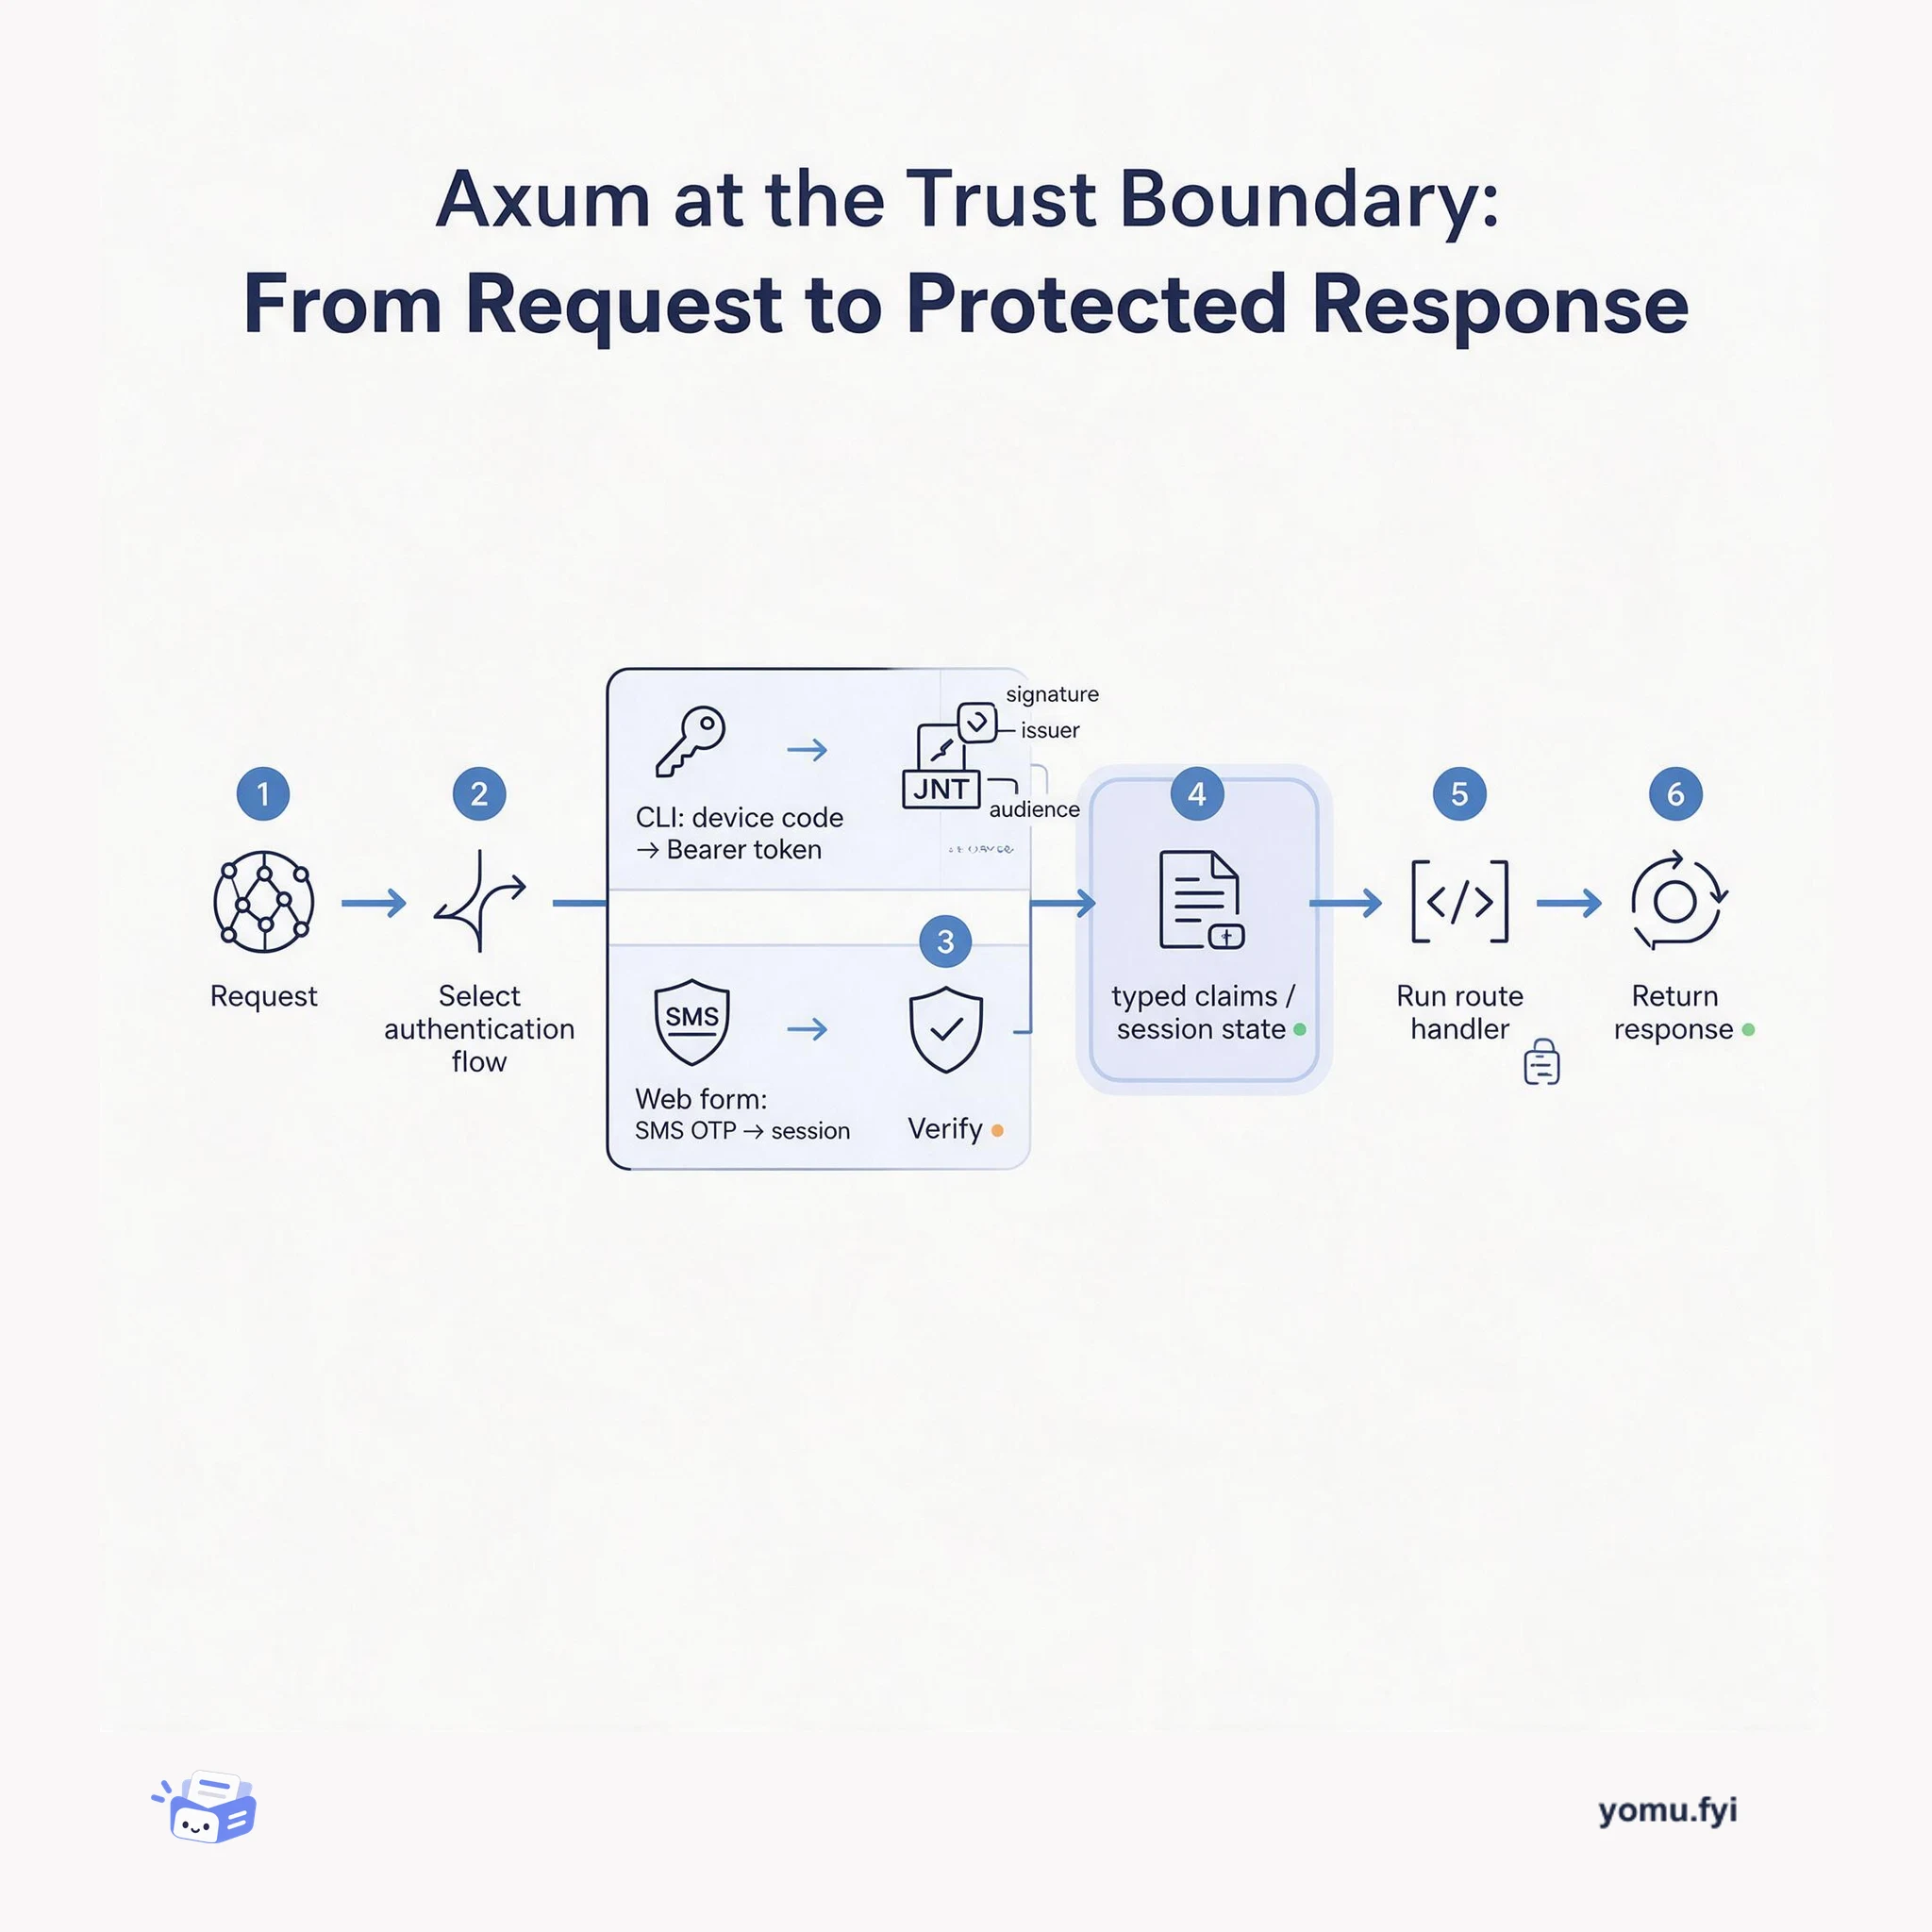
Axum is a Rust web framework for composing routes, middleware, and extractors. This explainer shows how different login flows become verified identity before a handler responds.
 Auth0Aniket BhattacharyeaTutorial
CLI applications cannot use a standard browser redirect OAuth login flow when no browser or redirect URL is available, so the tutorial uses OAuth 2.0 Device Authorization Flow. It builds an end-to-end Rust workspace containing a CLI, a shared auth-lib crate, and an Axum API configured with Auth0. The CLI requests a device code, displays a verification URL and user code, polls for an ID token and access token, then sends the access token as a Bearer credential. The API middleware fetches JWKS, selects the key matching the JWT’s kid, validates RS256 signatures plus issuer and audience claims, and deserializes strongly typed UserClaims. With valid claims, a protected route returns a message and subject; otherwise the extractor returns an unauthorized response.
CLI applications need an authentication method for cases where launching a browser or receiving a redirect URL is inconvenient or impossible. The tutorial applies the OAuth 2.0 Device Authorization Flow to this browserless authentication problem.
The implementation configures an Auth0 Native Application and API, enables the Device Code grant, and creates Rust CLI and Axum API projects sharing typed authentication models and JWT validation logic. The CLI obtains tokens through device authorization, while an Axum request extractor validates Bearer tokens before protected handlers run.
Auth0’s Device Authorization grant must be enabled for the Native Application; otherwise token polling fails with an unauthorized_client error.
The shared auth-lib crate defines typed OAuth responses, JWT claims, and JWKS structures, allowing deserialization errors instead of unchecked JSON field assumptions.
The Axum AuthUser extractor rejects missing or malformed Bearer credentials and invalid tokens with HTTP 401 responses before the protected route executes.
Summaries are generated from the original by a language model. Check the original before relying on it.
See the idea
Axum is a Rust web framework for composing routes, middleware, and extractors. This explainer shows how different login flows become verified identity before a handler responds.
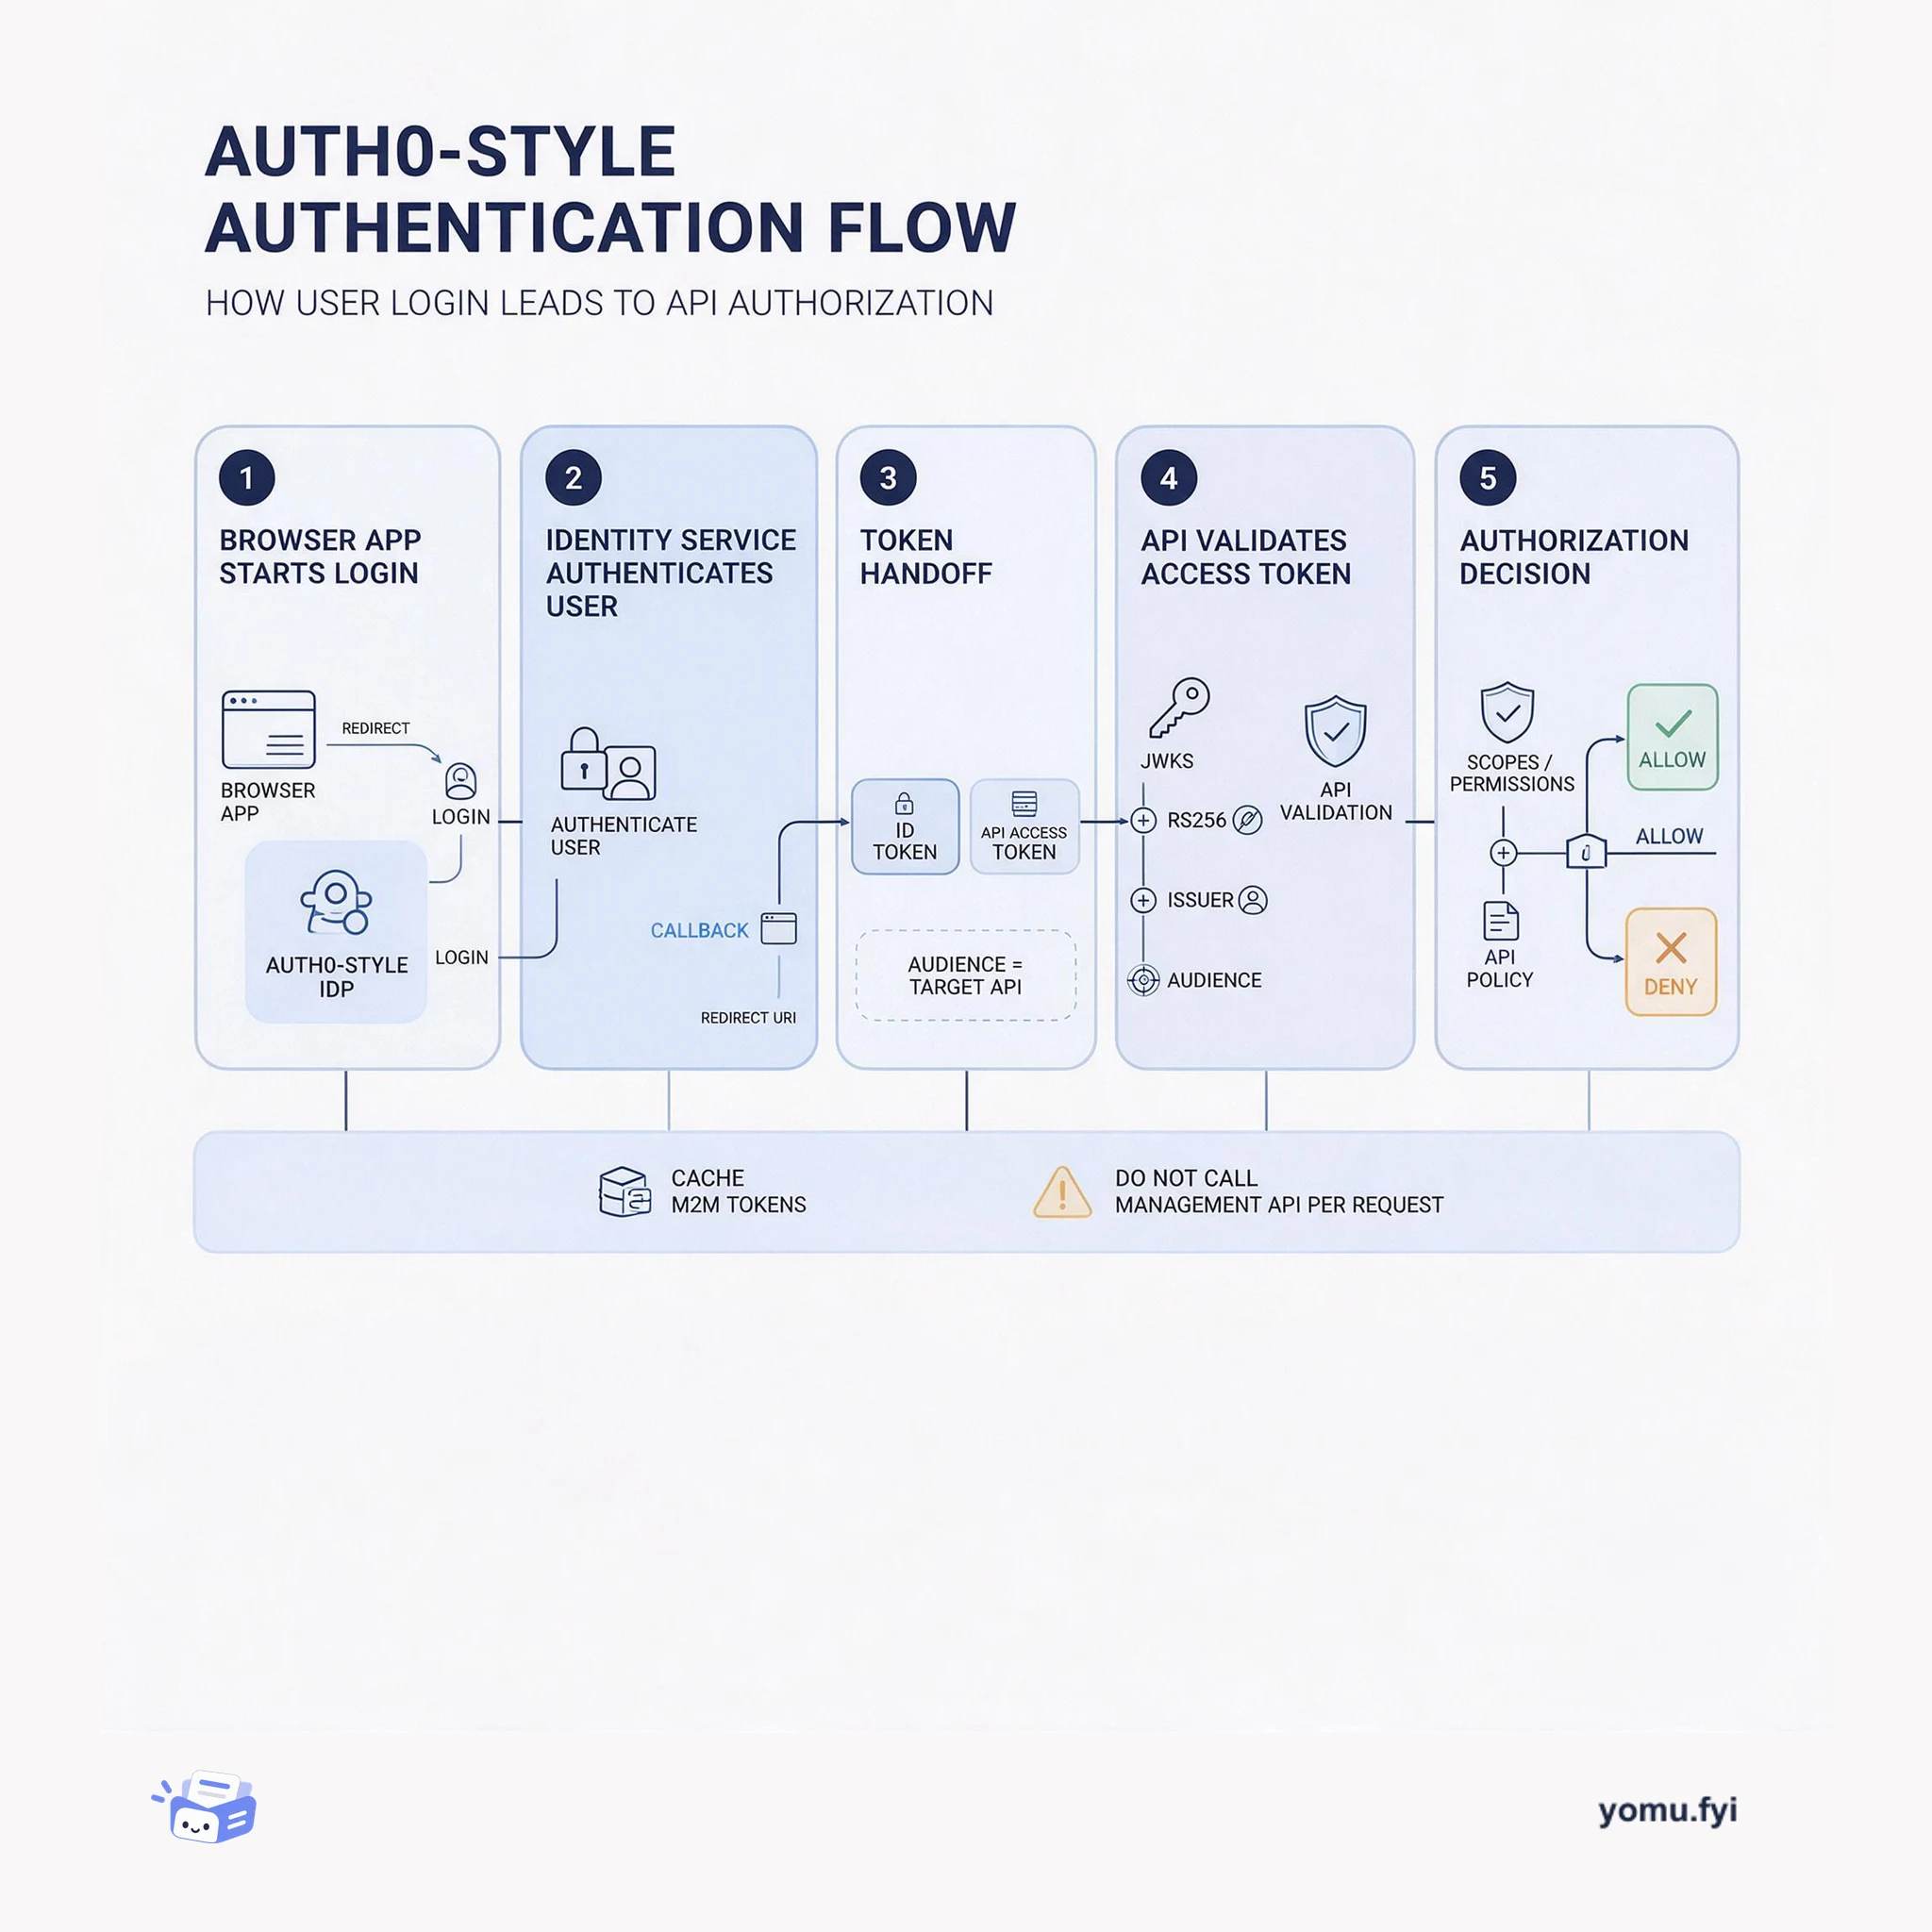
See how an Auth0 login becomes an API decision: redirect the user, issue the right token, validate its claims, and apply audience, scope, and access policies.
Keep reading
The Good Stuff
Paid picks we use ourselves. Links carry a referral code — a subscription through one earns us a commission at no extra cost to you.
One useful email. Unsubscribe anytime.