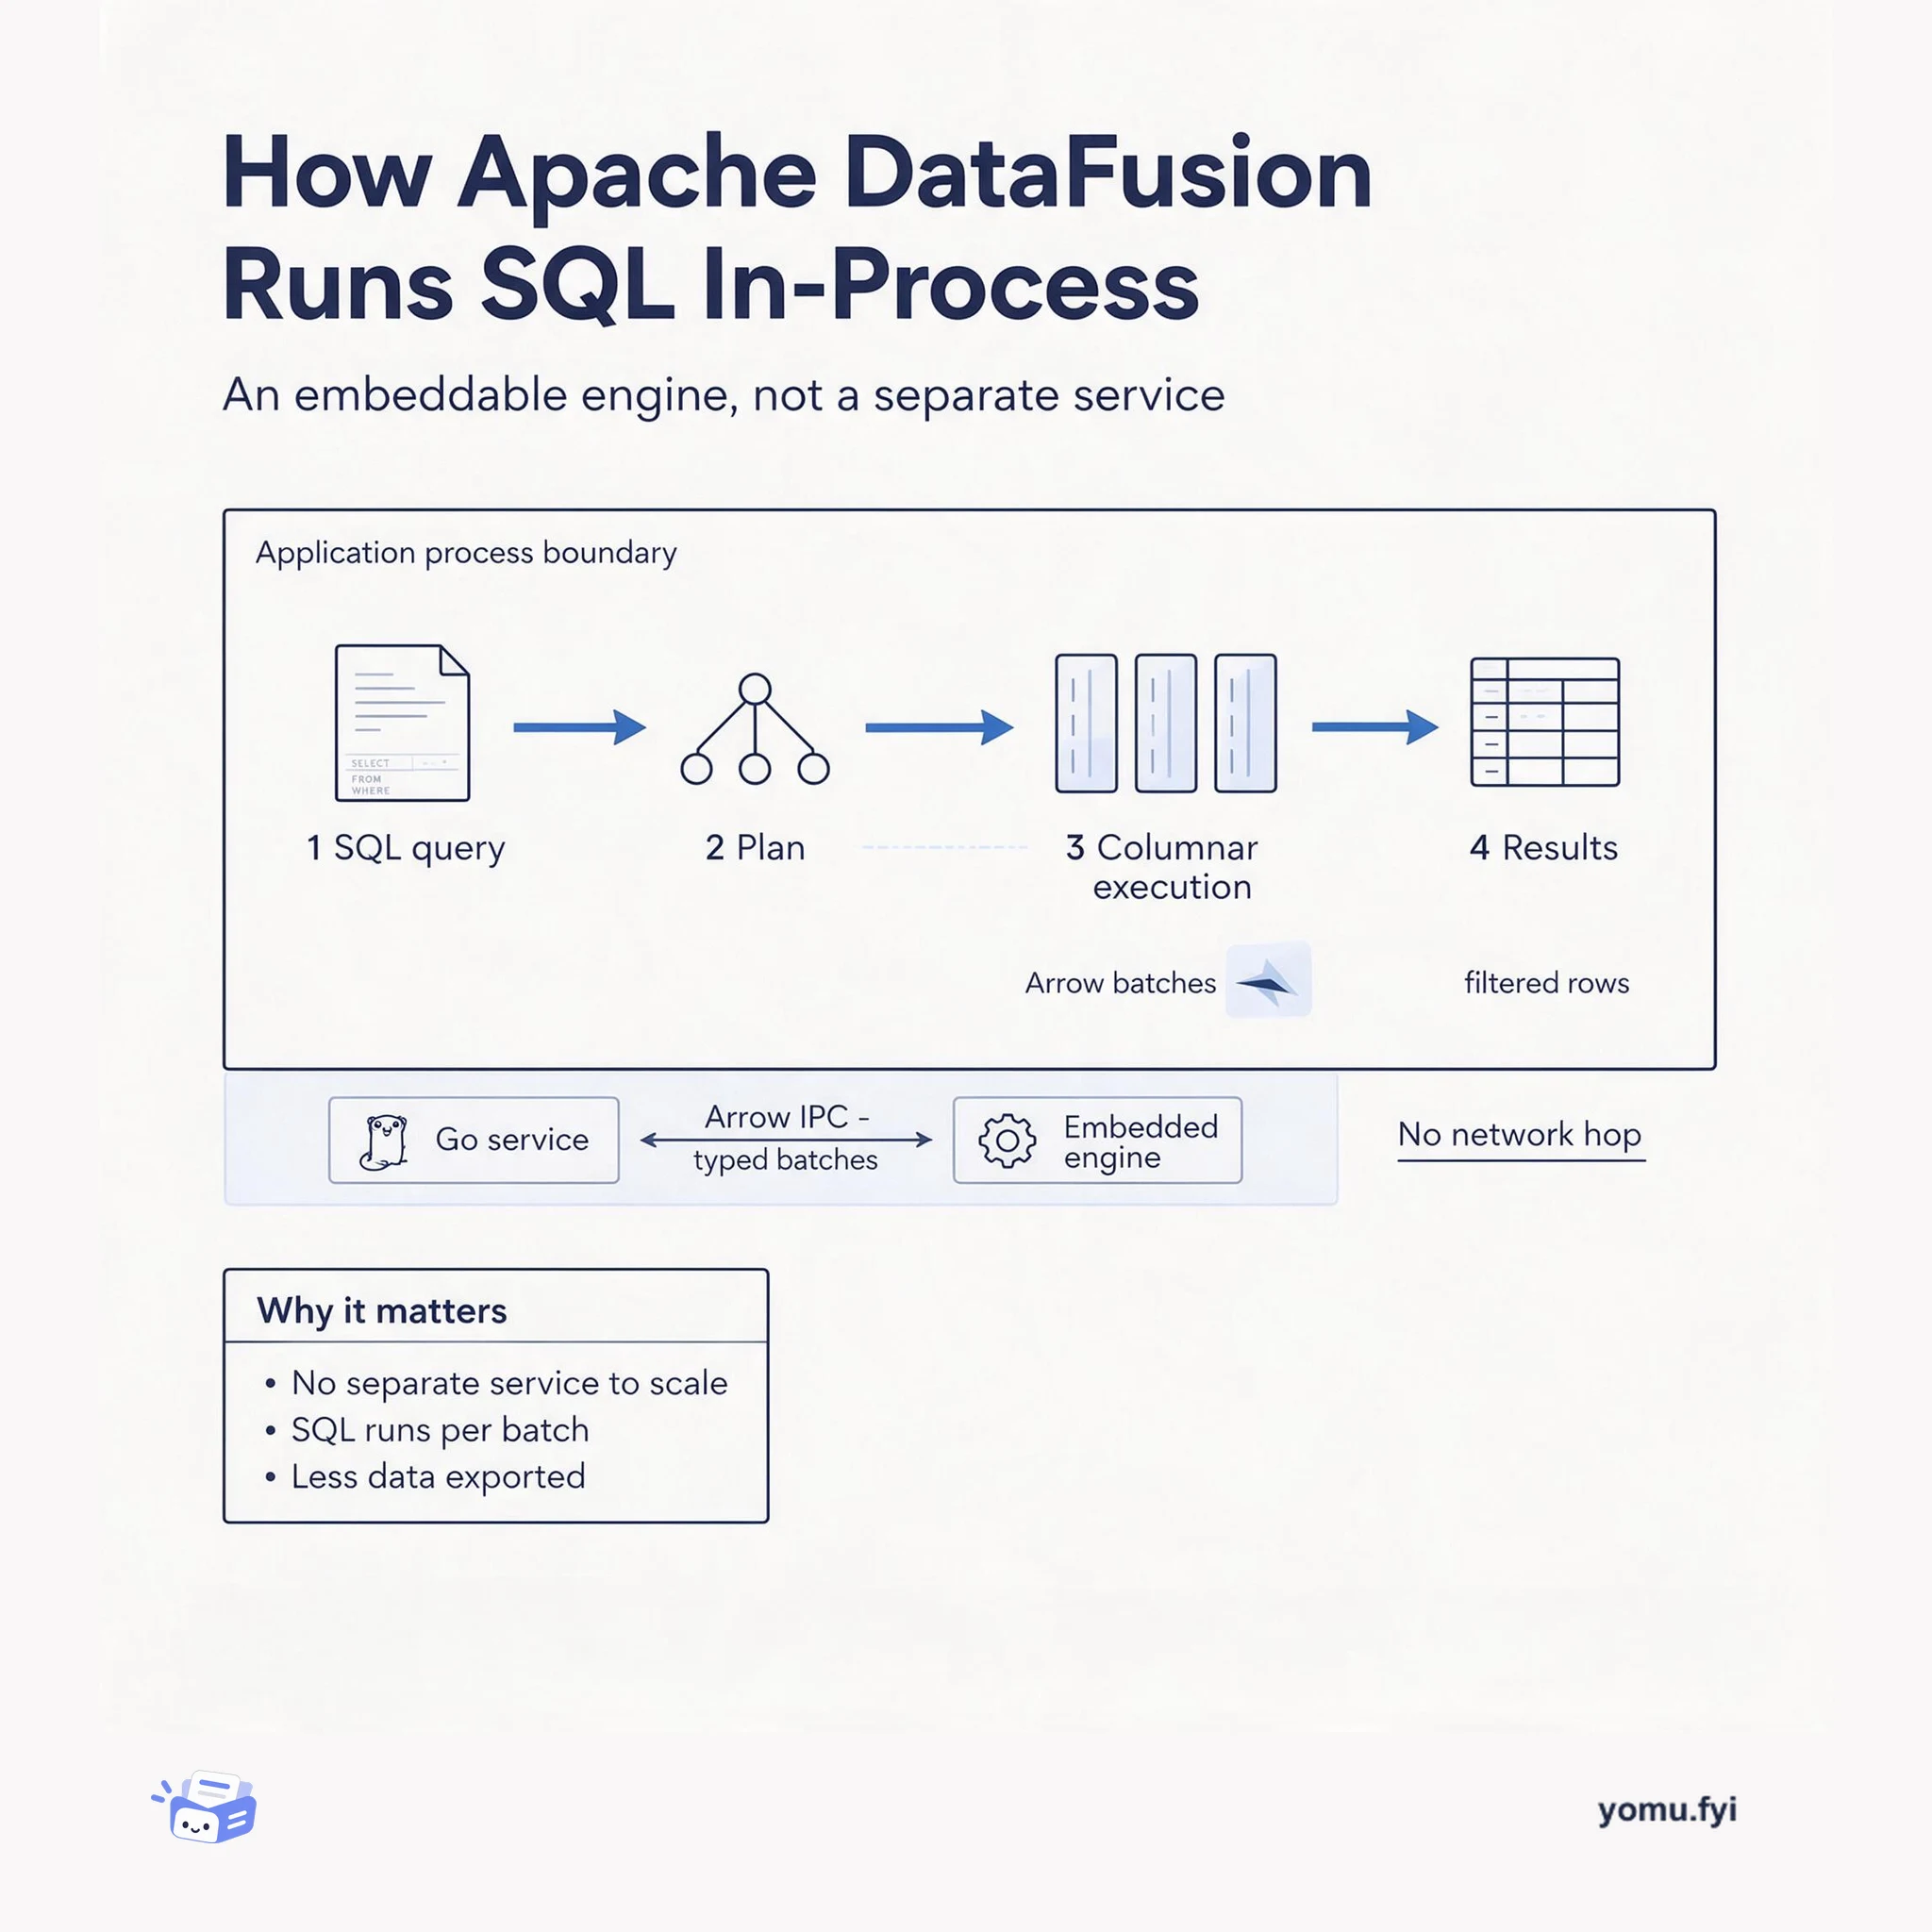
How Apache DataFusion Runs SQL In-Process
Apache DataFusion is an embeddable query engine: SQL goes in, runs as columnar Arrow batches inside your own process, and results come out without a separate service.
Axum is a Rust web framework for composing routes, middleware, and extractors. This explainer shows how different login flows become verified identity before a handler responds.
Axum services can place authentication between an incoming request and the route logic that acts on it. A CLI may obtain an Auth0 device-flow token, while a web form may verify a one-time SMS code and maintain a session; both paths lead to a request carrying accepted identity or verification state. The diagram follows the request through routing, verification, typed claims or session state, handler execution, and the final response. It highlights where external identity services and application code meet, helping engineers choose a flow without mixing credential acquisition with business logic.
The Auth0 example places verification in API middleware before the protected route runs. The middleware fetches JWKS, selects the key matching the JWT kid, validates the RS256 signature, issuer, and audience, then exposes strongly typed user claims to the route.
A CLI without a browser or redirect URL can use OAuth 2.0 Device Authorization Flow: it displays a verification URL and code, polls for tokens, and sends a Bearer credential. A web form can use Twilio Verify to send and validate a one-time SMS code, with session state used to represent the result.
Credential acquisition and verification should be treated as an earlier boundary, so the handler receives accepted claims or session state rather than implementing the full login exchange. The examples also show external services handling identity or OTP work while the Rust application owns routes and responses.
The posts behind it
 Twilio · · Tutorial
Voice agents can converse, but they need external APIs to retrieve live information or take actions such as checking inventory or booking appointments. This tutorial builds a Node.js voice agent with Twilio Conversation Relay, Express, WebSockets, and the OpenAI Node.js SDK. A Conversation Relay WebSocket handler collects voice prompts, maintains conversation messages, streams model output back to the call, and defines a get_cat_fact tool that fetches JSON from the unauthenticated Cat Facts REST API. The service returns the fetched fact or an error message, while TwiML connects Twilio's voice-capable number to the WebSocket endpoint. Testing uses Node.js 18+, an OpenAI API key, ngrok, and a POST /voice webhook; the stated result is that callers can ask for a cat fact and hear the API response.
Twilio · · TutorialVoice agents can converse, but need external APIs to retrieve live data or take actions such as checking inventory and booking appointments. This tutorial builds a Python and FastAPI voice agent with Twilio Conversation Relay, OpenAI tool calling, and an unauthenticated Cat Facts REST API. A FastAPI webhook returns TwiML that connects callers to a websocket, while Conversation Relay messages are converted into conversation history and streamed responses. When the model requests a cat fact, the application executes the tool, sends its result back to OpenAI, and streams the follow-up answer to the caller. The setup uses environment variables for the OpenAI key, httpx for asynchronous external requests, and ngrok to expose local webhooks; the completed test lets a caller ask for and receive a cat fact.
 Auth0 · · Tutorial
CLI applications cannot use a standard browser redirect OAuth login flow when no browser or redirect URL is available, so the tutorial uses OAuth 2.0 Device Authorization Flow. It builds an end-to-end Rust workspace containing a CLI, a shared auth-lib crate, and an Axum API configured with Auth0. The CLI requests a device code, displays a verification URL and user code, polls for an ID token and access token, then sends the access token as a Bearer credential. The API middleware fetches JWKS, selects the key matching the JWT’s kid, validates RS256 signatures plus issuer and audience claims, and deserializes strongly typed UserClaims. With valid claims, a protected route returns a message and subject; otherwise the extractor returns an unauthorized response.
Twilio · · TutorialPasswordless authentication replaces passwords with one-time codes delivered by SMS, and this tutorial builds a Rust app around that flow. The app uses Twilio Verify for OTP generation and validation, with GET and POST routes at "/" for collecting a phone number and at "/verify" for entering the received code. It sets up a Cargo project with Axum, Handlebars templates, sessions, dotenvy configuration, and the rustlio Twilio client, while environment variables hold the Account SID, Auth Token, and Verify Service SID. The implementation also serves HTML forms and static assets, with verification status rendered as a success or error message. Running cargo run starts the server on port 8080, where users can submit a number, receive an SMS, and see whether the verification code is valid.
More like this
Apache DataFusion is an embeddable query engine: SQL goes in, runs as columnar Arrow batches inside your own process, and results come out without a separate service.
A model deployed on AKS is open by default. See how MaaS policies insert Authorino authentication and Limitador rate limits in front of vLLM, so bad keys and over-quota requests stop at the gate.
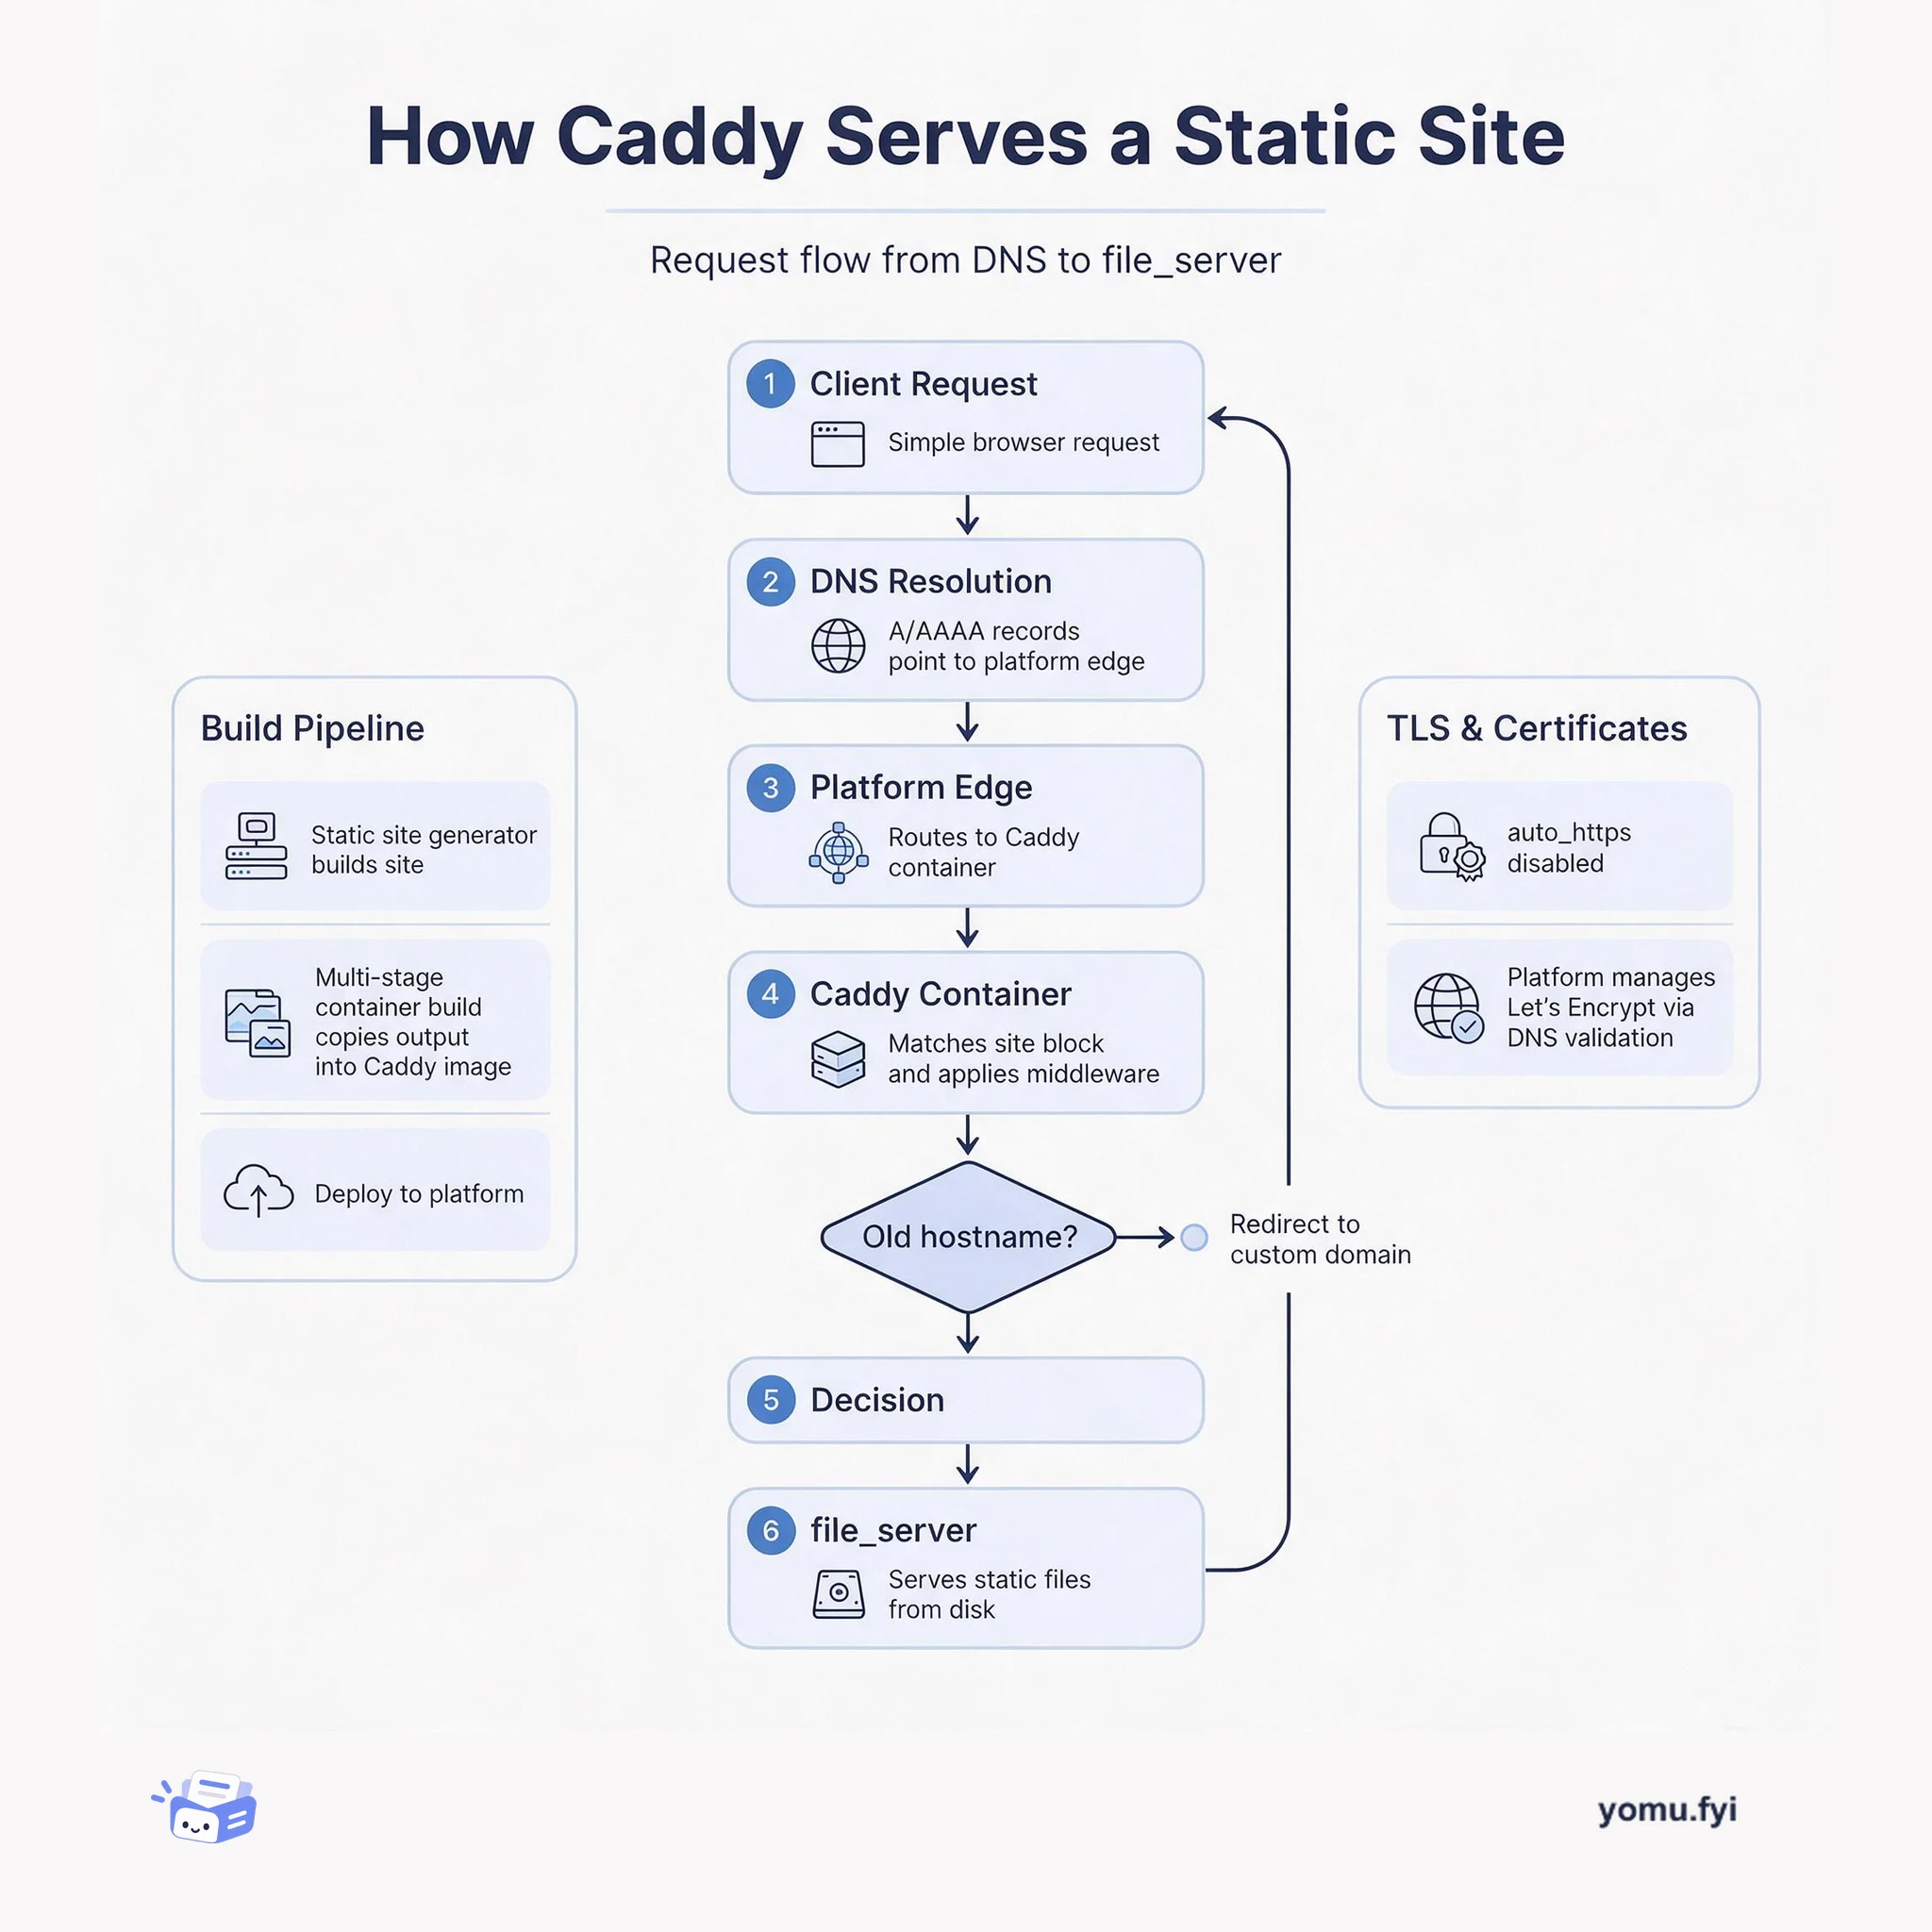
See how Caddy handles a request for a static site, from DNS resolution through container routing to file_server, and how TLS and redirects fit into the flow.
The Good Stuff
Paid picks we use ourselves. Links carry a referral code — a subscription through one earns us a commission at no extra cost to you.
One useful email. Unsubscribe anytime.