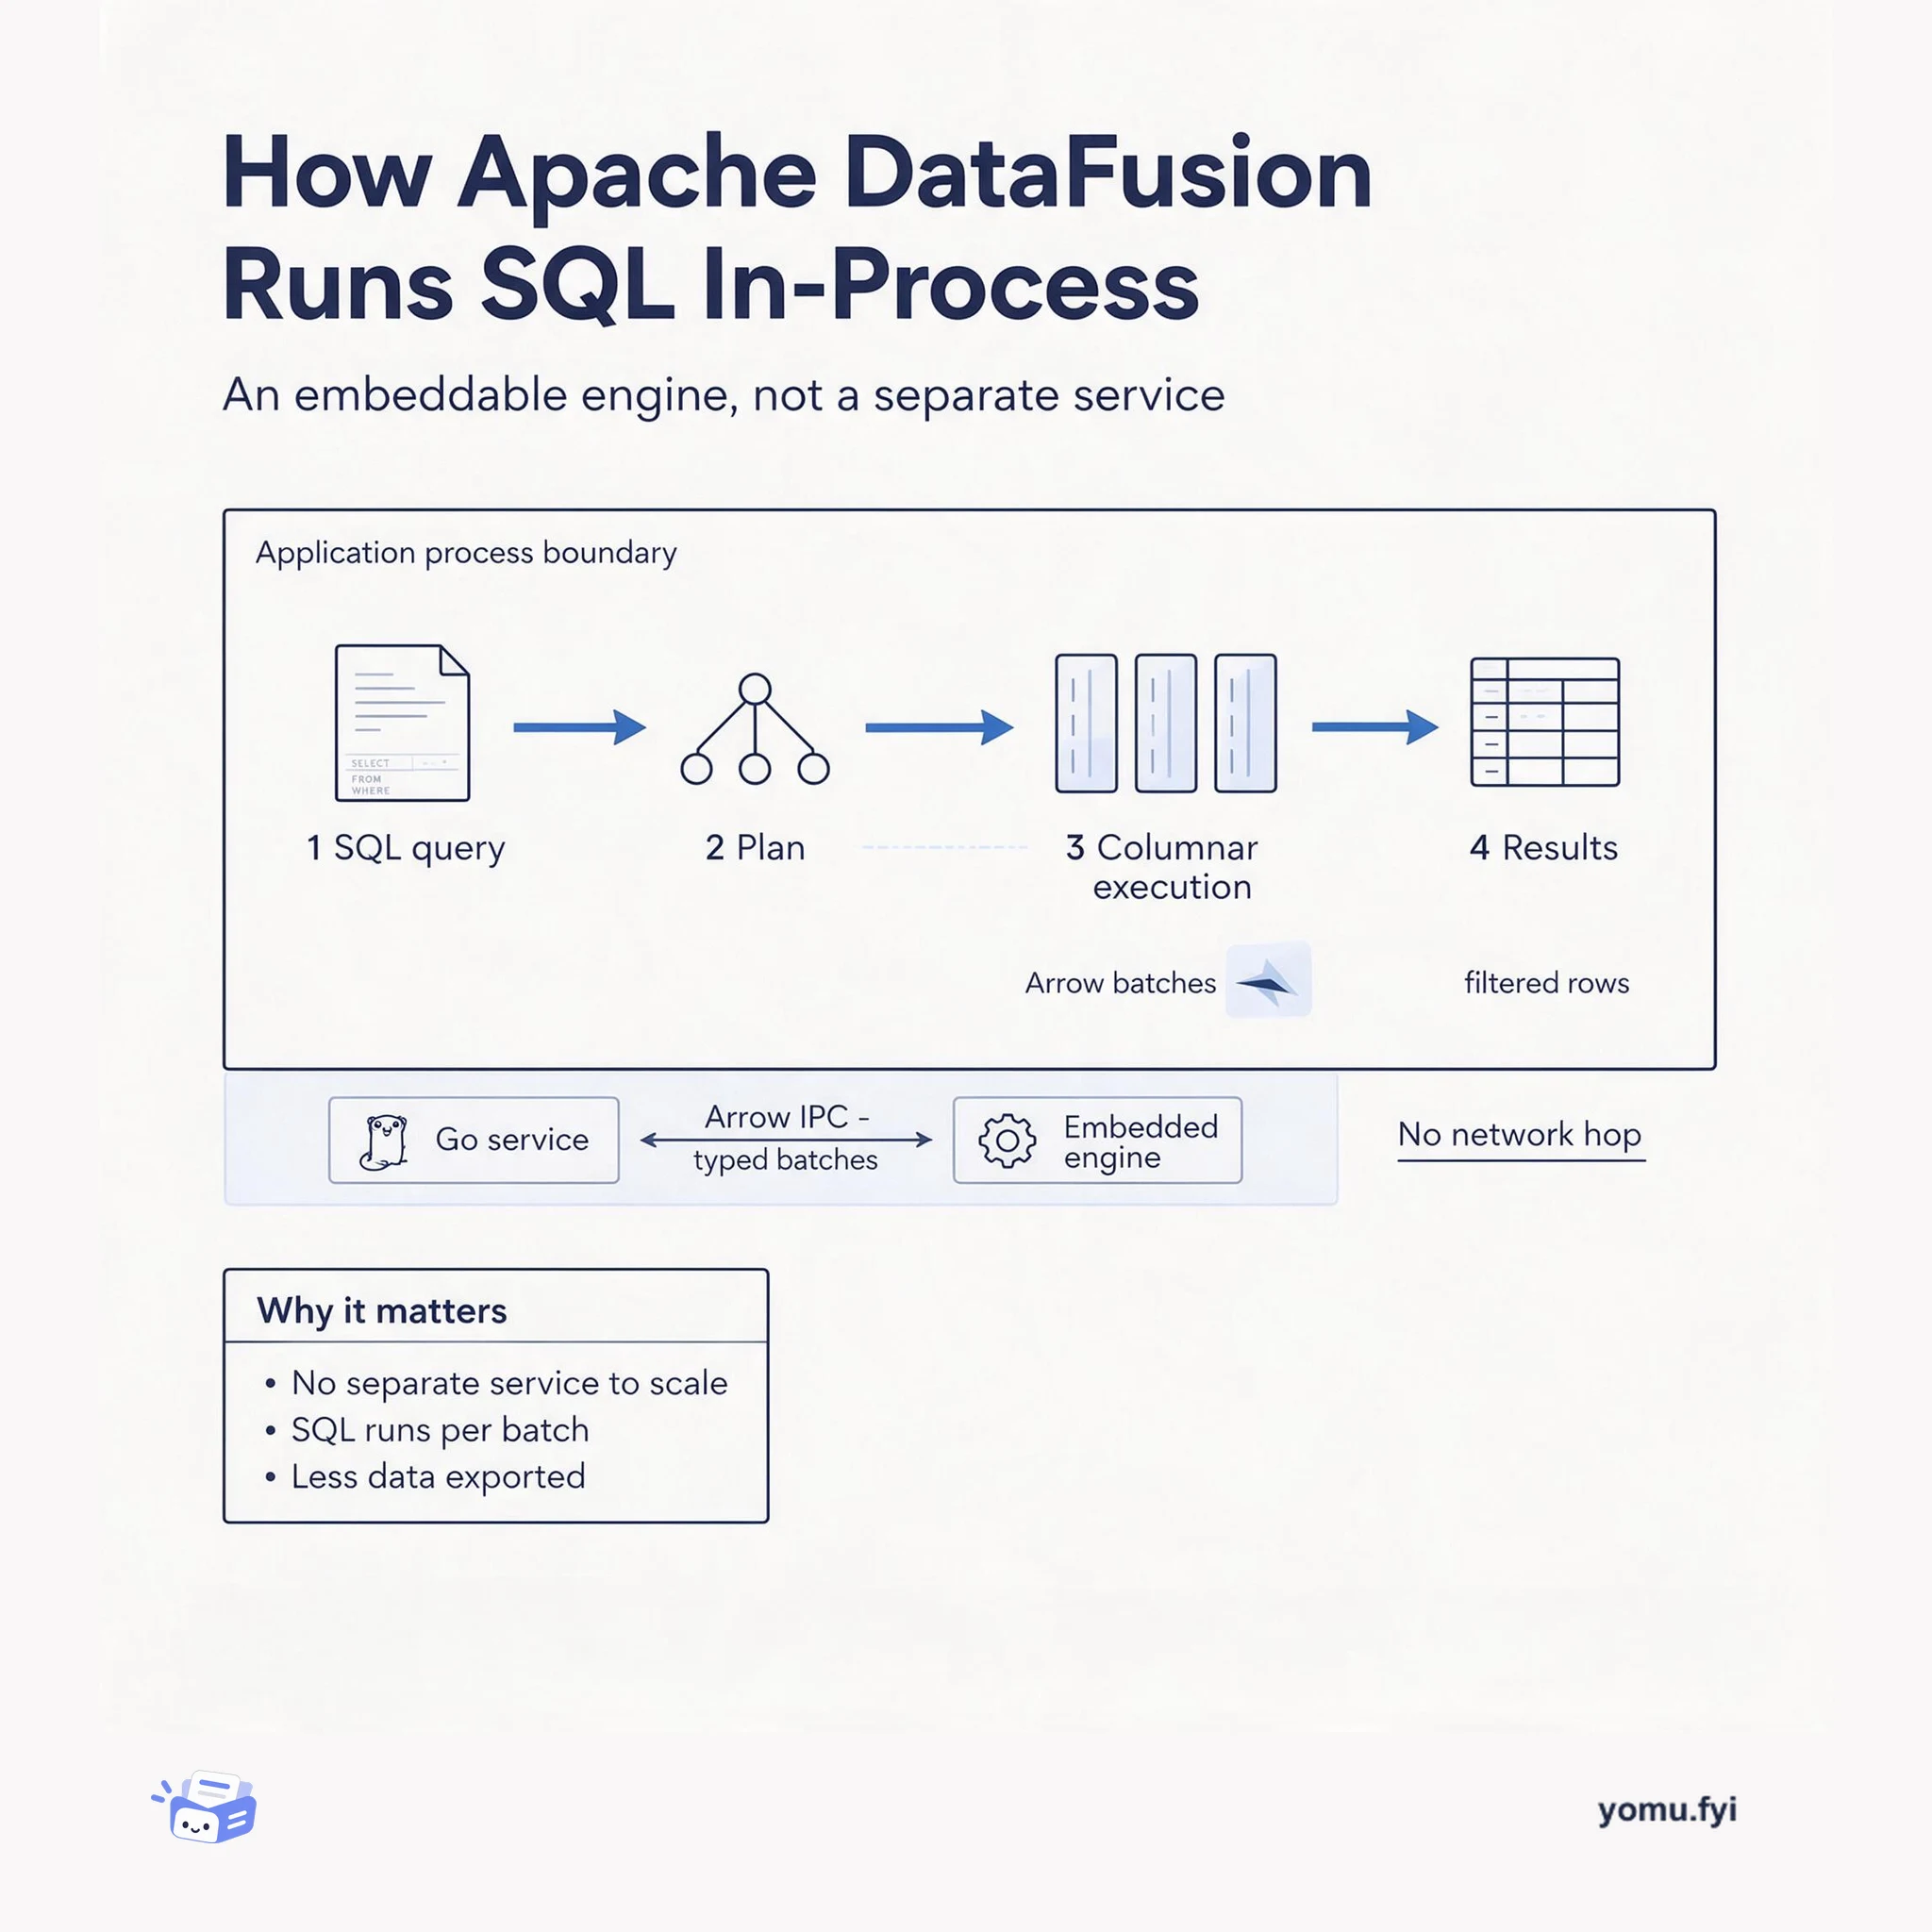
How Apache DataFusion Runs SQL In-Process
Apache DataFusion is an embeddable query engine: SQL goes in, runs as columnar Arrow batches inside your own process, and results come out without a separate service.
See how an Auth0 login becomes an API decision: redirect the user, issue the right token, validate its claims, and apply audience, scope, and access policies.
This explainer follows a browser application from login redirect through callback, token selection, API validation, and authorization. It separates identity tokens from API access tokens, shows how issuer, audience, signature, scopes, and permissions affect the request, and highlights where Auth0 API policies and client grants fit. The flow also flags practical operating choices: cache machine-to-machine tokens and avoid using the Management API on every request.
The audience identifies which API the token is meant for and determines which Auth0 API access policy is evaluated. Without the intended audience, the request may produce the wrong token or lack the API permissions the service expects.
The API can fetch the signing keys through JWKS and validate the JWT signature, issuer, and audience; the Rust and Axum example uses RS256 and selects the key matching the token’s kid. After validation, the service can deserialize claims and apply its route authorization rules.
Obtaining a new M2M token for every request can exhaust Auth0 rate limits. The supplied guidance says to cache tokens, refresh them with a 60-second expiry buffer, and use a server-side cache when data must remain fresher than token claims.
The posts behind it
 Auth0 · · Tutorial
The tutorial shows how to add Google login to a Vite-based React single-page app without implementing OAuth directly, using Auth0’s React SDK and Google social connection. It covers installing @auth0/auth0-react, creating an Auth0 Single Page Web Application, checking RS256 and OIDC Conformant settings, registering callback, logout, and web-origin URLs, and supplying the domain and client ID through Vite environment variables. The React code wraps the app in Auth0Provider, uses useAuth0 for loading and authentication state, and calls loginWithRedirect with connection: 'google-oauth2' to bypass provider selection. For production, it explains replacing Auth0’s shared development keys with Google Cloud credentials whose origin and redirect URI target the Auth0 domain, then storing them in the Auth0 social connection. It also points to route protection with withAuthenticationRequired, API access tokens from getAccessTokenSilently, and exact redirect-URI matching as important follow-on considerations.
Auth0 · · TutorialAuth0 API Access Policies for Applications control whether an application can obtain an access token for a registered API, separately for user-delegated and client access. The FinFlow example separates a browser application that should reach both APIs from a machine-to-machine Risk Engine restricted to the Payments API. Policies provide three choices—allow_all, require_client_grant, and deny_all—while client grants specify an application's audience and permitted scopes, with the audience determining which API policy is evaluated. The guide shows Dashboard and Management API configuration, including subject_type_authorization settings and grants for user and client access. It also explains that third-party applications still require grants under allow_all, while default third-party grants establish a baseline and per-application grants take precedence for exceptions.
Auth0 · · Problem & solutionAuth0 429 responses in production are tied to rate limits, commonly when applications call the Management API for every request or obtain a new machine-to-machine (M2M) token for every request. Because limits are per tenant and vary by plan, logging x-ratelimit-limit, x-ratelimit-remaining, and x-ratelimit-reset headers exposes approaching exhaustion. User roles, permissions, and metadata that can be treated as access-token snapshots should be added as custom claims by a Post-Login Action, while APIs read them from the JWT. M2M tokens, valid for 24 hours by default, should be cached and refreshed with a 60-second expiry buffer; data requiring freshness should sit behind a server-side cache with a 30-to-60-second TTL. When a 429 occurs, retry at the Unix timestamp in x-ratelimit-reset rather than applying exponential backoff, because the reset time is deterministic.
Auth0 · · ExplainerAuth0 access tokens can lack a permissions claim despite apparently configured RBAC, and the post identifies five silent causes. The authorization request may omit the API audience, the API’s “Add Permissions in the Access Token” setting may be disabled, or a permission-bearing role may not be assigned to the user, including at the relevant organization level. Developers may also be decoding an ID token rather than the API access token, whose aud identifies the API. Client Credentials tokens represent applications rather than users and typically carry granted scopes instead of a permissions array. For custom Post-Login claims, the post advises using a namespaced claim rather than colliding with Auth0’s reserved permissions claim.
Auth0 · · TutorialCLI applications cannot use a standard browser redirect OAuth login flow when no browser or redirect URL is available, so the tutorial uses OAuth 2.0 Device Authorization Flow. It builds an end-to-end Rust workspace containing a CLI, a shared auth-lib crate, and an Axum API configured with Auth0. The CLI requests a device code, displays a verification URL and user code, polls for an ID token and access token, then sends the access token as a Bearer credential. The API middleware fetches JWKS, selects the key matching the JWT’s kid, validates RS256 signatures plus issuer and audience claims, and deserializes strongly typed UserClaims. With valid claims, a protected route returns a message and subject; otherwise the extractor returns an unauthorized response.
More like this
Apache DataFusion is an embeddable query engine: SQL goes in, runs as columnar Arrow batches inside your own process, and results come out without a separate service.
A model deployed on AKS is open by default. See how MaaS policies insert Authorino authentication and Limitador rate limits in front of vLLM, so bad keys and over-quota requests stop at the gate.
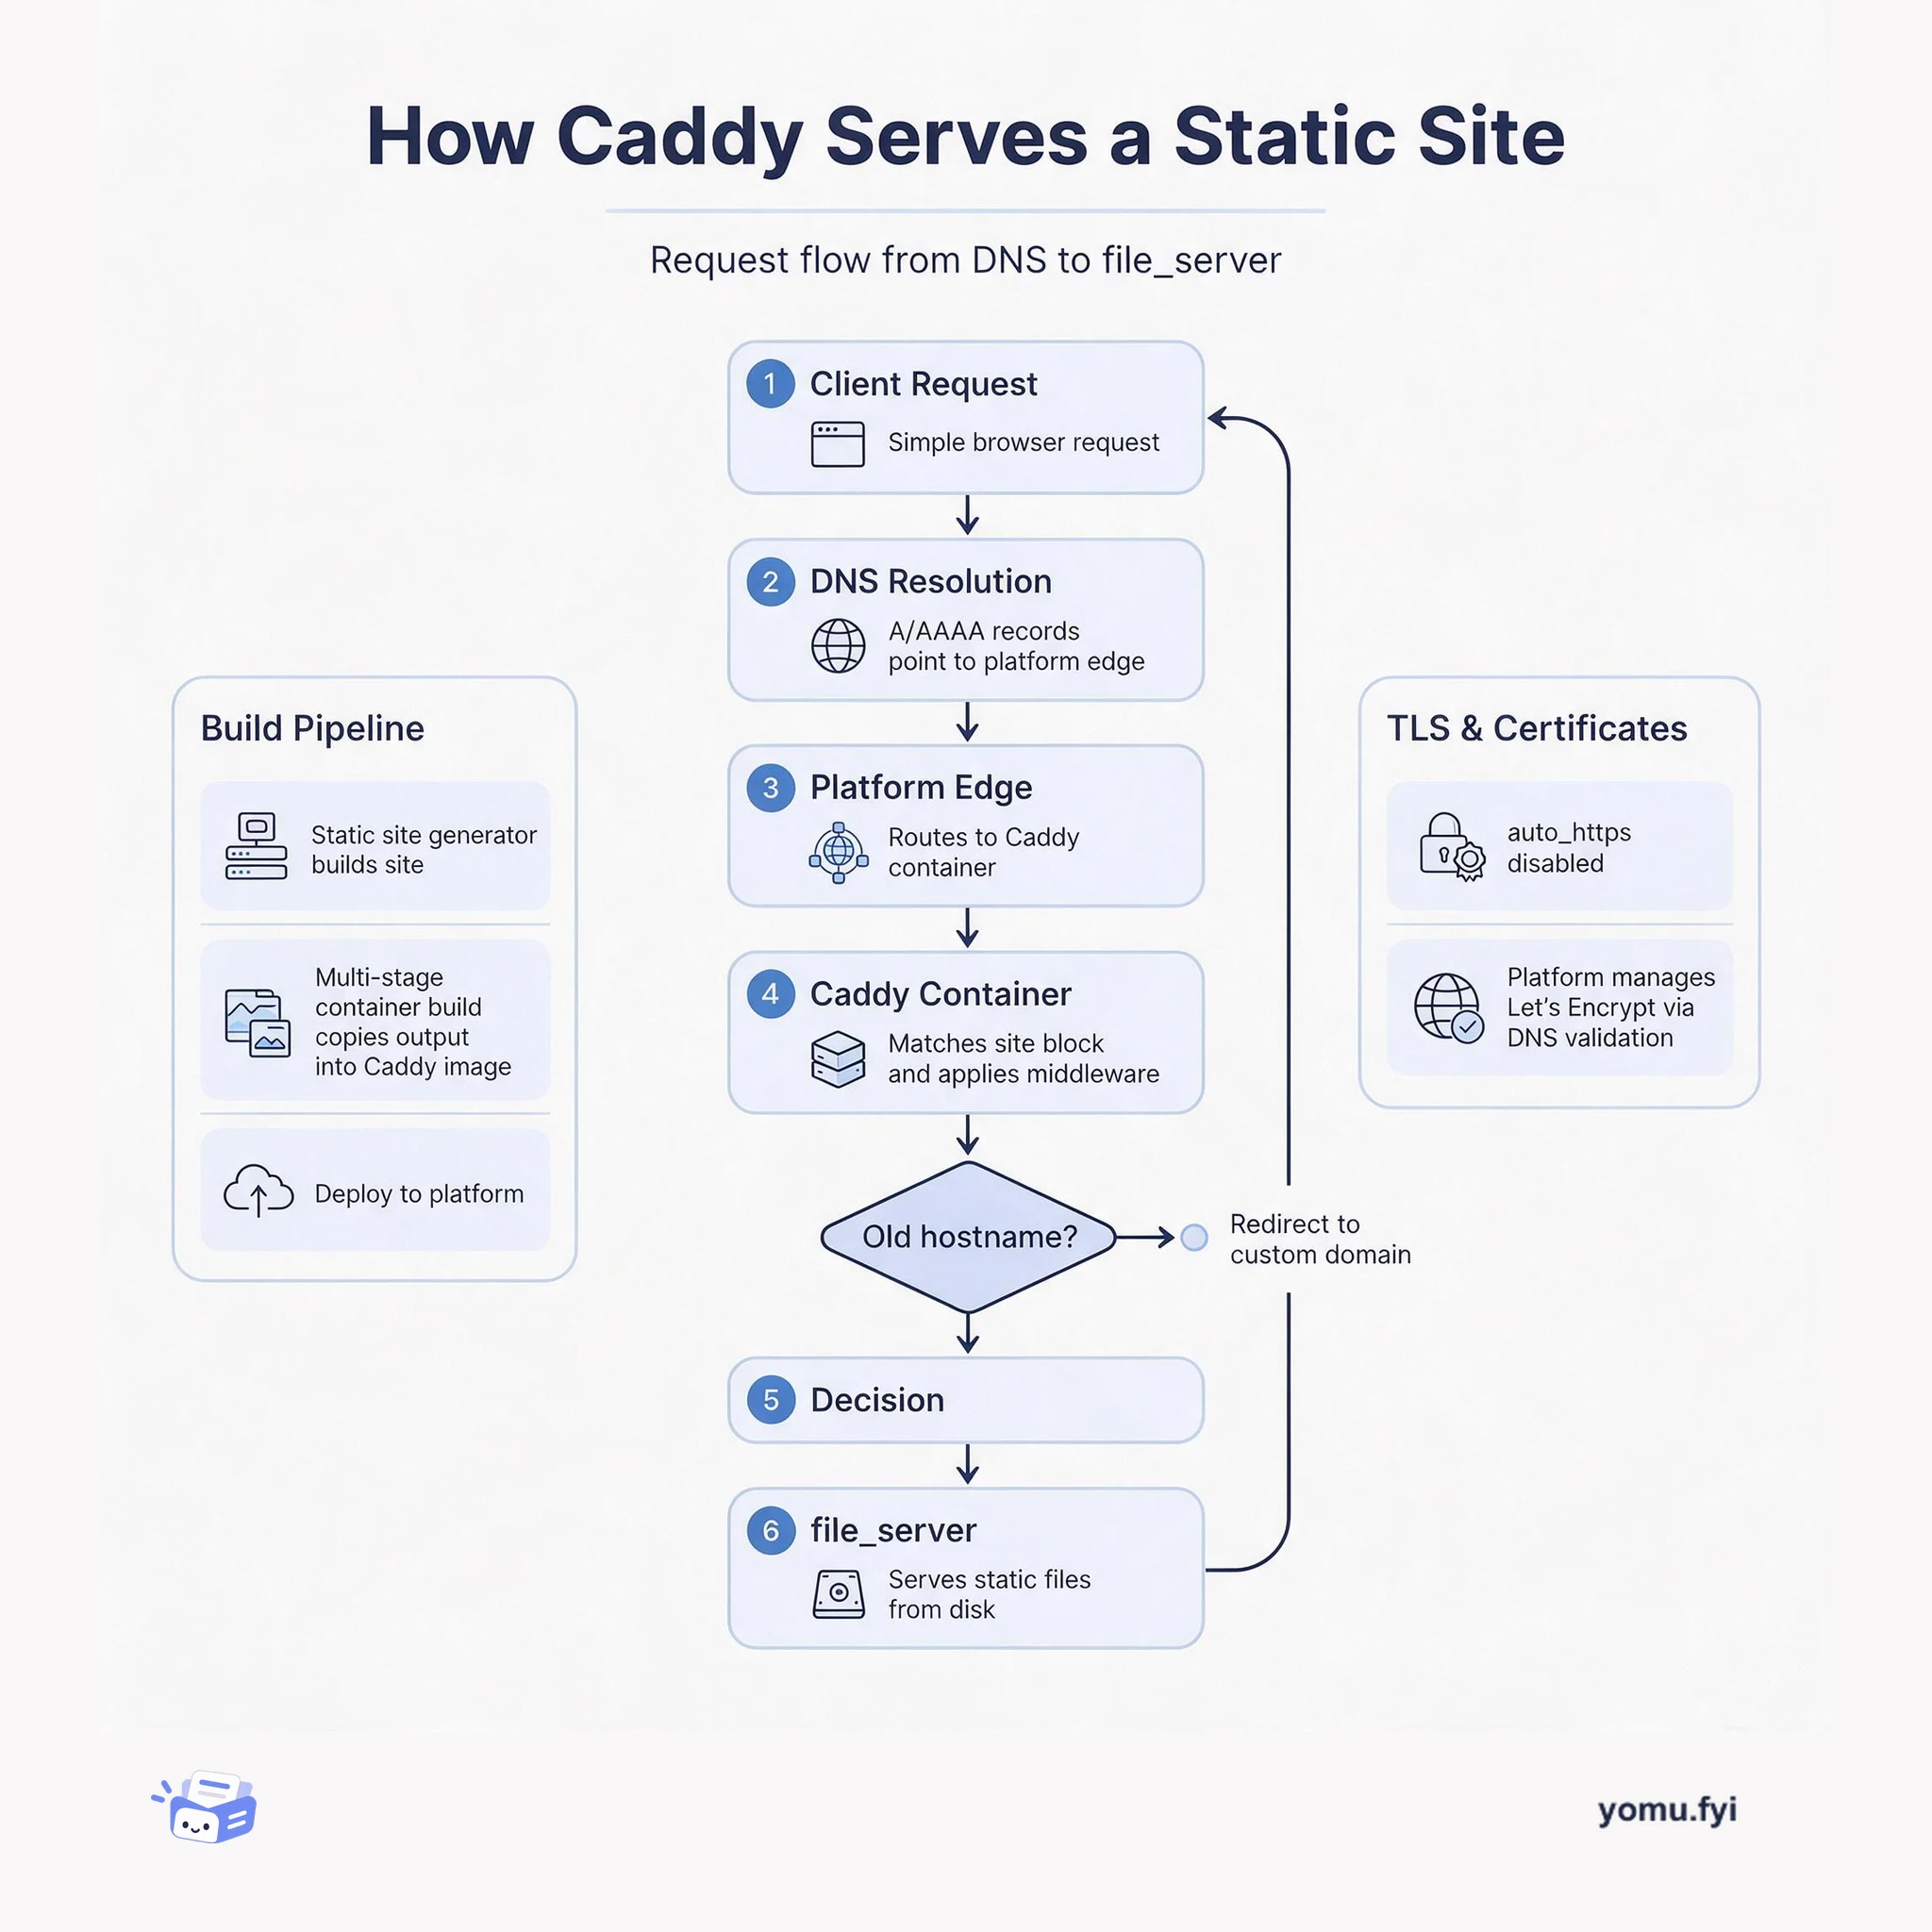
See how Caddy handles a request for a static site, from DNS resolution through container routing to file_server, and how TLS and redirects fit into the flow.
The Good Stuff
Paid picks we use ourselves. Links carry a referral code — a subscription through one earns us a commission at no extra cost to you.
One useful email. Unsubscribe anytime.