How MaaS Governance Wraps a Model Endpoint on AKS
A model deployed on AKS is open by default. See how MaaS policies insert Authorino authentication and Limitador rate limits in front of vLLM, so bad keys and over-quota requests stop at the gate.
 AWSSinisa MikasinovicTutorial
AWS Resilience Hub’s Next generation, announced September 18, 2026, adds three capabilities to align workload scope and resilience requirements with running environments. Amazon EKS label support selects Kubernetes resources using existing labels with AND logic, establishing precise resource boundaries without reorganizing namespaces. Generative AI-powered Dependency Insights summarizes discovered dependencies and highlights patterns warranting resilience review, such as cross-Region dependencies questioning recovery design. Resilience policy sharing through AWS Organizations lets a central team define requirements once and make them available to member accounts, with policy events tracking adoption. The post walks through scoping a checkout service on EKS using labels, examining dependencies via synthetic traffic, and applying a shared tier-1-critical policy with a 99.9% availability SLO, 5-minute multi-AZ RTO, 1-minute RPO, 15-minute multi-Region RTO, and 60-minute backup intervals.
Keeping workload scope and resilience requirements aligned with running environments, especially in shared Kubernetes clusters where resource boundaries are unclear and dependencies change after migrations or deployments.
Use Amazon EKS label selectors to filter Kubernetes resources within namespaces for precise service scoping, employ Generative AI-powered Dependency Insights to summarize and highlight discovered dependencies for resilience review, and share resilience policies across AWS Organizations to centralize requirements and track adoption.
EKS label selectors use AND logic within a namespace; without a selector, all supported objects in selected namespaces are discovered.
Dependency Insights can be regenerated once every 24 hours and uses DNS activity to discover endpoints, but connections made directly by IP address are not discovered.
A shared policy attachment event confirms adoption, not compliance; a failure mode assessment and resilience testing are needed to determine if the service meets targets.
Label selectors filter Kubernetes resources within selected namespaces using a key, operator, and values. Selectors within a namespace use AND logic: an object must match all of them. Without a selector, all supported objects in the selected namespaces are discovered.
Connections made directly by IP address aren't discovered, AWS Lambda functions need VPC connectivity to be covered, and very infrequent calls might not appear in initial results. Results reflect the history available to the service.
No, a policy attachment event confirms adoption, not compliance. After applying a shared policy, the console changes each target to 'Pending failure mode assessment,' and a failure mode assessment and appropriate resilience testing are needed to determine whether the service meets those targets.
Summaries are generated from the original by a language model. Check the original before relying on it.
See the idea
A model deployed on AKS is open by default. See how MaaS policies insert Authorino authentication and Limitador rate limits in front of vLLM, so bad keys and over-quota requests stop at the gate.
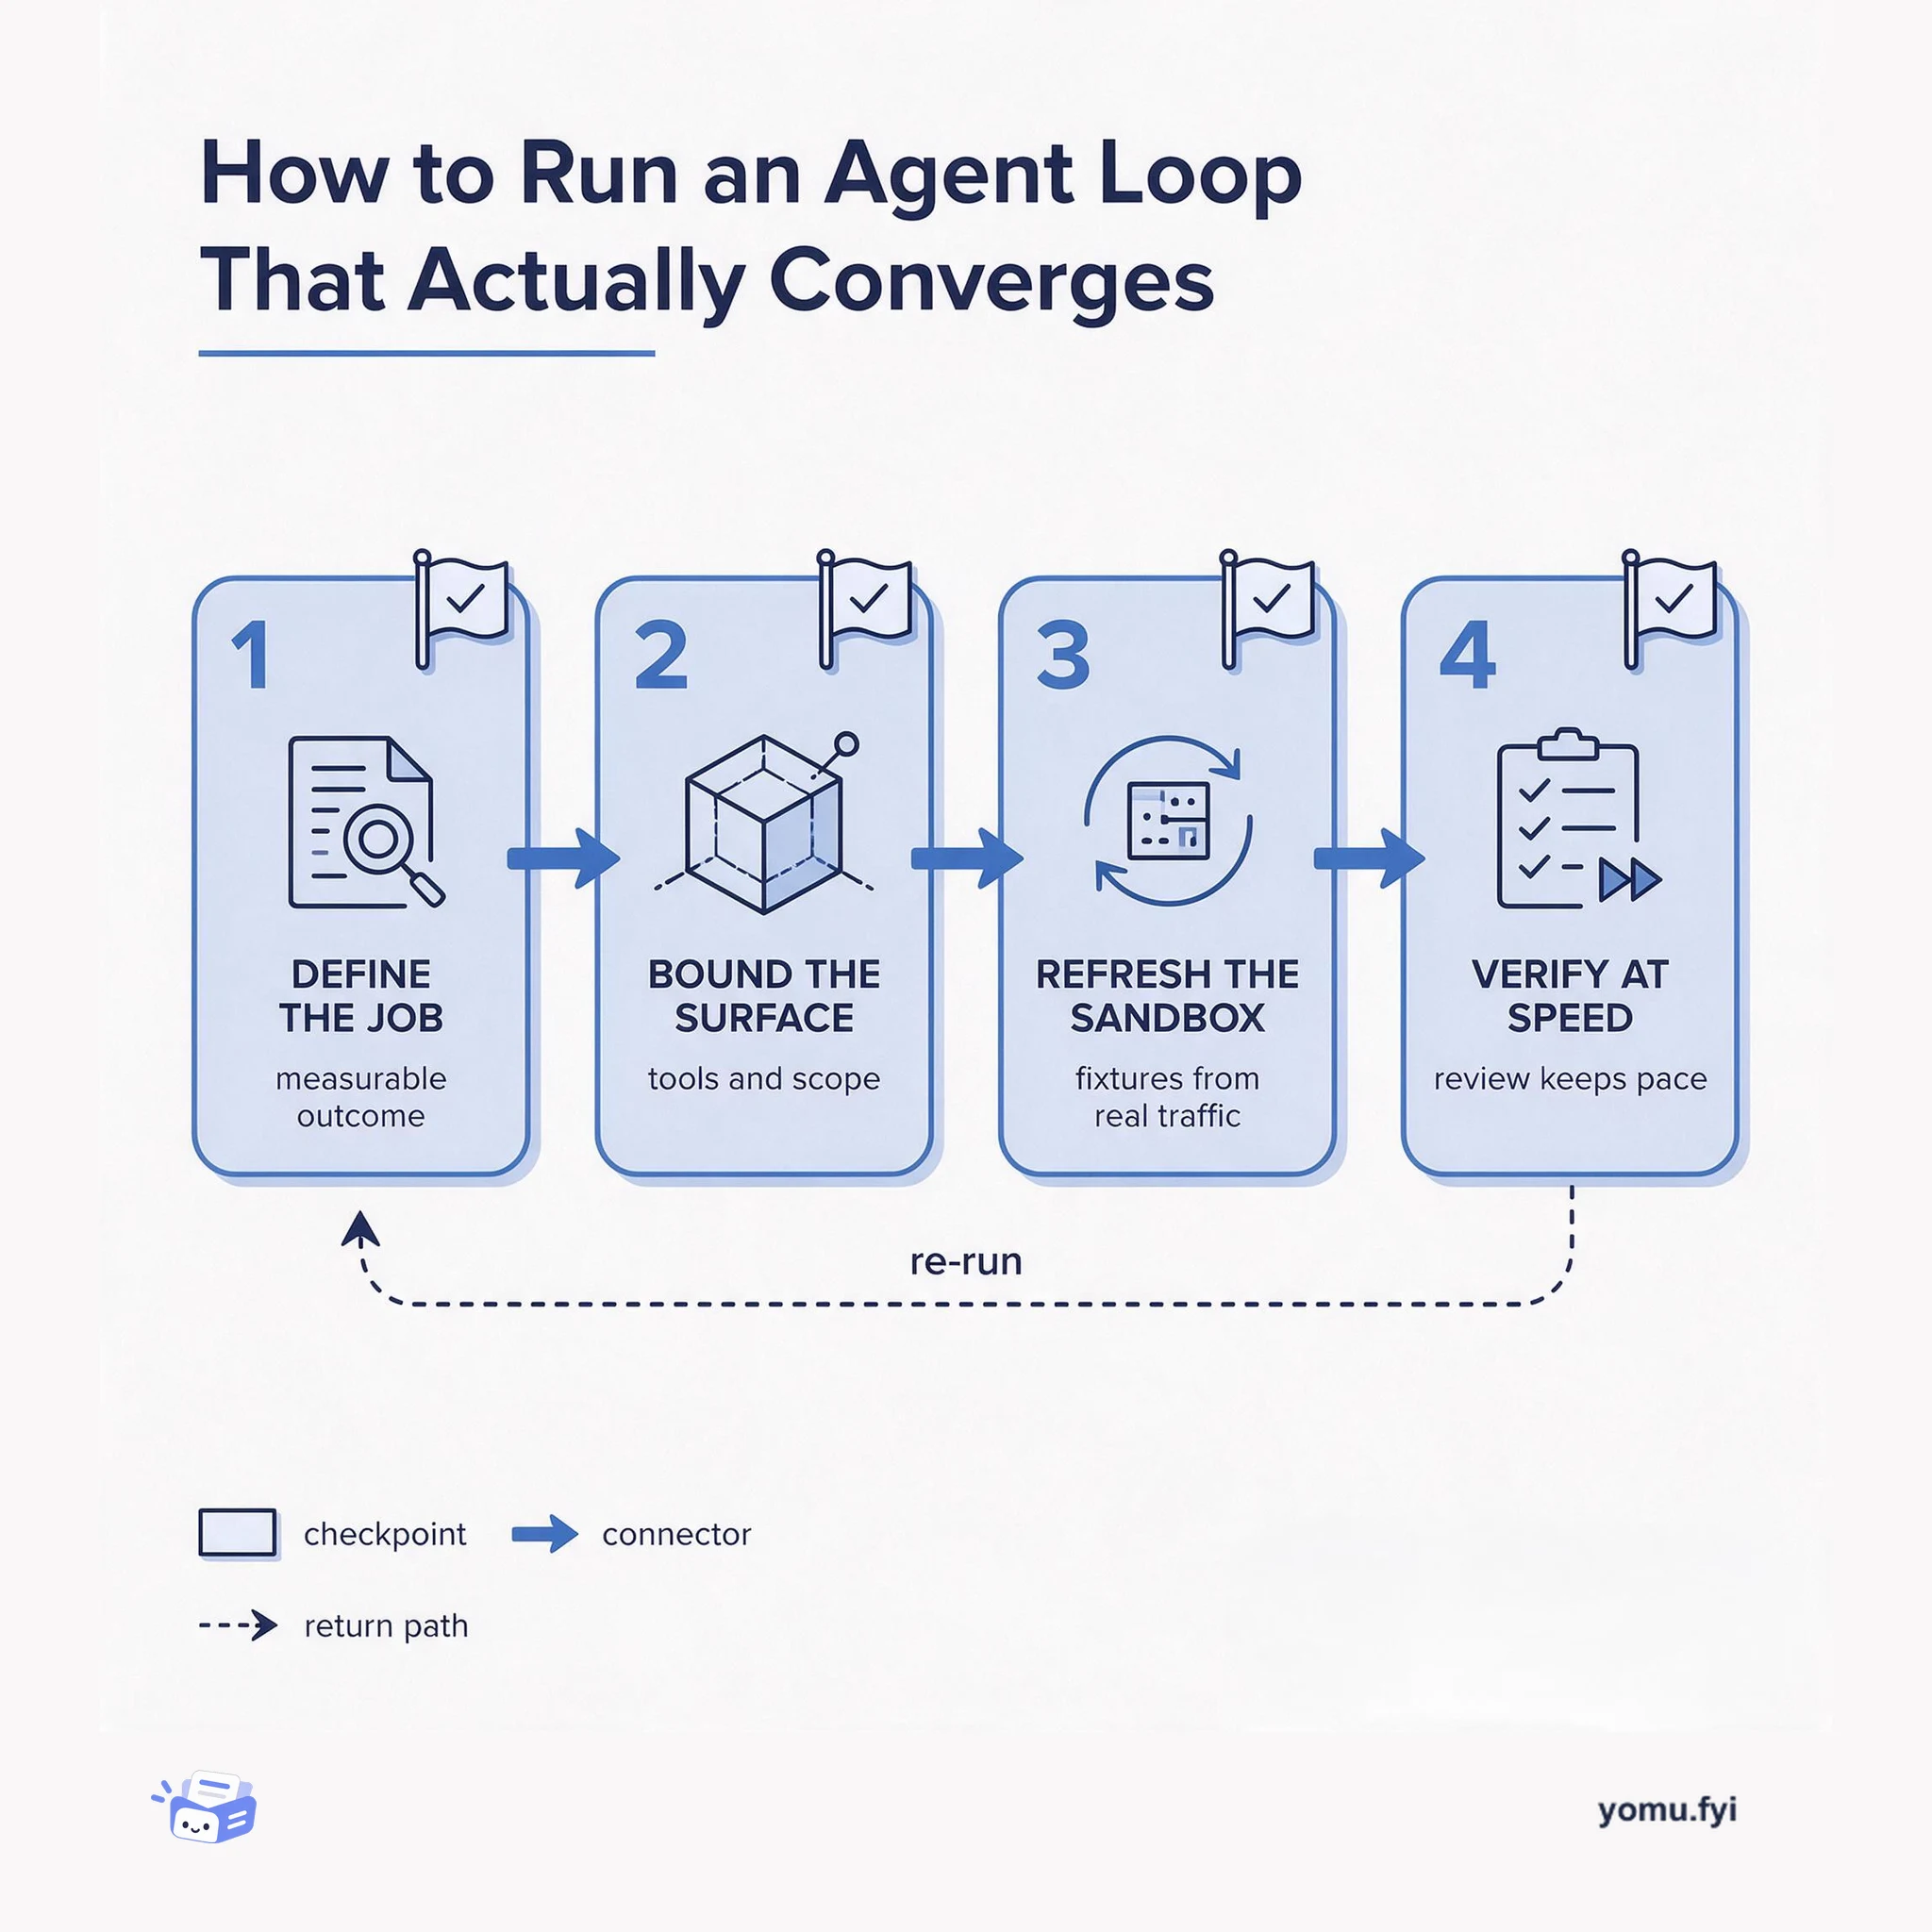
A four-checkpoint how-to for agent loops: name a measurable job, bound the tool surface, refresh sandbox fixtures from real traffic, and verify at agent speed.
Keep reading
The Good Stuff
Paid picks we use ourselves. Links carry a referral code — a subscription through one earns us a commission at no extra cost to you.
One useful email. Unsubscribe anytime.